Finding Low Hanging Fruit with Kali
Explore Kali Linux for identifying and exploiting common security vulnerabilities, including unnecessary services, weak passwords, and web-based admin interfaces.
Mutillidae Jeremy Druin Part 2
Learn to install and configure Mutillidae, explore security levels, and understand OWASP Top 10 vulnerabilities with expert guidance from Jeremy Druin.
The Benefits in Externalizing DMZ as a Service in the Cloud
Explore the benefits of cloud-based DMZ services, covering web architecture, security measures, and application firewalls. Learn about attack types and secure development practices.
Surfing the Sea and Drowning in Tabs - An Introduction to Cross Site Request Forgery
Explore Cross-Site Request Forgery (CSRF) attacks, their impact on web security, and effective prevention strategies in this comprehensive introduction.
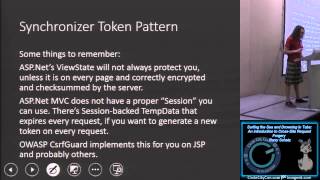
Surfing the Sea and Drowning in Tabs - An Introduction to Cross Site Request Forgery
Explore Cross Site Request Forgery: its mechanisms, prevention strategies, and real-world implications. Learn about same-origin policy, viewstate, headers, and encrypted token patterns.
Why the Web is Broken
Explore the vulnerabilities and flaws in web security, understanding why the internet remains susceptible to attacks and breaches despite ongoing efforts to secure it.
Attacking OWASP - Exploiting the Top 10
Explore OWASP Top 10 vulnerabilities through hands-on demonstrations, learning practical exploitation techniques and essential web security concepts for effective penetration testing.
Introducing the OWASP API Security Project
Explore OWASP API Security Project, covering key vulnerabilities and best practices for securing APIs. Learn about data sanitization, access control, and preventing sensitive data exposure.
Red Team Madness - Or How I Learned To Stop Worrying and Expect Pentester Mistakes
Explore red team tactics, pentester mistakes, and effective defensive strategies. Learn to detect and respond to various attack techniques, from encrypted drives to brute force attempts.
Web Security for Dummies
Learn essential web security practices, including password management, browser safety, Tor usage, and system patching. Enhance your online protection skills with expert guidance.
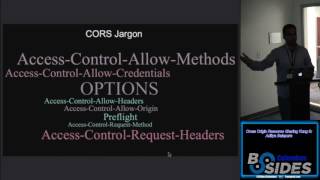
Cross Origin Resource Sharing Kung Fu
Explore Cross-Origin Resource Sharing (CORS) security implications, common developer mistakes, and best practices for implementing secure web applications.
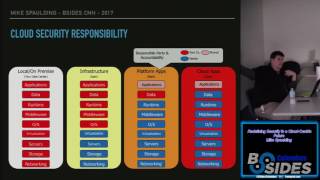
Redefining Security in a Cloud Centric Future
Explore cloud security challenges and solutions for various user types, covering data protection, API security, encryption, and compliance in a cloud-centric future.
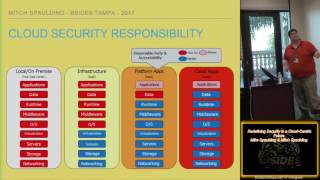
Redefining Security in a Cloud Centric Future
Explore cloud security challenges, responsibilities, and best practices in a rapidly evolving digital landscape. Learn about data protection, API security, and compliance risks in multi-tenant environments.
Mozilla's Tips on Strong HTTPS
Learn Mozilla's top tips for implementing strong HTTPS, including perfect forward secrecy, public key pinning, and certificate trust. Gain insights on maintaining privacy and security in web communications.
Choose Django for Secure Web Development
Learn why Django excels in secure web development, covering key security features and best practices to protect against common vulnerabilities and threats.
Web Hacking 101 - Hands on with Burp Suite
Hands-on workshop exploring web security vulnerabilities using Burp Suite. Practice identifying and exploiting common threats like cross-site scripting and SQL injection in a controlled environment.
Lessons Learned from a OWASP Top 10 Datacall
Explore insights from OWASP Top 10 Datacall, covering attribution, tools vs. humans, tech complexity, survey results, and vulnerability patterns for improved application security.
Serverless Security Top 10
Explore top 10 serverless security risks, their impact, and mitigation strategies. Gain insights into cloud evolution and emerging vulnerabilities in serverless architectures.
API Security Tokens Flows and the Big Bad Wolf
Explore API security, authorization flows, and authentication methods to protect digital resources from potential threats and ensure secure access in modern applications.
Understanding XSS
Comprehensive exploration of Cross-Site Scripting (XSS) vulnerabilities, covering detection, exploitation, and mitigation strategies for web application security professionals.
Of CORS It's Exploitable - What's Possible with Cross-Origin Resource Sharing
Explore Cross-Origin Resource Sharing (CORS), its vulnerabilities, and exploitation techniques. Learn about REST, authentication, and effective CORS defenses in web security.