Bypassing Browser Security Policies for Fun and Profit
Explore mobile browser vulnerabilities and security policy bypasses, including Same Origin Policy and Content Security Policy. Learn testing methodologies and see real-world examples of Android browser exploits.
Your Scripts In My Page - What Could Possibly Go Wrong?
Explore the security risks of cross-domain script inclusion, including potential data leaks and account compromises. Learn detection methods and defensive measures to protect against these vulnerabilities.
Automated Detection of Firefox Extension-Reuse Vulnerabilities
Discover a novel extension-reuse vulnerability in Firefox and learn about CROSSFIRE, a static analyzer that detects these vulnerabilities and generates exploit templates for rapid proof-of-concept creation.
Browsers Gone Wild
Unveiling creative browser vulnerabilities and attacks, including confidentiality breaches, login detection, and exploiting HTML5 features, with live demonstrations challenging Same Origin Policy understanding.
Understanding the Attack Surface and Attack Resilience of Project Spartan's New EdgeHTML Rendering Engine
Explore EdgeHTML's attack surface, compare it with MSHTML, and analyze exploit mitigations in Windows 10's new rendering engine for enhanced web security understanding.
Compromising Web Servers and Defensive Techniques
Explore web server vulnerabilities and learn defensive strategies to protect against common attacks and security breaches in this comprehensive cybersecurity presentation.
HTTP Fingerprinting and Advanced Assessment Techniques
Explore advanced HTTP fingerprinting techniques and assessment methods for enhanced web security and vulnerability detection.
WAF Bypass In Depth
Explore advanced techniques for bypassing Web Application Firewalls (WAFs) and demonstrating the impact of cross-site scripting vulnerabilities, even in the presence of sophisticated security measures.
Blindspots
Robert Hansen shares insights on overlooked areas in web application and browser security, challenging industry professionals to broaden their thinking and address critical blindspots.
Next Gen Web Pen Testing - Handling Modern Applications in a Penetration Test
Explore modern web application security with insights on WebSockets, REST APIs, and Content Security Policy. Learn practical penetration testing techniques for next-gen web technologies.

To CORS - The Cause of and Solution to Your SPA Problems
Explore CORS issues in Single Page Applications, their causes, and effective solutions for improved web development and security.
Pavlovian Security - How To Change the Way Your Users Respond When the Bell Rings
Learn to influence user behavior for better security through Pavlovian techniques. Explore motivations, failures, and practical strategies to raise awareness and create secure habits in your organization.
The 3 Way Bypass Surgery - Abusing Content Delivery Networks with Server Side Request Forgery - SSRF
Explore advanced techniques for bypassing security measures using Server Side Request Forgery (SSRF) and Content Delivery Networks (CDNs) in this comprehensive cybersecurity presentation.
A Heaven for Hackers - Breaking Web Security Virtual Appliance
Explore web security vulnerabilities and hacking techniques through hands-on demonstrations, focusing on methodology, enumeration, and exploitation of common weaknesses in web applications.
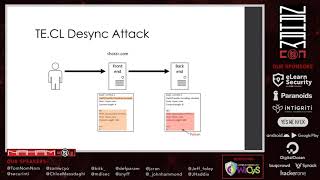
Practical Attacks Using HTTP Request Smuggling
Explore practical HTTP request smuggling attacks, including CL.TE/TE.CL desync techniques, testing methods, and real-world examples. Learn to exploit vulnerabilities for session stealing and response queue poisoning.
Hacking IIS
Explore advanced IIS hacking techniques, including HTTPAPI 2.0 assets, VHost hopping, local file disclosure, and complex XXE vectors. Learn to leverage tools like DNSpy for effective web application security testing.
Using Chromedp to Hunt for Prototype Pollution
Learn to use Chromedp in Go for detecting prototype pollution at scale, enhancing your ability to identify and address this client-side security vulnerability efficiently.
EmPoWeb - Empowering Web Applications with Browser Extensions
Explores security risks of browser extension APIs, revealing how web apps can exploit them to bypass SOP, access sensitive user data, and perform privileged actions on users' devices.
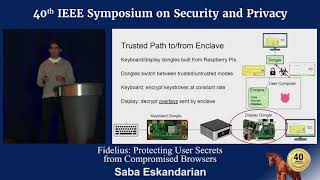
Fidelius - Protecting User Secrets from Compromised Browsers
Innovative architecture using trusted hardware enclaves to protect sensitive user data during web browsing, even in fully compromised environments. Offers secure form data, JavaScript, XMLHttpRequests, and storage solutions.
A Deep Learning Approach to Fast, Format-Agnostic Detection of Malicious Web Content
Innovative deep learning method for detecting malicious web content, operating on token streams from static HTML files. Achieves high accuracy and speed without complex parsing or emulation.
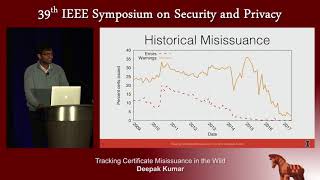
Tracking Certificate Misissuance in the Wild
Explore certificate misissuance trends, introducing ZLint tool to analyze CA errors. Discover improvements, persistent issues, and correlations with mismanagement in the Web PKI ecosystem.