Facebook's Approach to Common Web Vulnerabilities
Explore Facebook's strategies for combating web vulnerabilities, including XSS, CSRF, and SQL injection, through security libraries, automated detection, and lint rules.
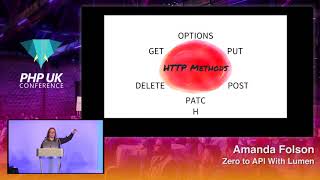
Zero to API with Lumen
Learn to build efficient APIs using PHP and Laravel's Lumen framework. Covers API design best practices, microservices, REST principles, and practical implementation steps for creating maintainable and user-friendly APIs.
JWT - To Authentication & Beyond
Explore JSON Web Tokens for smart, self-contained authentication in distributed systems. Learn claims, use cases, and best practices for secure and efficient token management.
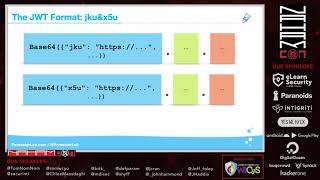
JWT JKU and X5U Equals Love
Explore JWT vulnerabilities related to jku and x5u headers, understanding potential security risks and exploitation techniques in web applications.
TruffleHog Chrome Extension - Open CORS in SAAS API's Lead to Leaky Keys
Discover API keys hidden in web pages with the open-source TruffleHog Chrome extension. Learn how to use this tool and explore real-world examples of exposed keys in SaaS APIs with open CORS.
Hell on Earth - From Browser to System Compromise
Explore cutting-edge browser exploitation techniques and kernel vulnerabilities from Pwn2Own 2016. Analyze attack vectors, root causes, and remediation strategies for achieving system-level access.
Abusing Bleeding Edge Web Standards for Appsec Glory
Explore risks and mitigation strategies for modern web security standards like SRI, CSP, and HPKP. Learn about implementation challenges, trade-offs, and potential exploits in legacy applications.
Web Application Firewalls - Analysis of Detection Logic
Explores detection logic in Web Application Firewalls, focusing on regular expressions. Analyzes security flaws in popular WAFs and introduces tools for identifying vulnerabilities in regex patterns.
Crippling HTTPS with Unholy PAC
Explore how malicious Proxy AutoConfiguration can compromise HTTPS security, leak sensitive data, and enable cross-platform attacks, even on secure networks and browsers.
Exploiting IPC With New Desynchronization Primitives
Exploración de vulnerabilidades críticas en SAP, demostrando técnicas avanzadas de explotación HTTP y desincronización para comprometer sistemas empresariales. Incluye demostraciones prácticas y análisis de impacto en la seguridad global.
Certificate Transparency Logs - Roadmaps to Riches or Ruin?
Explore the dual nature of Certificate Transparency Logs in Web PKI: their role in ensuring certificate authenticity and potential misuse by malicious actors for reconnaissance.

WebAuthn, Yubikeys, and You - What We Wish We Knew Before Rolling Out WebAuthn for Internal Use
Insights from Discord's implementation of WebAuthn and Yubikeys for enhanced internal security. Learn about challenges, best practices, and lessons learned in deploying FIDO2/WebAuthn as a superior MFA solution.
Tokens, Everywhere!
Hands-on deep-dive into Azure AD's OAuth implementation, covering JWT, token types, and attack scenarios. Learn to secure environments and detect token abuse.
Oops, That Wasn't Supposed to Happen - Bypassing Internet Explorer's Cross Site Scripting Filter
Explore techniques to bypass Internet Explorer's XSS filter, uncovering vulnerabilities and enhancing web security knowledge.
Beyond Passwords - How WebAuthn Actually Works
Explore WebAuthn as a secure alternative to passwords, diving into its implementation, hardware token usage, and underlying cryptography for enhanced web authentication.
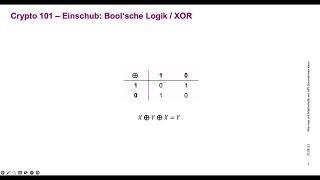
Wie man mit Mathematik ein API übernehmen kann - und wie gute Architektur das verhindert
Entdecken Sie, wie mathematische Schwachstellen in der Kryptographie zur Übernahme eines API-Gateways führen können und lernen Sie Strategien zur Verhinderung solcher Angriffe durch defensive Architektur.
Back to Basics - HTTP Cookies
Explore HTTP cookies' origins, behavior, and recent developments. Gain insights into security, tracking, and privacy implications for modern web development.
Knock Knock, Who's There? Authenticating Your Single Page Apps Using JSON Web Tokens
Explore authentication challenges in single page apps and learn how to implement secure solutions using OpenID Connect and JSON Web Tokens for seamless user experiences.
From Zero to Microprofile Hero - Let's Dive into a Microservices World
Hands-on exploration of MicroProfile for building efficient, portable microservices in Java. Learn key features like monitoring, security, configuration, and resilience through live coding examples.
Black Clouds and Silver Linings in Node.js Security
Explore Node.js security challenges, mitigation strategies, and practical measures for building secure applications. Learn about OWASP Top 10 issues and recent security initiatives in the Node.js ecosystem.
How to Get Along with HATEOAS Without Letting the Bad Guys Steal Your Lunch
Explore secure HATEOAS implementation for RESTful web services, balancing design flexibility with cybersecurity. Learn practical steps to protect against exploits while leveraging dynamic client-server interactions.