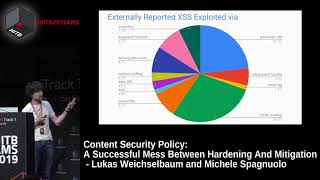
A Successful Mess Between Hardening and Mitigation
In-depth analysis of Content Security Policy for XSS prevention, exploring its effectiveness, debunking myths, and sharing real-world data on successful XSS mitigation in sensitive applications.
Web Applications Bug Hunting - Fundamentals
Explore web application security fundamentals, attack vectors, and tools for bug hunting. Learn key concepts to kickstart your career in application security.
XSS Mitigation - The State of the Art
Comprehensive overview of XSS attacks and modern defense strategies, covering browser-based, server-side, and framework-specific mitigations for web developers and security professionals.

Navigating Passwordless Authentication with FIDO2 & WebAuthn
Explore FIDO2 and WebAuthn standards for passwordless authentication, learn implementation strategies, and discover how to enhance security while improving user experience.
No More XSS - Deploying CSP with Nonces and Strict-Dynamic
Learn to implement Content Security Policy with nonces and strict-dynamic to prevent XSS attacks. Discover practical deployment strategies for Pinterest and Instapaper, and understand potential vulnerabilities.
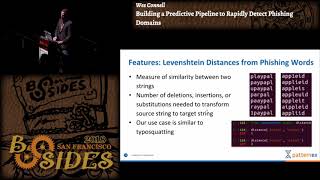
Building a Predictive Pipeline to Rapidly Detect Phishing Domains
Learn to build a predictive pipeline using Python and machine learning to detect phishing domains in real-time, leveraging Certificate Transparency logs and supervised learning techniques.
All Your Containers Are Belong to Us
Explore container orchestration security risks, focusing on exposed management nodes and APIs. Learn implications, recommendations, and see demonstrations of potential exploits in popular platforms.
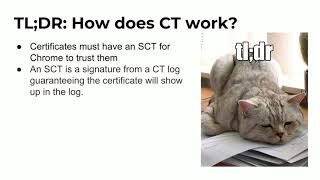
Cats in My Certificate Transparency Logs
Explore Certificate Transparency logs: their purpose, functionality, and potential misuse. Learn about SCTs, public keys, and novel applications, including finding cat pictures online.
Hacking with a Heads Up Display
Explore OWASP ZAP's Heads Up Display, a browser-integrated security testing tool designed to make security testing more accessible and user-friendly for developers, QA, and hackers.
Offensive Javascript Techniques for Red Teamers
Explore advanced JavaScript techniques for red team operations, including browser exploitation, network reconnaissance, and crafting payloads to target internal vulnerabilities quickly and effectively.
Exploiting CSP in WebKit to Break Authentication and Authorization
Uncover a critical WebKit vulnerability that compromises authentication and authorization in web applications, exposing weaknesses in browser security features and their implementation.
Edge Side Include Injection - Abusing Caching Servers into SSRF and Transparent Session Hijacking
Explore Edge Side Include injection, a web attack vector exploiting caching servers. Learn how this legacy technology can lead to SSRF and session hijacking vulnerabilities in modern web infrastructure.
Battle of Windows Service - A Silver Bullet to Discover File Privilege Escalation Bugs Automatically
Discover file privilege escalation bugs automatically in Windows services using Advanced Local Procedure Call analysis and process monitoring techniques for enhanced system security.
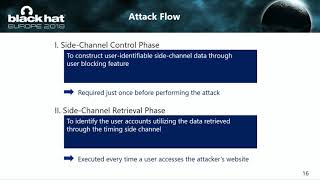
I Block You Because I Love You - Social Account Identification Attack Against a Website Visitor
Practical side-channel attack to identify social web service accounts of website visitors, compromising anonymity through user profiles and activities.
Cutting Edge - Microsoft Browser Security — From People Who Owned It
Deep dive into Microsoft Edge security architecture, exploring sandbox initialization, browser broker implementation, and renderer security isolation.
AutoSpear - Towards Automatically Bypassing and Inspecting Web Application Firewalls
Explore techniques for automatically bypassing and inspecting web application firewalls, examining vulnerabilities in WAF-as-a-service solutions and cloud security services.
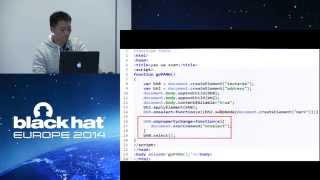
The Power of Pair - One Template that Reveals 100+ UAF IE Vulnerabilities
Discover a unique fuzzing strategy that revealed over 100 IE use-after-free vulnerabilities. Learn about the vulnerability hunting system and techniques used to find critical browser security flaws.
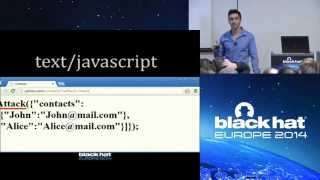
Same Origin Method Execution - Exploiting a Callback for Same Origin Policy Bypass
Explore a powerful web attack technique that exploits JSONP to bypass Same Origin Policy, potentially compromising entire domains without user interaction or typical browser protections.
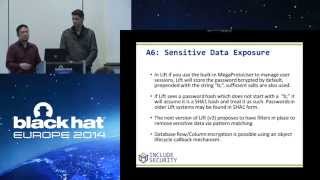
Scala Security - Examining the Play and LiftWeb Frameworks
Explore security aspects of Scala's Play and LiftWeb frameworks, including OWASP Top 10 vulnerabilities, exploitation mitigations, and a new Scala library for SSRF prevention.
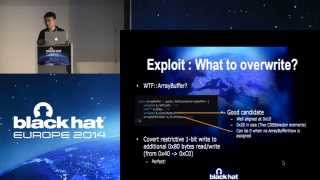
WebKit Everywhere - Secure or Not?
Explore WebKit security, vulnerabilities, and exploitation techniques across platforms. Learn about security enhancements, mitigation strategies, and advanced exploit methods with real-world demos.
Session Identifier are for Now, Passwords are Forever - XSS-Based Abuse of Browser Password Managers
Explore XSS-based attacks on browser password managers, their vulnerabilities, and potential solutions. Learn about password field usage on popular websites and get recommendations for protection.