Modern and Secure IAM for Modern Applications
Explore modern IAM strategies for enhanced application security, covering OpenID, JSON Web Tokens, SAML, and FIDO protocols, with practical insights and a demo.
The State of Credential Stuffing and the Future of Account Takeovers
Explore credential stuffing, account takeovers, and evolving cybersecurity threats. Learn about attack methods, defense strategies, and the future of online fraud prevention.
XSS is Dead - We Just Don't Get It
Exploración crítica de la persistencia del XSS, analizando su historia, fracasos en su mitigación y factores que contribuyen a su continuidad. Se cuestiona su relevancia actual y se proponen reflexiones sobre el futuro de la seguridad web.
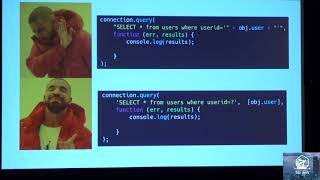
OWASP Top 10 for JavaScript Developers
Explore JavaScript vulnerabilities in OWASP Top 10, covering client and server-side issues with focus on modern frameworks and NodeJS. Learn prevention techniques for secure web development.
Testing and Hacking APIs
Learn techniques for testing and exploiting API vulnerabilities, including understanding implementation, detecting weak points, and conducting effective penetration tests on modern applications.
DevSecOps with OWASP DevSlop
Learn DevSecOps through hands-on examples with OWASP DevSlop. Explore secure component management, secret handling, testing techniques, and open-source tools to enhance your pipeline security.
Common API Security Pitfalls
Explore common API security pitfalls, their root causes, and best practices for protection. Learn to assess and improve API security, focusing on authentication, encryption, and input validation.
Temporal - Code-Origin Policy - Towards a Formal User Privacy Protection for the Web
Explore a novel approach to web privacy protection through code-origin monitoring, offering customizable user safeguards and formal assurance mechanisms for JavaScript execution.
Extending WAFs at the Application Layer
Explore application-level security control with Sanwaf, an alternative to traditional WAFs. Learn its structure, datatypes, and implementation for enhanced web application protection.
Insecure Deserialization, and How Not to Do It
Explore secure deserialization techniques and common vulnerabilities with practical demos, focusing on session cookies and big vulnerabilities in various platforms.
Restricting the Scripts, You're to Blame, You Give CSP a Bad Name
Explore Content Security Policy's role in web security, covering script restrictions, TLS enforcement, and framing control. Learn best practices and developer insights for effective CSP implementation.
Practical OWASP CRS in High Security Settings
Learn to implement OWASP Core Rule Set for high-security web applications, covering WAFs, ModSecurity, logging, whitelisting, and advanced protection techniques.
OWASP Flagship Projects - OWASP ModSecurity Core Rule Set
Explore OWASP ModSecurity Core Rule Set: web application firewall rules, paranoia levels, and project developments for enhanced security and threat protection.
OWASP Standard Classification - API Security Top 10 - A Beginner's Guide to Mitigation
Learn to mitigate API security risks using OWASP's Top 10 classification. Explore vulnerabilities, solutions, and strategies for implementing robust API security throughout the entire lifecycle.
OWASP Standard Classification - Rough Consensus - An OWASP Story
Explore OWASP's journey in establishing software security standards through rough consensus, highlighting challenges, achievements, and future directions in the field.
Topics of Interest - Common NGINX Misconfigurations That Leave Your Web Server Open To Attack
Explore common NGINX misconfigurations, their security implications, and remediation strategies. Learn to identify and fix vulnerabilities in web server setups through demos and expert insights.
Automated Evasion Attacks and Fingerprinting Using Blackbox Differential Automata Learning
Automated evasion attacks and fingerprinting techniques using blackbox differential automata learning for evaluating web security products and analyzing TCP/IP implementations.

Host of Troubles - Multiple Host Ambiguities in HTTP Implementations
Explores HTTP host ambiguities in implementations, revealing vulnerabilities in caching, firewalls, and WAFs. Presents attacks exploiting these issues and discusses prevalence and mitigation strategies.
CSP is Dead, Long Live CSP! - On the Insecurity of Whitelists and the Future of the Content Security Policy
Explore the evolution and challenges of Content Security Policy, analyzing its effectiveness, vulnerabilities, and future directions in web security.
Evaluating the Effectiveness of Content Security Policy in the Wild
Evaluación de la efectividad de la Política de Seguridad de Contenido en la práctica, analizando su adopción, configuración y debilidades frente a ataques XSS.
CSPAutoGen - Black-box Enforcement of Content Security Policy upon Real-world Websites
Explore black-box enforcement of Content Security Policy on websites, covering deployment, training, rewriting, and evaluation of CSPAutoGen for enhanced web security.