Measurement and Analysis of Private Key Sharing in the HTTPS Ecosystem
Explore HTTPS ecosystem's private key sharing practices, risks, and implications for web security. Learn detection methods and analysis of key sharing among domains and hosting providers.
The "Web/Local" Boundary Is Fuzzy - A Security Study of Chrome's Process-based Sandboxing
Explore Chrome's process-based sandboxing, its security implications, and potential vulnerabilities in web browser architecture. Learn about attacks exploiting the fuzzy web/local boundary.
Tired of Playing Exploit Kit Whack-A-Mole? Let's Automate
Explore automated detection of Exploit Kits using headless browsers, JavaScript, and DOM inspectors for efficient web crawling and analysis of malware delivery techniques.
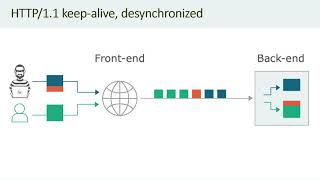
HTTP Desync Attacks - Request Smuggling Reborn
Explore HTTP request smuggling techniques to bypass security, manipulate web infrastructure, and exploit vulnerabilities. Learn detection, confirmation, and exploitation methods for various attack scenarios.

WebAuthn 101 - Demystifying WebAuthn
Demystifying WebAuthn: Learn about its use cases, implementation, and future developments in web authentication, essential for any service implementing user login.
Attacking Client-Side JIT Compilers
Explore JIT compiler security in JavaScript engines, focusing on challenges, solutions, and potential vulnerabilities. Learn about optimization techniques and their impact on browser exploitation.
A New Era of SSRF - Exploiting URL Parser in Trending Programming Languages
Explore a new SSRF exploit technique targeting URL parsers in popular programming languages. Learn about protocol smuggling, fuzzing tools, and discover vulnerabilities in widely-used libraries.
HTTP Request Smuggling in 2020 - New Variants, New Defenses and New Challenges
Explore new variants, defenses, and challenges of HTTP Request Smuggling, an attack technique exploiting interpretations of non-standard HTTP requests between client and server.
Web Cache Entanglement - Novel Pathways to Poisoning
Explore novel web cache poisoning techniques, probing cache inconsistencies to build sophisticated exploit chains. Learn to uncover vulnerabilities in caching systems across the internet.
API-Induced SSRF - How Apple Pay Scattered Vulnerabilities Across the Web
Explore API security vulnerabilities, focusing on Apple Pay's impact, with live demos and actionable strategies for improving defensive programming practices.
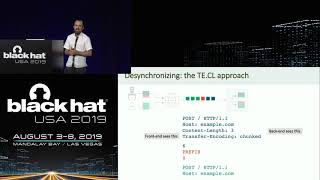
HTTP Desync Attacks - Smashing into the Cell Next Door
Explore techniques for HTTP request splicing, enabling remote attackers to manipulate web infrastructure, exploit visitors, and breach system isolation. Learn detection, case studies, and mitigation strategies.
Breaking XSS Mitigations Via Script Gadgets
Explore a novel web hacking technique that bypasses XSS mitigations using script gadgets. Learn about HTML sanitizers, CSP, and practical demonstrations of this powerful attack method.
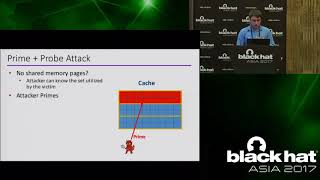
Cache Side Channel Attack - Exploitability and Countermeasures
Explore dangerous cache attacks, their characteristics, and real-world applications. Learn about exploitability, countermeasures, and key takeaways for protecting against these privacy-violating threats.
Uncovering Large Scale Fraud Operations
Uncover advanced fraud techniques targeting digital credentials and learn strategies to counter large-scale account takeover threats in the wake of accelerated digital transformation.
HackIM CTF - Do's and Don'ts
Explore CTF competitions: learn security through challenges in web, crypto, reverse engineering, and more. Gain insights on dos and don'ts for successful participation in HackIM CTF.
ECMA Script 6 from an Attacker's Perspective
Explore ECMA Script 6 from a security perspective, covering new language features, potential attack vectors, and strategies to mitigate risks in modern web browsers.
Introduction to the OWASP ModSecurity Core Rule Set
Learn about OWASP ModSecurity Core Rule Set, a powerful open-source web application firewall. Discover key features like paranoia levels and anomaly scoring, and see its effectiveness in protecting against various attacks.

Hunting Evasive Vulnerabilities - Finding Flaws That Others Miss
Explore techniques for uncovering elusive web vulnerabilities, from advanced methods to overlooked basics. Learn strategies to enhance your security auditing skills and find flaws others miss.
Delivering Secure, Client-Side Technology to Billions of Users
Explore Google's approach to securing Android for billions, covering encryption, app analysis, ecosystem collaboration, and update processes for a safer mobile experience.
How FIDO2 and WebAuthn Stop Account Takeovers
Explore FIDO2 and WebAuthn for robust user authentication, learn implementation strategies, and understand how these technologies prevent account takeovers and enhance security.
Getting API Security Right
Explore best practices for API security through real-world cases, covering attack surfaces, authorization issues, and practical guidelines to enhance your API's protection.