Why the LinkedIn Hack Could Be Your Biggest AppSec Threat
Explore account takeover threats, their long-term impact, and effective defense strategies. Learn about hacking techniques, credential stuffing, and tools to protect against evolving cyber risks.
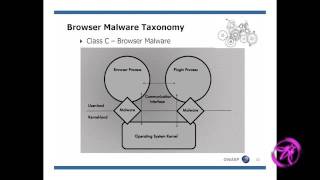
The Good Hacker - Dismantling Web Malware
Explore web malware anatomy, impact, and detection techniques. Learn about browser vulnerabilities, drive-by downloads, and real-world case studies of exploit kits and botnets.
SSL and the Future of Authenticity
Explore SSL's role in online security, challenges with certificate authorities, and innovative approaches to authentication in the digital age.
Implementing AppSensor in ModSecurity
Explore advanced web application security techniques using AppSensor and ModSecurity, focusing on detection points, SQL injection prevention, and innovative defense strategies.
Securing Modern API and Microservice Based Applications by Design
Learn to secure modern API and microservices architectures with expert insights on key concerns, architectural patterns, and actionable solutions for robust application security.
IoT and the Security of That Mobile App - Mark Loveless
Explore IoT security vulnerabilities in mobile apps, focusing on common mistakes, attack vectors, and research techniques. Learn to identify and exploit weaknesses in device-to-cloud communication.
Fixing XSS with Content Security Policy
Explore Content Security Policy (CSP) as a defense against XSS attacks, comparing CSP 1.0 and 2.0, and learn implementation strategies for enhanced web application security.
Railsgoat - Rails Attack and Defense
Explore RailsGoat, an OWASP project for Rails security training. Learn common vulnerabilities, remediation techniques, and attack scenarios aligned with the OWASP Top 10 using a purposely vulnerable Rails application.
Preventing Mobile App and API Abuse
Explore mobile app and API security threats, countermeasures, and defense-in-depth techniques through a courier service's evolving security approach against malicious attacks.
Working with Developers for Fun and Progress
Practical strategies for building strong relationships with developers to create an impactful AppSec program, featuring competition-based training, tooling implementation partnerships, and codebase contributions.
Authentication as a Microservice - Portable Customer Identity Management
Explore microservice-based authentication, portable identity management, and JWT security. Learn advantages, pitfalls, and best practices for decoupling user data in modern applications.
Breaking Fraud and Bot Detection Solutions
Demystifying browser fingerprinting and user behavior tracking in fraud detection, exploring vulnerabilities, and sharing real-world implementation flaws in bot prevention systems.
My Journey Through Building an Advanced Bot Detection Product
Explore the evolution of bot detection and management, focusing on fraudulent activities, detection techniques, and best practices for protecting e-commerce and finance websites.
Exploiting Unknown Browsers and Objects
Discover hidden browser vulnerabilities with the Hackability Inspector, a new offensive toolkit for security researchers to explore and exploit unknown entities in embedded browsers.
FIESTA - An HTTPS Side-Channel Party
Explore HTTPS side-channel vulnerabilities and a new tool, FIESTA, for testing and exploiting these issues. Learn about a novel side-channel affecting major tech companies and its implications for online security.
A Tour of API Underprotection
Explore API security threats, protection techniques, and advanced strategies. Learn about OAuth2, static API keys, mobile security, certificate pinning, and emerging technologies to strengthen your API security posture.
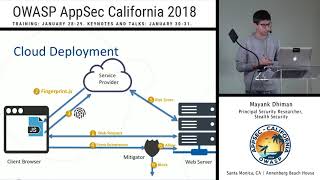
Breaking Fraud and Bot Detection Solutions
Demystifying browser fingerprinting and user behavior tracking in fraud detection, exploring vulnerabilities, and demonstrating proof-of-concept attacks against these defense mechanisms.
Common REST API Security Pitfalls
Explore common REST API security pitfalls, their root causes, and best practices for protection. Learn to assess and improve API security for robust, future-proof applications.
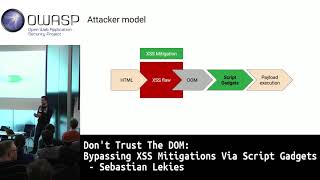
Don't Trust the DOM - Bypassing XSS Mitigations via Script Gadgets
Explores novel XSS attack technique using script gadgets to bypass mitigations, demonstrating vulnerabilities in modern JavaScript libraries and advocating for preventive security measures.
Core Rule Set for the Masses
Insights on fine-tuning ModSecurity Core Rule Set for large-scale deployments, reducing false positives, and optimizing web application firewall performance.
An Overview of API Underprotection
Explores API security challenges, threats, and emerging technologies. Covers OAuth2, API keys, mobile app security, TLS pinning, and advanced techniques like app hardening and software attestation.