WAFs FTW! A Modern DevOps Approach to Security Testing Your WAF
Explore modern DevOps approach to security testing Web Application Firewalls (WAFs) using Framework for Testing WAFs (FTW). Learn objective WAF evaluation, rapid prototyping, and continuous testing strategies.
Client-Side Protection Against DOM-Based XSS Done Right
Comprehensive overview of client-side protection against DOM-based XSS attacks, covering vulnerabilities, prevention techniques, and practical solutions for web security professionals.
Pentesting Swift Application with OWASP iGoat
Learn iOS Swift app pentesting using OWASP iGoat, covering security loopholes, defense strategies, and real-world case studies. Gain skills for product security engineers and bug bounty hunters.
CSP Pitfalls and Gotchas
Explore common pitfalls and gotchas in Content Security Policy implementation, focusing on whitelist issues, SameOrigin policy, and unsafe inline practices. Learn strategies for building a robust security framework.
Anatomy of a WebShell
Explore WebShell malware: types, design, usage, and detection methods. Learn to identify and protect against this stealthy, powerful attacker tool used for long-term network compromise.
.NET Access Control Service
Explore .NET Access Control Service for token-based authentication, federation, and secure resource access in Windows Azure environments.
Ads Networks Are Following You, Follow Them Back
Explore how ad networks track users and learn techniques to monitor and analyze their behavior, including tools like ET Toolkit and HTTP Bloom for enhanced web privacy.
Comparing WAF and RASP - Why?
Explore the differences and complementary roles of WAF and RASP in application security, understanding their strengths and limitations for comprehensive protection.
API Security - Is it the New Application Attack Surface and How to Secure at Enterprise Scale
Explore API security challenges, threats, and enterprise-scale solutions. Learn about modern attack surfaces, recent breaches, and effective strategies for protecting sensitive data in API-driven architectures.
Your Frontier Defense - Understanding Web Application Firewalls
Explore WAF options, features, and challenges across cloud providers and self-managed solutions for enhanced web application security and defense-in-depth strategies.
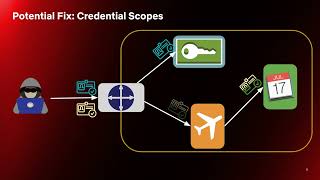
Adventures in Authentication and Authorization
Explore Netflix's journey in implementing authentication and authorization for microservices, discussing technology choices, challenges, and innovative solutions for a robust zero-trust ecosystem.
User Agent 2.0 - What Can the Browser Do for the User? - Ben Livshits - USENIX Enigma Conference - 2019
Explores browser evolution as a user agent, advocating for smarter security mechanisms and informed decision-making to enhance user privacy and content monetization on the web.
The URLephant in the Room - Emily Stark, Google - USENIX Enigma Conference - 2019
Exploring the challenges of URLs as security indicators, discussing user behavior, phishing attacks, and potential solutions for improving web security and user trust.
The Art of War of Browser Fingerprinting - Florencia Rao & Leandro Cuozzo - Ekoparty 2021: BlueSpace
Explora el fingerprinting del navegador: su uso, efectividad y aplicación en sistemas de autenticación para mejorar el reconocimiento de usuarios legítimos en organizaciones.
Ekoparty #UniTalks - Víctor Orozco: Seguridad de Aplicaciones Java/JakartaEE con OWASP Top 10
Ejemplos prácticos de vulnerabilidades OWASP Top 10 en Java/JakartaEE y cómo implementar controles de seguridad robustos en backends y microservicios usando APIs estándar como Jakarta EE security y MicroProfile JWT.
Mobile Hacking - Gustavo "Puky" Sorondo: Mobile Hacking Tips - Ekoparty Security Conference - 2020
Consejos y trucos para testear la seguridad de aplicaciones móviles, incluyendo tráfico remoto, certificados SSL, apps híbridas y un caso práctico de hackeo a Starbucks.
The Forbidden Image - Security Impact of SVG on the WWW - Mario Heiderich - Hack in Paris
Explores security risks of SVG images on the web, covering potential exploits, scripting vulnerabilities, and mitigation strategies for developers and security professionals.
Inside "MOAR TLS" - How We Think about Encouraging External - Emily Schechter - USENIX Enigma Conference - 2017
Exploring Google's "MOAR TLS" project to promote HTTPS adoption, addressing challenges, sharing strategies, and discussing the future of web security.
Several Horror Stories About the Encrypted Web - Peter Eckersley and Yan Zhu - USENIX Enigma Conference - 2016
Explore challenges in web encryption through real-world horror stories from Let's Encrypt and HTTPS Everywhere projects, offering insights into staying secure in a complex digital landscape.
Trust Beyond the First Hop–What Really Happens to Data Sent to HTTPS Websites - USENIX Enigma Conference - 2016
Explore the complex journey of web data beyond HTTPS, examining modern web infrastructure, security indicators, and potential approaches to extend trust beyond initial encryption.
Interact Differently - Get More from Your Tools Through Exposed APIs
Explore how to leverage exposed APIs and plugin interfaces in software tools to enhance functionality, streamline workflows, and create custom solutions for improved efficiency and effectiveness.