Securing the Gateway and Mitigating Risks in LLM API Integration
Explore strategies for safeguarding LLM API integrations, addressing security vulnerabilities, and implementing robust risk mitigation measures in AI-powered applications.
OWASP Coraza Web Application Firewalls Revisited
Explore OWASP Coraza's advanced features for securing web applications, including its architecture, rule language, and integration capabilities with popular web servers and frameworks.
Navigating the Landscape of Client-Side Request Hijacking on the Web
Explore client-side request hijacking vulnerabilities, their impact on web security, and effective mitigation strategies to protect against these emerging threats.
DOM Jungle - Can We Trust the UI?
Explore UI vulnerabilities and DOM-based attacks in web applications, learning techniques to identify and mitigate security risks in the browser environment.
API Security By Design
Explore API security best practices and design principles to build robust, secure systems with expert insights from Jose Haro Peralta.
Back to the Roots - Finding the Origin of CSP Security Bugs
Explore the root causes of Content Security Policy bugs in web browsers, their lifecycle, and insights for both attackers and defenders using automated analysis tools.

How to Setup Fingerprint Authentication in JavaScript
Learn to implement fingerprint and biometric authentication in JavaScript using WebAuthn APIs. Covers client and server-side setup for secure, third-party-free user registration and login.
How Hacking Works - Web Edition
Explore web exploitation techniques and tools to enhance software security. Learn through gamified environments to build skills for safer development practices.
Preparing for the API Apocalypse - Exposing Shadow and Zombie APIs
Uncover hidden vulnerabilities in Shadow and Zombie APIs. Learn techniques to identify, understand, and mitigate risks using popular frameworks and open-source tools for enhanced API security.
BOLABuster: Harnessing LLMs for Automating BOLA Detection
Harnessing LLMs to automate BOLA detection in APIs and web applications, reducing requests by 99% while uncovering critical vulnerabilities and submitting multiple CVEs.
Hacking Arcade Cashless Systems: Vulnerabilities and Exploits
Explore vulnerabilities in global arcade cashless systems, covering API security, access control, and NFC. Learn how to exploit weaknesses for potential free play in amusement parks worldwide.
Attacking Primary Refresh Tokens Using MacOS Implementation - TROOPERS24
Explore techniques for attacking Primary Refresh Tokens through MacOS implementation, presented by security experts at TROOPERS24 conference in Heidelberg.
Exploiting Token-Based Authentication: Attacking and Defending Identities in the 2020s
Explore token-based authentication vulnerabilities and defense strategies for modern identity systems in this insightful cybersecurity talk by Dr Nestori Syynimaa at TROOPERS24.
Seven Things About API Security - NDC Oslo 2024
Explore API security best practices, OWASP top vulnerabilities, live demo, and real-world case studies to enhance your API protection strategies and prevent potential breaches.
The Final Frontier - Security APIs in Modern Browsers
Explore modern browser security APIs and mechanisms that protect against common web attacks, enhance authentication, and restrict browser behavior, with code demonstrations and future insights.
New Methods of Recon - Enhancing Reconnaissance Techniques
Refine and expand your reconnaissance toolkit with top hacker OrwaGodfather's precise tactics, enhancing your bug hunting capabilities.
Guarding LLM and NLP APIs: A Trailblazing Odyssey for Enhanced Security - Podcast #190
Explore LLM and NLP API security challenges, threat modeling, and defense strategies. Gain insights on OWASP Top 10 for LLM Applications and the AI Village's 'Hack the Future' event at Defcon31.
Safeguarding Platforms: Detecting Abusive Behavior Patterns
Discover strategies to combat digital threats and protect platforms from automated abuse. Learn innovative anti-abuse techniques used by tech giants to safeguard valuable data and enhance cybersecurity measures.
Blasting Past WebP - Exploring Image Format Vulnerabilities
Explore advanced techniques for bypassing WebP image format security measures, uncovering vulnerabilities and potential exploits in web applications.
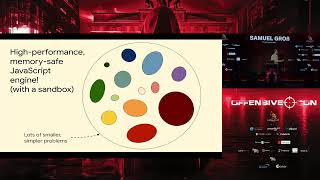
The V8 Heap Sandbox - Understanding JavaScript Engine Security
Explore V8 engine's heap sandbox implementation, its security implications, and potential vulnerabilities in Chrome's JavaScript engine.
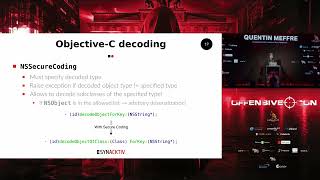
Escaping the Safari Sandbox: A Tour of Webkit IPC
Explore Webkit IPC vulnerabilities and techniques for escaping the Safari sandbox, gaining insights into browser security and exploitation.