Stay Ahead of API Security Threats with Machine Learning Detection
Explore ML-powered API security controls to detect abuse, misconfigurations, and business logic attacks without adding overhead. Learn to protect sensitive data and critical business information.
Zero Trust Security for APIs
Implement Zero Trust Security for APIs. Learn the model, architecture, and practical steps to protect your API ecosystem from frequent attacks and abuses.
7 Must-Know Steps to Making Modern Web Apps Ultra-Secure
Learn 7 essential steps to enhance web app security. Master prevention of vulnerabilities, implement secure authorization, add security layers, logging, and testing for robust protection.
API Security Best Practices - Preventing Vulnerabilities and Hacks
Learn API security best practices, including BOLA vulnerability prevention, testing techniques, and strategies to protect against hacking through a demo-oriented session.
Exploring Card Games in Threat Modeling - Enhancing Security Posture
Explore innovative card games for threat modeling, including Elevation of Privileges, OWASP Cornucopia, and OWASP Cumulus. Learn how these engaging tools can enhance your organization's security posture through interactive gameplay.
OWASP Top 10 Security Risks for Large Language Models
Explore OWASP Top 10 LLM security risks, learn mitigation strategies, and understand the impact of Generative AI on cybersecurity in various industries.
Public Key Caching Strategies for Token Signature Validation - DevSecCon
Explore public key caching strategies for token signature validation in OAuth2 and OpenID Connect. Compare performance and security trade-offs of different approaches for relying parties.
Securing Applications in SDLC and Cloud-Native Web and API Protection - Sessions 1 and 2
Learn secure coding practices, identify vulnerabilities, and integrate security into SDLC. Explore cloud-native WAAP for effective web app and API protection using machine learning.

Secure Practices with .NET Services
Implement robust security measures for .NET services, including encryption, authentication, and best coding practices to safeguard applications and data against cyber threats.
How Hacking Works - Web Edition - NDC Oslo 2024
Explore web exploitation techniques and tools to enhance software security through gamified environments. Learn to think like a hacker for safer development.
The Digital Trust Journey: From Key Generation to Signed Certificate
Explore the creation process of digital certificates, from key generation to CA signing. Understand the critical steps ensuring trust and security in online interactions.
OWASP LLM Top 10 - Understanding Critical Security Risks for Large Language Models
Explore OWASP LLM Top 10: Gain insights into critical security risks, learn practical steps to fortify applications, and stay ahead in cybersecurity with expert R Nagarjun.
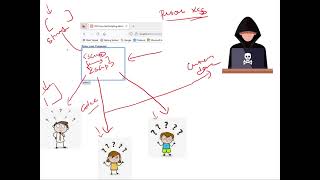
Persistent XSS (Cross-Site Scripting) Attack: What It Is and How to Prevent It
Explore persistent XSS attacks, witness a live demo, and learn effective prevention strategies to enhance web application security.
Nikto Web Vulnerability Scanner - Web Penetration Testing
Learn to identify web vulnerabilities using Nikto, an open-source scanner. Explore its features and enhance your web application security skills.
Zero Trust APIs with Python
Explore Zero Trust Security for APIs using Python. Learn to identify and address vulnerabilities, implement robust data validation, and use tools for automated security testing.
What's Not So New in the New OWASP Top 10 - Devoxx Poland 2022
Explore OWASP Top 10 updates, focusing on insecure design. Learn defense-in-depth strategies, secure design principles, and threat modeling methodologies like STRIDE for improved web application security.
Go Passwordless with WebAuthn in Ruby
Explore WebAuthn for passwordless authentication in Ruby, enhancing security and user experience with biometrics and public-key cryptography.
When Not to Use a Web Application Firewall and Its Alternatives - Lecture
Explore when to avoid Web Application Firewalls (WAFs) and learn their limitations. Understand WAF architecture, common web threats, and alternative security approaches for effective application protection.
Capture the Flag 101 Workshop
Dive into Capture the Flag challenges with hands-on practice, learning key concepts and problem-solving techniques for beginner and intermediate levels in cybersecurity.
Beyond the Basics: Securing JavaScript Applications
Explore advanced JavaScript application security techniques, from understanding cyber attack chains to implementing network isolation and restrictive IAM permissions.
Iterative Threat Modelling - Security in Agile Development
Learn iterative threat modeling for agile development. Explore misconceptions, methodologies, and practical examples using OWASP Juice Shop. Discover effective ways to identify, prioritize, and mitigate security risks.