Graph-Oriented Approach for SSTI Payload Optimization - Jinja2 Case Study
Explore a graph-oriented approach for optimizing Server-Side Template Injection payloads, focusing on Jinja2 vulnerabilities and enhancing web application security.
The Past, Present, and Future of Cross-Site and Cross-Origin Request Forgery
Explore the evolution of Cross-Site Request Forgery attacks, their impact on applications, and effective defense strategies. Learn about vulnerabilities in API-based systems and best practices to prevent CSRF.

OWASP Juice Shop - An Open Source Software and Security Fairytale
Explore the evolution of OWASP Juice Shop, a pioneering hacking training platform, from its inception as a pet project to becoming an OWASP Flagship project, with insights into its future developments.
Unlocking the Secrets of TLS - Understanding the TLS Handshake Process
Explore the intricacies of TLS handshake, its evolution, and how secure connections are established on the Internet. Gain insights into past mistakes and lessons learned in this process.
Modern WAF Bypass Techniques on Large Attack Surfaces
Explore advanced WAF bypass techniques for large attack surfaces with insights from top security researcher Shubham Shah, focusing on complex vulnerabilities and security automation.
Cross Site Scripting (XSS) in 2023 - The Mitigated Unmitigated Vulnerability
Explore the current state of Cross-Site Scripting (XSS) vulnerabilities, their impact, and mitigation strategies in modern web security landscape.
Security Is Key - The Vulnerabilities of API Security
Explore API security vulnerabilities and learn essential strategies to protect your systems from potential threats in this informative talk by Joe Wrieden.
Mastering Web Security - Myths, Strategies and Best Practices
Debunking web security myths and exploring effective defense strategies. Experts share practical tips, valuable resources, and emphasize organizational commitment for robust application security.
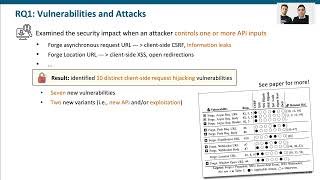
The Great Request Robbery
Explore web security vulnerabilities and attack techniques with a focus on request forgery and injection flaws in modern applications.
Fundamentals of API Security with Python
Dive into API security for Python apps. Learn authentication, authorization, OWASP top 10 vulnerabilities, OAuth, OIDC, JWTs, and automated security testing. Practical examples using Flask and FastAPI.

SQL Injection Explained - With Free Labs
Comprehensive guide to SQL injection vulnerabilities, featuring expert insights and hands-on practice labs for enhancing web security skills and bug bounty hunting techniques.

What is JWT and Why - Understanding JSON Web Tokens
Explore JSON Web Token (JWT): its purpose, structure, and benefits for secure information transmission between parties in web development.
I Can't Scan This Website - Cybersecurity Challenges with Cloaking Firewalls
Explore website scanning challenges and cybersecurity techniques with John Hammond. Learn about protective measures like Cloaking Firewall and gain insights into infrastructure security.
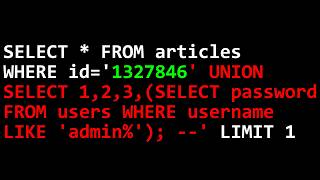
Interactive SQL Injection
Hands-on practice with SQL injection techniques in a safe environment. Learn to identify and exploit vulnerabilities, enhancing your cybersecurity skills and understanding of database security.
The Mark of the Web - Understanding Internet Security Zones
Explore the Mark of the Web security feature, its impact on file downloads, and how it affects system protection and user experience in Windows operating systems.
Towards Better Semantics Exploration for Browser Fuzzing
Explore innovative browser fuzzing techniques using production-context sensitive grammars for enhanced semantic coverage and bug detection in Chrome, Safari, and Firefox.
DevSecOps Transformation at Speed and Scale Using Tekton
Standardize CI/CD security automation, centralize platform operations, and prevent software vulnerabilities using Tekton as an open-source orchestrator with integrated scanning tools and continuous compliance.
Subdomain Hijacking - Why DevOps is Making Us More Vulnerable
Explore subdomain hijacking vulnerabilities in DevOps practices and learn mitigation strategies to enhance your organization's security posture.
API Security: Code-to-Cloud Context for Complete Protection
Comprehensive approach to API security, covering code-level inventorying and runtime protection. Learn to mitigate issues faster and improve organizational API security posture efficiently.
Insecurity Protocols - An Overview of Modern Authentication
Explore modern authentication protocols like OpenID Connect, SAML, and WebAuthn. Learn their strengths, vulnerabilities, and real-world security implications in this comprehensive overview.
OWASP API Security Project
Explore OWASP's API Security Project, focusing on best practices, common vulnerabilities, and strategies to enhance API protection in modern applications.