Scanning at Scale with OWASP ZAP - Technical Challenges and Improvements
Explore techniques for scaling OWASP ZAP scans, including technical challenges, modifications, and improvements. Learn from Probely's experience as active ZAP contributors.
Using API Specifications to Attack APIs
Explore API security vulnerabilities, breaches, and scanning tools. Learn to leverage API specifications for both protection and potential exploitation in this comprehensive overview.
Defense-in-Depth Engineering Techniques for Secure Software Design
Explore techniques for building resilient software, identifying overlooked vulnerabilities, and designing for incident preparedness. Learn to architect secure systems and improve incident response capabilities.
Hacking an Online Casino - Bug Bounty Stories Episode 1
Discover how a bug bounty hunter successfully hacked a major online casino. Learn about the techniques used and gain insights into the world of ethical hacking and cybersecurity.
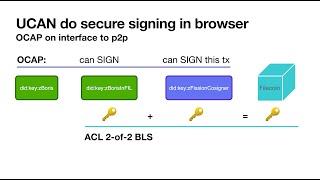
Secure Key Management in the Browser with UCAN - Fission Platform Overview
Explore secure key management in browsers using UCAN, WebCrypto API, and DIDs. Learn about Fission's platform and plans for Filecoin integration without browser extensions.
Towards Intelligent Application Security
Exploring the evolution of application security and proposing an automated approach integrating security into development and operations, aided by learning techniques and threat intelligence.
The Secret Life of Secrets - Designing Secure API Keys
Explore API key design strategies, security measures, and best practices for creating robust and secure API authentication systems.

Fake CAPTCHA Malware Analysis
Explore the deceptive tactics of malware disguised as CAPTCHA, uncovering its distribution methods and analyzing its impact on cybersecurity.
Web Developer Security: Best Practices and Beyond
Explore latest web security developments, technologies, and best practices for developers, including insights from recent workshops and W3C initiatives.

How to Implement Keycloak Authentication in React
Implement Keycloak authentication in React applications for enhanced security and access management in web-based projects.

Picking the Low-Hanging Fruit - Easy Pentest Wins
Learn to secure web services by addressing common vulnerabilities and easy-to-fix issues in penetration testing, freeing up resources for more complex challenges.

Safeguarding Web Applications Against Token Theft - Fortifying Security with DPoP
Explore DPoP, an innovative approach to secure token management in web applications, enhancing OAuth 2.0 framework and addressing challenges in authentication and authorization.
Escaping Modern Web-Based App Sandboxes - Site Isolation Vulnerabilities
Explore Chrome's site isolation vulnerabilities in web-based apps, revealing how attackers can bypass security measures to execute malicious actions and compromise user data.
Dawn of the Dead: The Tale of the Resurrected Domains
Explore the intriguing world of resurrected domains and their potential security implications in this insightful talk by Pedro Fortuna.
Exploiting Client-Side Path Traversal - CSRF Is Dead, Long Live CSRF
Uncover advanced techniques for exploiting client-side path traversal vulnerabilities, exploring the evolution of CSRF attacks and their modern implications for web security.
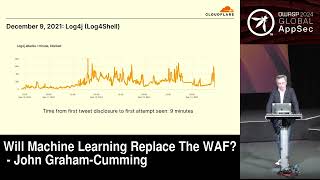
Will Machine Learning Replace the WAF?
Explore the potential of machine learning to revolutionize web application firewalls, examining its capabilities, limitations, and impact on cybersecurity.
The Power of JWT and Cryptography - Fundamentals and Digital Signatures
Explore fundamental cryptography principles, JWT, and digital signatures for software security. Learn how to protect infrastructure and data from attacks.
A New Architecture for Data Security to Free Incident Responders from False Positives
Explore a new data security architecture that minimizes false positives, enhancing incident response efficiency and improving detection of real security threats.
Identity and Security Meetup - November 2023
Explore OAuth 2.0 security in frontends and gain insights from identity experts. Level up your skills with presentations on web security and identity management from industry professionals.
Scaling Content Security Policy: Enterprise Compliance and Third-Party Resource Management
Learn to implement Content Security Policy and monitor web resources at scale, addressing supply chain attacks and PCI requirements for enhanced frontend security in enterprise applications.
Attacking Developer Environments Through Drive-by Localhost Attacks
Explore drive-by localhost attacks on developer environments, uncovering vulnerabilities and defense strategies in this cybersecurity presentation from DefCamp 2023.