OWASP API Security: Sufficient Logging and Monitoring for API Protection
Explore real-world examples and best practices for implementing sufficient API logging and monitoring to enhance security, observability, and incident response capabilities.
Ending Injection Vulnerabilities
Learn how programming languages can prevent injection vulnerabilities by distinguishing trusted developer strings from potentially attacker-controlled input, ensuring safer handling of user values in sensitive contexts.
Securing Modern Applications and APIs Against Attacks
Explore effective API security strategies for modern applications, focusing on deep application knowledge and user behavior to protect against evolving threats in cloud-native architectures.
OWASP ZAP and DeepFactor - Continuous AppSec Observability for DevSecOps
Explore how DeepFactor's observability enhances OWASP ZAP for comprehensive DevSecOps, detecting security risks in modern cloud-native applications through advanced event monitoring.
Are You Safe from OWASP #11? - Creating a Successful API Security Program
Explore API security beyond Top 10 lists, focusing on building a comprehensive program at scale. Learn key strategies for successful API protection and management.
Cybersecurity Trends and Challenges - 2022 Global AppSec Keynote
Explore cutting-edge application security insights and trends with Simon Bennetts' keynote address at the 2022 Global AppSec conference in San Francisco.
Passwordless Future: Using WebAuthn and Passkeys in Practice
Explore WebAuthn and passkeys for passwordless authentication, covering architecture, ceremonies, and usability improvements for a more secure online future.

Hacking Web Applications
Comprehensive guide to web application vulnerabilities, covering OWASP Top 10, hands-on walkthroughs, and defense strategies. Learn to identify, exploit, and mitigate common security risks in web applications.

How to Hack WordPress - Exploiting Plugins - Part 2
Learn to exploit WordPress plugins through lab setup, enumeration techniques, and remote code execution in this hands-on cybersecurity tutorial.
Advanced API Security with Kong - Developer Day 2021 Labs
Learn to secure APIs using Kong Gateway and Okta. Configure OIDC authentication for Kong Developer Portal and Manager, and explore various security plugins and features.
Integrating Identity into APIs with Okta and Kong - Developer Day 2021
Discover powerful authentication and authorization scenarios using Kong and Okta. Learn to implement sophisticated API access and management flows with OIDC and OAuth, including CI/CD pipeline integration.
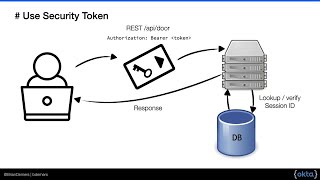
Security Tokens - Understanding JWTs, Macaroons, and PASETOs
Explore security tokens like JWTs, Macaroons, and PASETOs. Learn their benefits, usage, and potential vulnerabilities in mobile and web applications. Gain insights on choosing the right token for your project.
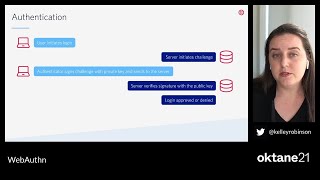
Everything You Want to Know About WebAuthn
Explore WebAuthn, a new authentication standard using everyday devices as phishing-resistant security keys. Learn its workings, applications, and potential for widespread adoption in consumer applications.
A Beginner's Guide to Building a Secure Website
Learn to build secure websites using OAuth and OpenID Connect. Covers authorization flows, client registration, PKCE, and includes live coding demonstrations for practical implementation.
An Introduction to PASETO - Understanding Platform Agnostic Security Tokens
Discover PASETO tokens, a simpler and more secure alternative to JWTs. Learn how they work, their advantages, and how to implement them in your applications for improved web authentication.
Step by Step Webapp Hacking Resources - Ethical Hacking
Comprehensive guide to web application hacking resources, including platforms, tools, and learning materials for aspiring ethical hackers and bug bounty hunters.

Web App Penetration Testing - CSRF (Cross Site Request Forgery)
Demonstración práctica de ataques CSRF en OWASP Juice Shop utilizando BurpSuite. Aprende a identificar y explotar vulnerabilidades de falsificación de peticiones entre sitios en aplicaciones web.
Sucuri Web Application Firewall Review
Comprehensive review of Sucuri's web application firewall, exploring its features, effectiveness, and benefits for website security and protection against online threats.

Nginx ModSecurity Tutorial - Nginx WAF
Learn to secure Nginx with ModSecurity, an open-source web application firewall. Explore real-time request inspection, protection against XSS and SQL injection attacks, and active monitoring for enhanced web server security.

Apache2 ModSecurity Tutorial - Apache2 WAF
Learn to secure Apache2 with ModSecurity, an open-source web application firewall. Explore real-time request inspection, prevention of common attacks, and active monitoring for enhanced web server protection.
How to Hack an API in 15 Minutes
Discover how hackers exploit Shadow APIs to extract large volumes of data quickly. Learn about this basic yet non-obvious security vulnerability and creative methods used by attackers.