Malware and Defense Techniques - OWASP AppSec Europe 2014
Explore cutting-edge malware detection, web security, and network defense techniques from industry experts at OWASP AppSec Europe 2014. Gain insights on cloud-based solutions, botnet detection, and advanced web application protection.
Introduction to the Newest Addition to the OWASP Top 10 - A9 Guidelines
Experts discuss the new OWASP A9 guideline on insecure open source libraries, offering insights on component usage, best practices, and real-world challenges in mitigating risks in agile development.
Application Security - Challenging Traditional Approaches and Controls
Challenging traditional application security approaches, this talk explores innovative strategies for developing and testing secure software, emphasizing the need for consistency and proactive security measures.
OWASP Hackademic - Teaching Application Security Through Practical Challenges
Practical environment for teaching application security through realistic scenarios with known vulnerabilities. Students discover and exploit vulnerabilities, gaining hands-on experience from an attacker's perspective.
Stop Chasing Vulnerabilities - Introducing Continuous Application Security
Explore continuous application security strategies using open-source tools for real-time monitoring and analytics, shifting focus from individual vulnerabilities to comprehensive portfolio-wide assurance.
Client-Side Exploitation Techniques Without Zero-Day Vulnerabilities
Explore practical client-side exploitation techniques without 0days, including browser extensions, HTML applications, and UI manipulation. Learn to automate attacks and tailor them for effective offensive security.
Blended Web and Database Attacks on Real-time, In-Memory Platforms
Explore blended web and database attacks on real-time, in-memory platforms, focusing on SAP HANA. Learn about novel exploit techniques, vulnerabilities, and security considerations for these high-performance systems.
Improved Phishing Detection Using Perceptual Hashing - AppSecUSA 2014
Explore advanced phishing detection using perceptual hashing algorithms, with insights on identifying malicious sites masquerading as popular platforms and a demonstration of new defensive tools.
11,000 Voices - Experts Shed Light on 4-Year Open Source and AppSec Survey
Experts discuss findings from a 4-year study on open source security practices, revealing surprising trends in policy enforcement, vulnerability tracking, and organizational preparedness for security threats like Heartbleed.
Building Your Application Security Data Hub - The Imperative for Structured Vulnerability Information
Learn how to create an integrated application security program by breaking down silos, enabling data flow between teams and tools, and implementing metrics to measure performance and improvement.

Making Content Security Policy Work For You
Learn about Content Security Policy (CSP), its importance in web application defense, and practical tips for implementation from Mozilla's application security expert.
Continuous Security Testing in DevOps Environments
Explore continuous security testing in DevOps, addressing challenges and presenting an open-source framework using Behavior Driven Development for effective communication and automation.
Reflections on Scoping Trust in Modern Web Environments
Reflections on trust in the modern web environment, examining gaps in current models and exploring ways to create a more trustworthy internet ecosystem without total self-reliance.
API Authentication's Poorly Implemented - Security Issues in Web APIs
Explore real-world API security issues, focusing on authentication and authorization problems across various platforms. Learn from examples ranging from online payment systems to embedded device infrastructures.
Building a Web Malware Analyzer Using Machine Learning - Catch Me If You Can
Learn to build a web malware analyzer using machine learning. Explore infection methods, injected content, and scalable detection systems. Includes live demo and insights on web malware trends and prevention mechanisms.
Top 10 Web Hacking Techniques of 2013 - OWASP AppSecUSA 2014
Explore the top 10 innovative web hacking techniques of 2013, including Mutation XSS, BREACH, and HTML5 attacks. Learn about cutting-edge security vulnerabilities and their implications for web applications.
Static Analysis for Dynamic Assessments - OWASP AppSecUSA 2014
Explore techniques for using static analysis tools in dynamic web vulnerability assessments without source code, enhancing detection of security weaknesses in complex applications.
OWASP Top 10 Mobile Risks: 2014 Reboot
Explore the updated 2014 OWASP Top 10 Mobile Risks, comparing changes since 2011, understanding new threats, and learning recommended fixes for iOS, Android, and Windows Phone platforms.
New Frameworks, Old Problems: Web Security Challenges in Modern Development
Exploring security challenges in modern web frameworks like Play! and Node.js, comparing solutions from established frameworks, and offering practical code examples to address common vulnerabilities.

Content Security Policy (CSP) - Understanding and Implementing Web Protection
Learn about Content Security Policy (CSP), a powerful browser security feature that mitigates cross-site scripting attacks. Discover its benefits, implementation strategies, and future impact on web security.
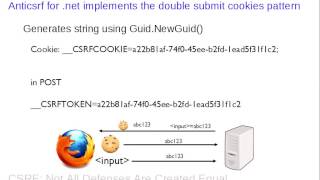
CSRF Defense Strategies - Not All Are Created Equal
Explore CSRF vulnerabilities, defense mechanisms, and their implementations. Learn about synchronizer token patterns, double submit cookies, and challenge-response systems for effective protection against CSRF attacks.