Implementing a User-Centric Datastore with Privacy-Aware Access Control for Cloud-Based Data Platforms
Explore user-centric data storage with privacy-aware access control for cloud platforms. Learn about implementation, components, and challenges in this informative talk on secure data management.
Rise of the Machines - How Automated Processes Overtook the Web
Explore how automated processes have dominated web interactions, their impact on security, and strategies to protect against machine-driven threats in modern web environments.
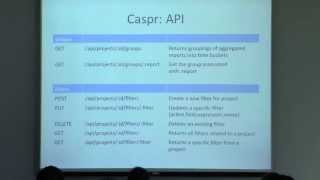
Content Security Policy Reporting and Aggregation with Caspr - OWASP AppSec California 2015
Explore Content-Security-Policy (CSP) violation reporting with Caspr, a tool for collecting and analyzing reports. Learn about CSP background, Caspr usage, and related tools for enhancing web application security.
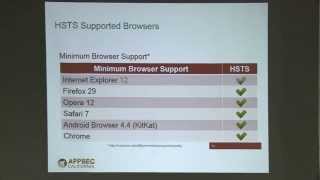
Proactively Defending Your Business Against Security Protocol Attacks - OWASP AppSec California 2015
Explore strategies to proactively defend against security protocol attacks and implementation flaws in HTTPS/SSL/TLS. Learn about recent vulnerabilities, mitigations, and best practices for secure communications.
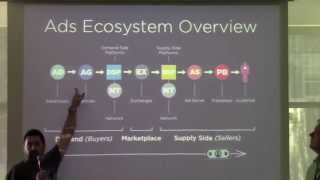
Modern Malvertising and Malware Web-Based Exploit Campaigns
Explore modern malvertising and web-based exploit campaigns, including top malware types, real-world attack breakdowns, and emerging threats in this technical presentation on cybersecurity.
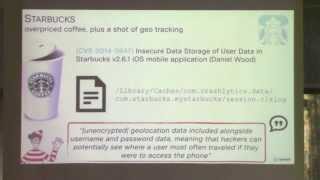
When Geo Goes Wrong - A Case Study of Geolocation Vulnerabilities in Mobile Apps
Exploring geolocation vulnerabilities in mobile apps, focusing on a dating app case study. Discusses common bugs, attack methods, and best practices for secure location-aware app development.
Analyzing and Detecting Flash-Based Malware
Explore techniques for analyzing and detecting Flash-based malware, enhancing your cybersecurity skills and understanding of this prevalent threat vector.
Framework Security: Hugging Developers Through Self-Defending Systems - AppSecEU 2016
Explore framework security strategies, self-defending frameworks, and developer-friendly approaches to enhance application security without code changes or performance impact.
Hardening the Web Platform
Explore web platform security with Mike West's keynote on hardening techniques, challenges, and future directions for a more robust online environment.
Making CSP Great Again - Enhancing Content Security Policy
Explore advanced Content Security Policy techniques to enhance web application security and mitigate XSS vulnerabilities effectively.
The Top 10 Web Hacks of 2014 - AppSec EU 2015
Explore the most significant web security vulnerabilities of 2014, presented by industry experts. Gain insights into attack vectors and learn essential defense strategies.
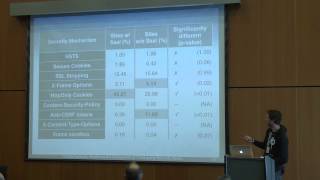
Issues and Limitations of Third Party Security Seals
Explore limitations of third-party security seals in web applications, uncovering potential vulnerabilities and discussing implications for online security practices.
Copy Pest - A Case Study on the Clipboard, Blind Trust, and Invisible Cross-Application XSS
Explore clipboard vulnerabilities and cross-application XSS in this case study on invisible security threats and blind trust in web applications.
Naxsi: A Web Application Firewall for NGINX
Explore Naxsi, an open-source web application firewall for NGINX, and learn about its features, implementation, and benefits for enhancing web application security.
Making SSL Warnings Work - Improving Security and User Experience
Explore strategies to improve SSL warnings in Chrome, focusing on reducing false positives and enhancing user understanding of security threats through clear design and communication.
Monitoring Web Sites for Malware Injection with Web Detector
Explore WebDetector, a tool for monitoring websites and detecting malware injections. Learn about its components, heuristics, and effectiveness in identifying harmful elements on web pages.

Lessons from Trusting JavaScript Cryptography - Biting into the Forbidden Fruit
Exploring real-world JavaScript cryptography implementations, debunking myths, and providing an updated perspective on JS crypto security through vulnerability analysis and practical examples.
Getting New Actionable Insights by Analyzing Web Application Firewall Triggers
Explore advanced techniques for analyzing WAF triggers to generate actionable defenses, improve security controls, and gain insights into attacker techniques using real-world case studies.
Security Implications of Cross-Origin Resource Sharing - HTML5 and CORS Analysis
Explore security implications of Cross-Origin Resource Sharing in HTML5, including its impact on same-origin policy, potential vulnerabilities, and mitigation strategies for web application developers.
Hybrid Analysis Mapping - Making Security and Development Tools Play Nice Together
Explore techniques for integrating security testing and development tools, improving collaboration between testers and developers for more effective application security and code quality.
Getting a Handle on Mobile Security
Comprehensive overview of mobile security challenges and best practices, covering encryption, data protection, and platform-specific concerns for developers building secure mobile applications.