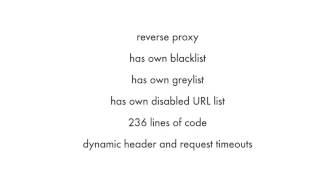
Surviving an Application DoS - Strategies and Open Source Defense Framework
Explore strategies to defend against Application-Level DoS attacks using a new open-source Node.js framework. Learn to identify threats, analyze traffic patterns, and implement active defense measures.
Libinjection: From SQLi to XSS Detection - New Algorithm Introduction
Explore advanced techniques for detecting SQLi and XSS attacks using libinjection, a fast and accurate algorithm. Learn about its implementation, benefits, and future developments in web security.
The Perilous Future of Browser Security
Explore browser security challenges, tradeoffs, and solutions. Learn about critical vulnerabilities, secure browser design, and balancing security with user experience in the face of evolving threats.
Pushing Content Security Policy to Production - Case Study of Real-World Implementation
Practical insights on implementing Content Security Policy in a live web application, covering challenges, browser nuances, third-party integrations, and real-world violation reports.
Fixing XSS with Content Security Policy
Learn how Content Security Policy (CSP) can prevent XSS attacks, understand its versions, browser support, and implementation strategies for web applications. Gain insights on balancing CSP with traditional security measures.
How Web Authentication Works: TLS, Password Hashing, OpenID Connect, OAuth 2, and JSON Web Tokens
Explore the inner workings of web authentication, covering TLS, password hashing, OpenID Connect, OAuth 2, and JSON Web Tokens in this comprehensive overview.
Kong API Gateway Integration with Okta OIDC Authentication
Integrate Kong API gateway with Okta OIDC for seamless authentication, eliminating the need for your application to manage OIDC flows directly.
JWTs for CSRF and Microservices - Secure Implementation Examples
Learn to implement JWT-based CSRF protection and establish trust between microservices using JWTs, with practical code examples and insights into secure microservice architecture.
WebAuthn (FIDO2) and Project Fugu - Browser Capabilities and Authentication
Explore cutting-edge web technologies like WebAuthn for secure logins and Project Fugu for advanced browser capabilities, including machine learning and hardware integration.
How to Build and Deploy a Custom JWT Auth System - Ktor, MongoDB, Android
Comprehensive guide to building a JWT authentication system using Ktor, MongoDB, and Android, covering backend development, app integration, and server deployment on Ubuntu.
Shift-Left DevOps for APIs with Okta and JFrog - Developer Day 2021
Strengthen your shift-left DevSecOps strategy by automating REST API security validation using Okta and JFrog. Learn to verify authentication and authorization policies before production release.
Privacy-preserving Approaches to Transparency Logs
Explore append-only transparency logs, their applications in infrastructure, and privacy-preserving techniques to balance immutability with user rights and data protection.
High-Level API Security with Keycloak - FAPI Implementation and Conformance
Explore high-level API security using Keycloak, focusing on OAuth 2.0, FAPI, and advanced features for robust authorization in digital transformation contexts.
Adding Authentication to Apps with Okta - Learn With Jason
Implement user authentication in Gatsby apps using Okta. Learn to set up secure user accounts, integrate sign-in widgets, and manage JSON Web Tokens for enhanced app functionality.

Opening Doors with JSON Web Tokens - Securing IoT Access
Explore secure IoT door access using JSON Web Tokens, NFC, and mobile apps. Learn innovative techniques for remote authorization without direct internet connection, balancing convenience and safety.

Authenticating Single Page Apps Using JSON Web Tokens
Learn to implement secure authentication in single page apps using OpenID Connect and JSON Web Tokens, enhancing user experience and application security.

The Future of Authentication - WebAuthn with PHP
Explore WebAuthn, a passwordless authentication standard, and learn how to implement it using PHP and JavaScript for enhanced security and user experience.
Practical Security in Web Applications
Explore effective methods to identify and avoid common security pitfalls in web applications. Learn to build secure enterprise web presence and protect against vulnerabilities.

The First 200 Milliseconds of HTTPS
Explore the intricate process of HTTPS connections, from certificates to cipher suites. Gain insights into the hidden mechanisms that ensure secure web browsing and understand potential vulnerabilities.
Hacking the OWASP Juice Shop
Explore web application security through hands-on hacking of a deliberately insecure e-commerce site, learning about OWASP Top 10 vulnerabilities and ethical hacking techniques.
Web Application Firewall - Functionality and Bypass Techniques
Explore web application firewalls, their functionality, and techniques to bypass them in this insightful presentation by security expert Aatif Khan.