OWASP Distinguished Lifetime Member Award - Jeff Williams' Contributions
Explore Jeff Williams' contributions to OWASP, including foundational projects, non-profit creation, and innovative security concepts, in this insightful 20th anniversary recognition.
Virtual AppSec Days Lightning Conference
Explore cutting-edge application security topics with industry experts in this fast-paced, informative conference session from OWASP Foundation.

WebAuthn - Balancing Strong Authentication, Privacy, and Convenience
Explore the balance between robust authentication, user privacy, and ease of use in WebAuthn implementation for enhanced online security.
Understanding the API Attack Vector - How Attackers Exploit Application Communications
Explore attacker techniques for targeting API-driven applications, including code manipulation, mobile vulnerabilities, and advanced attacks. Learn strategies to secure apps in cloud-native environments.
OWASP Top 10 - The Making of the OWASP Top 10 and Beyond
Explore the creation process and principles behind the OWASP Top 10, a crucial resource for web application security, including data analysis, likelihood management, and scoring methodologies.
OWASP CSRFGuard: Understanding and Preventing Cross-Site Request Forgery
Learn to prevent Cross-Site Request Forgery attacks with OWASP CSRFGuard. Explore real-world examples, detection techniques, and implementation strategies for robust web application security.
Modern XSS Defense Strategies - Frameworks, CSP, and Sanitization
Explore modern XSS defense strategies, including JavaScript frameworks, CSP deployment, HTML sanitization, and design considerations for building secure web applications against evolving threats.
OWASP Serverless Top 10 - Security Risks and Protections
Explore serverless security risks, challenges, and protective measures. Learn about OWASP Serverless Top 10 and DVSA tool for understanding serverless security implications and processes.
Trusted Types: End-to-End Injection Safety at Scale
Learn about Google's approach to achieving high-level XSS safety through integrated tools and developer-friendly practices, with insights on implementing similar security in open-source stacks.
Pwning WhatsApp - The Dark Side of Web-based Messaging Apps
Explore vulnerabilities in web-based messaging apps, focusing on WhatsApp. Learn about potential security risks and exploitation techniques in popular communication platforms.
OWASP Top 10 Maturity Categories for Security Champions
Learn to become an effective Security Champion using OWASP's Top 10 Maturity Categories. Explore key responsibilities, maturity models, and strategies for improving organizational security posture.
Don't Worry, Be API - Addressing AppSec's Modern Challenge
Explore modern API security challenges and solutions, including OWASP API Security Top 10, authentication issues, and authorization vulnerabilities in this comprehensive overview.
Good Bot, Bad Bot: Characterizing Automated Browsing Activity
Explore Aristeus, a system for deploying honeysites to study malicious bot behavior. Learn about bot traffic patterns, attack strategies, and the importance of understanding automated browsing activity for web security.
Everything You Always Wanted to Know About Fingerprinting Browser Extensions
Explore browser extension fingerprinting techniques, their implications for user privacy, and current browser defenses. Learn about DOM modifications, stylesheet hijacking, and web-accessible resources.
Hack Your APIs in 15 Minutes or Less - Exploiting Shadow APIs and Data Vulnerabilities
Learn to identify and exploit API vulnerabilities, understand hacker techniques, and explore creative methods for data theft in this eye-opening talk on modern cybersecurity challenges.
Worrisome Web Vulnerability Trends in the Race to Innovation
Explore concerning web vulnerability trends amid rapid innovation, examining their impact on security and discussing strategies for mitigation and protection.
A Risk-Based Approach to API Security
Explore a risk-based approach to API security, focusing on threat modeling, vulnerability assessment, and mitigation strategies to enhance your organization's API protection.
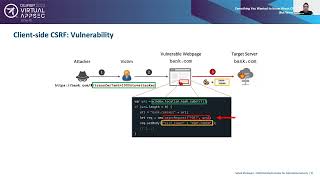
Everything You Wanted to Know About Client-Side CSRF But Were Afraid to Ask
Explore client-side CSRF vulnerabilities, detection challenges, and advanced analysis techniques using hybrid property graphs for improved web application security.
Preventing Subdomain Takeover with OWASP Domain Protect
Learn to prevent subdomain takeovers using OWASP Domain Protect. Enhance your application security knowledge with practical strategies and tools.
OWASP Coraza: The Way to WAF in 2023
Explore OWASP Coraza, a cutting-edge Web Application Firewall (WAF) solution, and learn how it enhances web security in 2023 through advanced features and implementation strategies.
A Weakness in Chrome and a New Hacking Technique
Explore a critical Chrome vulnerability and innovative hacking method presented by security experts. Gain insights into cutting-edge web security threats and defense strategies.