Creating Accessible Security Testing with ZAP - AppSecCali 2019 Lightning Talk
Introducing OWASP ZAP's Heads Up Display: A new UI that makes security testing more intuitive for developers and professionals, enabling efficient use of the attack proxy tool.
Browser Fingerprints for a More Secure Web - AppSecCali 2019
Explore how browser fingerprints can enhance web security by detecting session roaming and preventing account takeovers, using machine learning to identify anomalies in device configurations.
Lessons in Securing Internal Apps - AppSecCali 2019
Lessons and strategies for securing internal applications, including authentication, TLS, Content Security Policy, and leveraging WAFs. Insights on scalable approaches and using internal apps to train security engineers.
Open-Source OWASP Tools for Enhancing Penetration Testing Coverage
Explore open-source OWASP tools for efficient white box penetration testing. Learn about Code Pulse for real-time code coverage and Attack Surface Detector for comprehensive endpoint discovery to enhance security assessments.
The Path of Secure Software Development - AppSec EU 2017
Explore proactive security controls for developers to build safer applications. Learn techniques to address common vulnerabilities and integrate security throughout the development lifecycle.
Monitoring Attack Surface and Integrating Security into DevOps Pipelines
Explore methods for calculating and tracking web application attack surface, and learn to integrate security testing into CI/CD pipelines for effective DevOps practices.
The Gift of Feedback - Enhancing Application Security
Discover how to implement next-generation security by leveraging feedback, pushing security left, and making it consumable. Learn strategies to engage developers and address the challenges of securing complex software workloads.
Rise of the Machines: Automating Application Security Assessments - AppSec EU 2017
Explore automated security assessment techniques using Jenkins, HP Fortify, OWASP ZAP, and more. Learn how to efficiently scan and report vulnerabilities across diverse applications and platforms.
Bypassing XSS Mitigations Via Script Gadgets - AppSec EU 2017
Explore a novel web hacking technique bypassing XSS mitigations using script gadgets. Learn how attackers can exploit legitimate JavaScript to execute malicious code, evading common security measures.
Content Security Policy Evolution: From Whitelists to Strict-Dynamic - AppSec EU 2017
Explore Content Security Policy evolution, including 'strict-dynamic' approach, real-world implementation challenges, and strategies to address recent bypasses of nonce-based policies.
The Dark Side of Search Engine Optimization Campaigns - AppSec EU 2017
Explores how threat actors exploit SEO techniques and web attacks to manipulate search engine rankings, evaluating campaign success and proposing detection and mitigation strategies.
Essential TLS Hardening for Better Web Security
Explore essential TLS hardening techniques for enhanced web security with Justin Mayer, founder of Monitorial.com. Learn practical strategies to identify and address potential vulnerabilities in your web applications.
HTTPS Security Headers: HSTS, TLS, HPKP, and CSP Implementation - APPSEC CA 2017
Comprehensive guide to implementing HTTPS using HSTS, TLS, HPKP, and CSP. Learn best practices for secure web communication from Salesforce security experts.
SPArring with the Security of Single Page Applications
Explore security challenges in Single Page Applications with insights on automating detection and mitigation strategies for modern web development vulnerabilities.
Life of a Password
Explore the journey of passwords in cybersecurity with LinkedIn's Trust Engineering Director. Learn about authentication challenges and solutions for top websites.
The Road to Free Certificates is Paved with Good Intentions
Exploring the journey towards free SSL/TLS certificates, this talk discusses the challenges, intentions, and implications of widespread HTTPS adoption for web security and privacy.
Webhooks Hookups - Abusing API Developers
Explore the security risks of Webhooks in API development, including potential vulnerabilities, real-world examples, and preventive measures. Learn about a new toolkit for auditing Webhook exposure.
Rhyming with Hacks - The Ballad of Supply Chain Attacks
Explore supply chain attacks, their anatomy, and prevention strategies. Learn about real-life examples, existing solutions, and a new DOM monitoring approach with live demonstration.
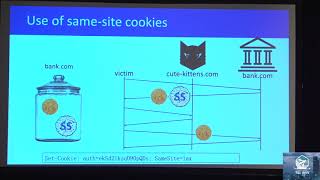
Bypassing Browser Policies and Privacy Extensions for Cookies
Explore bypasses to browser policies and extensions for cookie security. Learn about an automated framework for evaluating countermeasures against cross-site attacks and third-party tracking.
Innovation Fair for Application and Software Security Startups - OWASP Global AppSec Tel Aviv 2019
Explore innovative startups in application and software security at OWASP's first Innovation Fair. Early-stage companies pitch cutting-edge solutions, offering insights into emerging technologies and market trends.
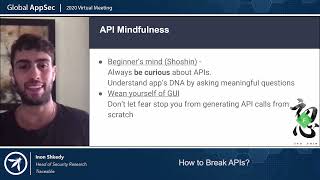
How to Break APIs - Security Testing Techniques
Comprehensive guide to identifying and exploiting vulnerabilities in APIs, focusing on practical techniques for security testing and penetration.