
Hacking and Defending APIs - Red and Blue Make Purple
Learn techniques for both attacking and defending APIs, combining offensive and defensive security perspectives to enhance overall API protection.
Vulnerabilities as Ingredients and OWASP Top 10 as Seasoning
Explore how vulnerabilities and OWASP Top 10 interact in application security, using a culinary analogy to demystify complex concepts and enhance understanding of secure development practices.
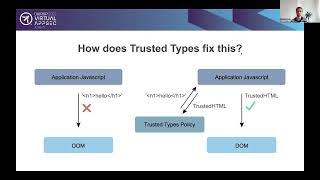
Trusted Types: A World Without XSS
Explore cutting-edge web security with Trusted Types, a powerful defense against XSS attacks. Learn implementation strategies and best practices from industry experts.
Landmines in the API Landscape
Explore potential security vulnerabilities in API development and learn strategies to mitigate risks in this insightful talk by a cybersecurity expert.
OWASP Web Honeypot Project
Explore web application security through honeypot technology. Learn deployment strategies, data analysis, and threat intelligence gathering to enhance your cybersecurity defenses.
How Security, Development, and Testing Can Work Together to Stop Recurring Vulnerabilities - OWASP Top 10
Explore strategies for integrating security, development, and testing to prevent recurring vulnerabilities in the OWASP Top 10, fostering collaboration and cultural change for secure software development.

vAPI: Vulnerable Adversely Programmed Interface - OWASP API Top 10
Explore and exploit API vulnerabilities using vAPI, a lab environment mimicking OWASP API Top 10 scenarios. Ideal for developers and penetration testers to understand and address common API security issues.
Post-DevOps: What Should We Shift-Left in Application Security?
Exploring post-DevOps challenges in AppSec, focusing on risk profiles, threat response architecture, and operational aspects to enhance security and quality in fast-paced development environments.
Big Data Intelligence - Harnessing Petabytes of WAF Statistics for Web Protection
Explore big data analysis of web application security trends, focusing on WAF statistics, attack patterns, and OWASP ModSecurity Core Rule Set accuracy. Learn to navigate and improve cloud-based web protection.
Introduction to Emerging JSON-Based ID and Security Protocols
Explore emerging JSON-based identity and security protocols with Brian Campbell, focusing on JOSE and its applications in modern authentication and authorization systems.
WAF Bypass Techniques Using HTTP Standard and Web Servers' Behavior
Explore creative techniques to bypass web application firewalls using HTTP standards and server behaviors. Learn to smuggle and reshape requests for penetration testing and bug bounty hunting.
The Bug Hunter's Methodology 2.0 - Advanced Web Application Security Testing
Explore cutting-edge techniques and tools for discovering vulnerabilities in web applications, including XSS, SSTI, SSRF, code injection, and more. Learn from expert Jason Haddix's updated methodology for effective penetration testing.
Robots with Pentest Recipes - Automating Security Testing in DevOps
Explore automated security testing using Robot Framework to integrate tools like OWASP ZAP and Nmap. Learn to create easy-to-write test recipes for continuous delivery pipelines, enabling cross-team collaboration in application security.
Visualizing Security via LANGSEC
Explore LANGSEC as an alternative to pattern matching in web security. Learn about lexers, tokenizers, and parsers, and discover how to implement LANGSEC for analyzing and preventing security attacks.
HTTPS Everywhere: Improving Web Security and Usability
Exploring Chrome's efforts to enhance HTTPS adoption: tools for debugging, reporting mechanisms for safe rollout, and strategies to improve web security.
50 Shades of AppSec - Lessons from Diverse Application Security Scenarios
Explore the diverse landscape of application security, from sophisticated to absurd, and learn valuable lessons for future security efforts in this engaging keynote by Troy Hunt.
New Methods in Automated XSS Detection - Dynamic Testing Without Static Payloads
Explore innovative dynamic methods for automated XSS detection without static payloads, including techniques for Stored XSS and custom exploit generation. Learn to overcome limitations of traditional approaches.
Exploiting CORS Misconfigurations for Bitcoins and Bounties
Explore CORS misconfigurations and their exploitation potential, including real-world examples of vulnerabilities in bitcoin exchanges and major websites. Learn about specification flaws and mitigation strategies.
Automating API Penetration Testing Using Fuzzapi
Explore automated API penetration testing with fuzzapi, addressing common vulnerabilities in REST APIs. Learn to integrate security testing into development pipelines for early detection and mitigation.
SPArring with the Security of Single Page Applications - MMA Hacker Training
Explore security challenges in Single Page Applications through an MMA analogy. Learn about SPA frameworks, REST APIs, WebSockets, and interconnectivity to become a "Mixed Multilayer Application Hacker".
Barbarians at the Gateway - DDoS and Web Attacks Against Cloud Platforms
Explore DDoS and web attacks on cloud platforms, examining tools, methods, and attacker motivations. Learn to identify patterns for better protection against evolving cyber threats.