Application Security Testing and SDLC for Developers
Learn app security testing techniques and tools for the software development lifecycle, including reconnaissance, mapping, vulnerability assessment, and exploitation.
Embedded Malicious JavaScript - Outerz0ne 2009
Explore techniques for embedding malicious JavaScript in web applications, understanding potential vulnerabilities and security risks in modern web development.
Defending Against Cross-Site Scripting (XSS) Vulnerabilities
Learn to defend against cross-site scripting (XSS) attacks. Covers vulnerability types, injection points, mitigation strategies, and practical demonstrations for developers and security professionals.
Taking on the King: Killing Injection Vulnerabilities - APPSEC Cali 2018
Explore strategies to combat injection vulnerabilities, including cross-site scripting, with insights on secure coding practices, framework design, and static analysis tools for improved application security.
Edgeguard: Client-side DOM Security Framework for Detecting Malicious Content - APPSEC Cali 2018
Introducing Edgeguard: an open framework for detecting malicious content in browsers that steals sensitive user data. Learn about this zero-footprint library's approach to enhancing client-side DOM security.
OWASP Top 10 - Application Security Risks
Explore the latest OWASP Top 10 web application security risks with expert Andrew van der Stock. Learn about critical vulnerabilities and effective mitigation strategies for safer software development.

Beyond End-to-End Encryption: Threat Models for Secure Messaging
Explore evolving threat models for secure messaging, covering advanced attacker capabilities, real-world vulnerabilities, and emerging challenges in cybersecurity and privacy protection.
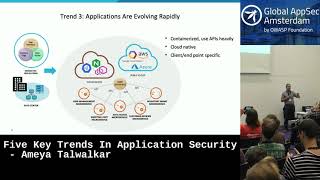
Five Key Trends in Application Security
Explore five crucial application security trends: cloud migration, CDN diversity, API proliferation, compliance challenges, and expanding attack surfaces. Gain insights into cybercriminal tactics and industry recommendations.
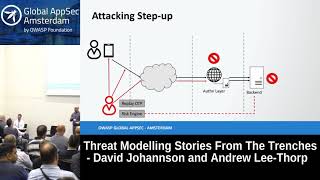
Threat Modeling Stories from the Trenches - Security Design Flaws and Solutions
Explore real-world threat modeling scenarios, design flaws, and security controls. Learn to identify vulnerabilities, understand attack vectors, and implement effective countermeasures in various systems.
Building an AppSec Program with a Budget of $0 - Beyond the OWASP Top 10
Explore OWASP projects to build a comprehensive AppSec program without spending money. Learn how to implement open-source tools for training, development, testing, and defense to create a robust security framework.
Temporal: Looking at 4 Years of Web Honeypot Attacks - Tactics, Techniques, and Trends
Analyze 9 million web honeypot attacks over 4 years, revealing attacker tactics, targeted CVEs, and global trends. Learn to identify common vs. unique threats and investigate web attack logs at scale.
Over 20 Years of SQL Injection Attacks - Refining Web Attack Detection Using Data Mining Techniques
Explore data mining techniques to refine SQL injection attack detection using CDN logs, NLP, and clustering for improved web security and emerging threat identification.
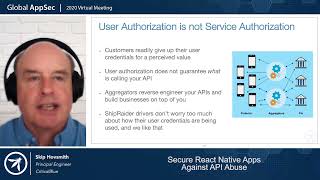
Secure React Native Apps Against API Abuse
Aprenda a proteger aplicativos React Native contra abusos de API, explorando vulnerabilidades comuns e implementando estratégias de defesa eficazes para garantir a segurança de seus aplicativos móveis.
Increasing Web Security with the Power of HTTP Headers
Explore how HTTP headers can enhance web security, focusing on practical implementation strategies and best practices for developers and security professionals.
Preventing Common Security Mistakes in the MEAN Stack - AppSec EU 2017
Learn to secure Angular applications by understanding common threats and implementing effective defenses. Covers script-based attacks, session management, CSRF, and more for robust client-side security.
On the Insecurity of JavaScript Object Signing and Encryption - AppSec EU 2017
Comprehensive analysis of JavaScript Object Signing and Encryption (JOSE) security, revealing critical vulnerabilities in popular libraries and introducing JOSEPH, an automated evaluation tool.
Exploiting CORS Misconfigurations for Bitcoins and Bounties - AppSec EU 2017
Explore CORS misconfigurations and their security implications, including real-world attacks on bitcoin exchanges and Google. Learn about subtle vulnerabilities and exploit techniques for web security professionals.
OWASP Zap - Introduction and Usage Guide
Explore OWASP Zap's capabilities for web application security testing with David Scrobonia's comprehensive overview, highlighting key features and best practices for effective vulnerability detection.
Securing Single Page Applications - Design Considerations and Pitfalls
Explore security pitfalls in Single Page Applications and learn mitigation strategies. Covers stateless design, JSON handling, caching, local storage, and resource sharing, with practical demos and key takeaways.
Threat Model-as-Code: Integrating Security into the Software Development Lifecycle
Integrating threat modeling into software development lifecycle using "Automaton" framework, enabling actionable outputs and automated security testing for improved product security.
The Evil Friend in Your Browser - Browser Extension Security Risks
Explore the hidden dangers of browser extensions, their security model limitations, and potential risks to user privacy. Learn about real-world analysis findings and discuss improved security measures.