Experimenting with Real-Time Event Feeds
Explore innovative approaches to real-time event feeds in cybersecurity, challenging traditional SIEM methods and addressing high-volume data management for improved threat detection.
Don't @ Me - Hunting Twitter Bots at Scale
Explore the Twitter bot economy and learn a three-step methodology to track down bots: dataset building, attribute identification, and classifier development for accurate large-scale detection.
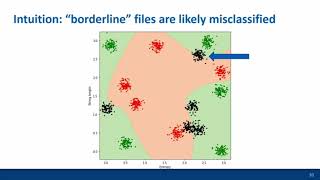
Measuring the Speed of the Red Queen's Race - Adaption and Evasion in Malware
Explore the dynamic evolution of malware and security measures using machine learning to quantify adaptation rates in the ongoing cybersecurity arms race.
Dissecting Non-Malicious Artifacts - One IP at a Time
Uncover the risks of security product interactions with online scanners, exploring information leaks, zero detection issues, and practical examples for improved cybersecurity.
DeepPhish - Simulating Malicious AI
Explore AI-driven phishing simulation techniques, including neural networks and URL prediction, to enhance cybersecurity defenses against sophisticated email-based attacks.
A Walk Through Historical Correlations Between Vulnerabilities and Stock Prices
Explore the impact of security vulnerabilities and data breaches on stock prices across industries, analyzing recovery patterns and sector-specific effects through historical data analysis.
Don't Eat Spaghetti with a Spoon - An Analysis of the Practical Value of Threat Intelligence
Explore the effectiveness of Threat Intelligence in predicting Internet malicious activity through analysis of over a million indicators across diverse real-world network sensors.
Defeating Machine Learning - What Your Security Vendor Is Not Telling You
Explore attacker strategies to defeat machine learning-based security defenses, analyze industry issues enabling these vulnerabilities, and discover novel data sourcing solutions for improved protection.
Harnessing Intelligence From Malware Repositories
Explore techniques for extracting intelligence from malware repositories using program analysis and data mining, with insights on connecting seemingly disparate cyber attacks and tracking malware trends.
Data-Driven Threat Intelligence - Metrics on Indicator Dissemination and Sharing
Análisis basado en datos de indicadores de inteligencia de amenazas y comunidades de intercambio, explorando eficiencia, calidad y superposición de fuentes durante más de un año.
Internet-Scale File Analysis
Explore TOTEM and DRAKVUF systems for large-scale malware analysis, addressing challenges in file diversity, volume, and dynamic analysis through cloud-based orchestration and hardware virtualization.
Cybercrime in the Deep Web
Explore automated detection of cybercrime in anonymous networks beyond TOR, including I2P and FreeNET. Learn about DeWA system for identifying emerging threats in the Deep Web.
Android Security State of the Union
Explore key factors driving Android security using data from millions of devices, establishing a baseline and identifying areas for community focus and research.
Multivariate Solutions to Emerging Passive DNS Challenges
Explore emerging challenges in passive DNS threat intelligence and learn multivariate solutions to overcome them, enhancing your ability to identify related malicious domains effectively.
The Myths of Software Security
Exposé of common software security myths, debunking industry surveys, best practices, and popular concepts like "shift left" and SBOMs. Challenges conventional wisdom with evidence-based insights.
What We Learned from 5 Million Books
Explore the fascinating insights gleaned from analyzing 5 million books using Google's Ngram Viewer, revealing surprising trends in language, culture, and human knowledge over centuries.
Visualizing the Medical Data Explosion
Explore cutting-edge medical visualization tools and technologies, including virtual autopsies, that help doctors analyze vast amounts of patient data for improved diagnosis and treatment.
The Good News of the Decade
Hans Rosling uses stunning visuals to reveal unreported progress in reducing child mortality, challenging conventional statistical approaches and highlighting a significant global health achievement.
Researching Secrets, Part 1
Explore techniques for uncovering hidden information and investigating confidential data in Windows systems with expert James Bamford.
Stable 10 - Getting Dirty on the CANBUS
Explore CANBUS technology and its applications in automotive systems, focusing on security implications and potential vulnerabilities in modern vehicles.
Scientific Computing for Information Security - Forging the Missing Link
Explore scientific computing's role in information security, focusing on data analytics, automation, and practical examples to enhance effectiveness and solve industry challenges.