Incident Response with Fireeye - Final Hackersploit Blue Team Training
Learn to use FireEye's Redline for incident response, including memory and file analysis. Gain practical skills in data collection, comprehensive collection, and analysis sessions for effective threat assessment.
Small Files and Big Bounties - Exploiting Sensitive Files
Explore techniques for exploiting sensitive files to uncover vulnerabilities and earn bounties. Learn from Internetwache team's expertise in identifying and leveraging small but critical files.
Open Source Malware Lab
Explore open-source tools for malware analysis, including Cuckoo Sandbox, Thug, Bro Network Security Monitor, and Volatility Framework. Learn to build an automated lab for comprehensive threat assessment.
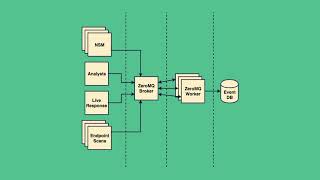
Beyond AV - Detection-Oriented File Analysis
Explore advanced file analysis techniques for enhanced threat detection, focusing on Strelka's features and applications in enterprise security.
Internet-Scale File Analysis
Explore TOTEM and DRAKVUF systems for large-scale malware analysis, addressing challenges in file diversity, volume, and dynamic analysis through cloud-based orchestration and hardware virtualization.

Offensive Anti-Analysis
Explore open-source malware analysis tools and techniques for file, URL, network traffic, and memory image analysis. Learn to build an automated analysis lab by chaining tools together.
Your Mac Defenestrated Post OSXploitation Elevated - FuzzyNop Noncetonic
Explore advanced Mac post-exploitation techniques, including persistence methods, keychain access, and system event manipulation for enhanced security understanding.
Make Troy, Not War - Case Study of the Wiper APT in Korea, and Beyond
Explore the Wiper APT in Korea, analyzing its impact, components, and connections to other cyber operations. Gain insights into this sophisticated malware and its global implications.
Google Attacks
Explore Google attack techniques, including pentest examples, special characters, and keywords. Learn about honeypots and controlling Google data for enhanced cybersecurity.
The 3 Way16 Hardy Har Har Har Har File Collection and Analysis for Malware
Explore HAR file collection and analysis techniques for malware detection, focusing on innovative approaches to enhance cybersecurity and threat intelligence.
Using Past Data to Determine Relevance in Autopsy
Explore Autopsy's File Discovery UI and Central Repository for efficient digital forensics. Learn how past data analysis enhances file prioritization and streamlines investigations.