How We Hacked LinkedIn and What Happened Next
Explore an advanced XSS attack on LinkedIn, dissecting its mechanics and aftermath. Gain insights into web security vulnerabilities and learn from a hacker's perspective.
How JSON Web Tokens Define the Future of Mobile Driver's License and Digital Identity
Explore JSON Web Tokens and their revolutionary role in mobile driver's licenses, from basic concepts to practical implementations for secure digital identity verification.
Exploring Security Vulnerabilities in Flutter Mobile Applications
Discover critical security vulnerabilities in Flutter apps through reverse engineering techniques, focusing on hardcoded credentials and using tools like B(l)utter to analyze and protect mobile applications.
API Security Fundamentals - Understanding Modern API Threats and Protection
Dive into API security challenges and solutions with Filip Verloy, exploring why APIs are becoming prime attack vectors and how traditional security measures fall short in protecting modern applications.
Understanding JWT: Implementation and Security Best Practices in Python
Discover how to implement and secure JSON Web Tokens (JWT) in Python applications, covering validation techniques, authorization purposes, and best practices for safer implementation.
Understanding CSRF and SSRF Web Security Vulnerabilities - Demo and Examples
Explore CSRF and SSRF web security vulnerabilities through practical demonstrations, understanding attack mechanisms, key differences, and essential prevention strategies for robust application security.
Azure AD Reconnaissance Using OSINT Tools
Discover how to gather intelligence on Azure AD environments using OSINT tools, including domain enumeration, authentication methods, and user information for security assessment purposes.
Clocks Have Ears - Timing and Browser-Based Local Network Port Scanner
Discover how browser-based timing attacks can be used for local network port scanning, exploring innovative security techniques and network vulnerability assessment methods.
Time-Based SQL Injection Techniques and Defense Strategies
Dive into time-based SQL injection techniques through Operation GhostShell, featuring live demos and defense strategies for protecting against sophisticated database vulnerabilities.
Exploiting Localhost APIs From The Browser - Zero-Day Vulnerability and Attack Techniques
Discover how browser-based attacks exploit localhost services through a zero-day vulnerability, featuring live demonstrations of remote code execution and novel attack techniques targeting developers behind firewalls.
Decoding Galah - An LLM-Powered Web Honeypot
Discover how LLM-powered honeypot Galah revolutionizes web security by dynamically simulating multiple applications and analyzing attacker behavior through intelligent HTTP response generation.
The Dual-Edged Sword of EV and Solar APIs in Grid Security
Explore critical vulnerabilities in EV charging and solar system APIs, examining potential cyber threats to power grid infrastructure and the urgent need for enhanced security measures.
Relative Path File Injection: The Next Evolution in RPO
Discover how Relative Path File Injection attacks can turn trusted websites into malware delivery platforms, exploring detection methods and real-world implementations through practical demonstrations.
Securing Frontends at Scale - Paving the Way to Post-XSS World
Discover cutting-edge strategies for defending against XSS vulnerabilities, exploring Google's proven security implementations and future-focused approaches for protecting web applications at scale.
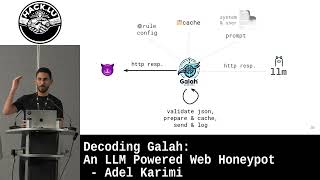
Decoding Galah - An LLM Powered Web Honeypot
Discover how to implement an LLM-powered web honeypot system through Galah, exploring advanced security techniques for detecting and analyzing potential cyber threats.
Nothing To See Here - On Cloaking Malicious Web Content Delivery
Uncover sophisticated techniques used by cybercriminals to hide malicious web content delivery through cloaking mechanisms and learn effective detection and prevention strategies.
Fast IP Address Matching in Elixir with Radix Trees and Persistent Term
Optimize IP address matching in Elixir using radix trees and persistent_term. Learn efficient data structures and compare GenServers, ETS, and persistent_term for high-performance solutions.
Fortifying gRPC Microservices - Beyond JWT with mTLS and SPIFFE
Explore secure gRPC microservices setup using mTLS and SPIFFE. Learn certificate management, key distribution, and modern alternatives to JWT for robust service-to-service authentication.
Refactoring the Web - Democratizing Data Ownership and Control
Explore the concept of a decentralized web platform that empowers individuals to own and control their personal data, revolutionizing online identity and data security.
One for Auth and Auth for One - Authentication and Authorization Crash Course
Explore authentication and authorization in modern apps, covering OAuth 2.0 and OIDC standards. Learn key concepts and practical applications for robust user and API security.
Apache APISIX for Enterprise API Lifecycle Management
Explore modern API lifecycle management with Apache APISIX, a cloud-native gateway. Learn how to efficiently manage APIs in microservice architectures for enterprise stability and security.