Securing Web Applications and APIs with ASP.NET Core 2.2 and 3.0
Explore ASP.NET Core's security features, focusing on API security with IdentityServer4. Learn about authentication, authorization policies, and resource-based security for modern web applications.
Adding Business Logic to Your Tokens - What Could Possibly Go Wrong
Explore the pitfalls of adding excessive business logic to tokens in identity servers, and learn best practices for token management and security.
Securing the Web with AI
Explore innovative AI-driven web security methods, including facial recognition for 2FA, user behavior analysis, and machine learning to detect fraudulent content, enhancing protection for all users.

Opening Doors with JSON Web Tokens
Explore secure IoT access using JSON Web Tokens, featuring a live door demo. Learn to transmit credentials safely, grant remote access, and apply concepts to various IoT devices.
25 Years of SSL - Secure - ish - Sockets Layer
Explore the 25-year evolution of web encryption, its challenges, recent advancements, and future prospects in securing online communications.
Modern Web Vulnerabilities 2020
Explore modern web vulnerabilities, including insecure deserialization, SSRF, ESI injection, prototype pollution, and HTTP request smuggling, with demos and prevention strategies.
OWASP TOP 10 Security API 2023 for GraphQL - An Interactive Workshop for Developers
Master production-ready GraphQL security techniques with hands-on exercises, following OWASP TOP 10 API 2023 standards. Apply essential concepts in real-world scenarios using Learn.Escape.Tech platform.
Continuous OpenAPI Security Tests on Kubernetes with Testkube and ZAP
Learn to implement continuous security testing for cloud-native apps using ZAP and Testkube on Kubernetes, integrating with GitOps for efficient and regular product delivery.
Securing Serverless: AWS Lambda and Resilient Architectures
Explore practical approaches for integrating security in AWS Lambda architectures. Learn to handle sensitive data and implement automated compliance checks for robust serverless systems.
Sustainable API Management - Best Practices and Strategies
Explore sustainable API management strategies to enhance security, scalability, and efficiency in your DevSecOps practices.
Next Steps for Browser Privacy: Pursuing Protections Beyond Extensions
Exploring privacy improvements beyond browser extensions, focusing on Brave's innovative approaches to enhance user protection and encourage broader research in web privacy.
Why Even Experienced and Highly Intelligent Developers Introduce API Vulnerabilities
Explores why experienced developers introduce vulnerabilities through API misuse, examining cognitive factors and personality traits affecting code security detection abilities.
Internal Affairs - Hacking File System Access from the Web
Explore vulnerabilities in the File System Access API, revealing how malicious websites can exploit it for arbitrary code execution and bypass security measures.
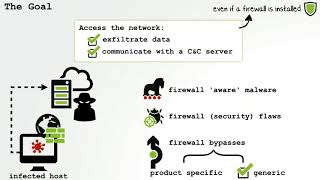
Fire & Ice - Making and Breaking macOS Firewalls
Explore macOS firewall creation and vulnerabilities, covering kernel-level socket filtering, user-mode communication, secure installation, and self-defense mechanisms. Learn about firewall bypasses and potential weaknesses.
Bridging the Gap Between Research and Practice in Intelligently Bypassing WAF
Explore AI-driven techniques for bypassing web application firewalls, addressing practical challenges in payload diversity and difficulty balancing. Learn innovative approaches to enhance cybersecurity defenses.
Birth of the Post-Quantum Internet
Explore the pivotal shift to post-quantum encryption, its impact on cybersecurity, and the challenges of implementing post-quantum certificates for the public Web.
Interactive Brokers Web API - Docker Tutorial for Full Stack Stock App - Part 1
Learn to build a full-stack stock app using Interactive Brokers REST API and Docker. Explore containerization, authentication, and web application features for efficient stock trading and portfolio management.
Securing Tomcat: Key Considerations and Best Practices
Learn key security considerations, features, and best practices for securing Tomcat, a widely-used Java-based web server and servlet container.
GenAI for Enterprises - Practical Considerations From Pilot to Scale
Explore practical considerations for implementing GenAI in enterprises, from pilot to scale. Address challenges and learn successful approaches for large-scale AI deployment.
Tick Tock - Building Browser Red Pills from Timing Side Channels
Exploring browser-based red pills to detect virtual environments, their impact on web malware scanners, and potential mitigations for enhanced cybersecurity.
Zero Trust Security for Your APIs
Explore Zero Trust Security for APIs: Learn the model, architecture, and implementation steps to protect your API ecosystem from attacks and abuse.