Meddling Middlemen - Empirical Analysis of the Risks of Data-Saving Mobile Browsers
Empirical analysis of data-saving mobile browsers, exploring their effectiveness, impact on usability, and potential security risks. Examines proxy server configurations, privacy concerns, and proposes improved designs.
A Formal Security Analysis of the W3C Web Payment APIs - Attacks and Verification
Explore formal security analysis of W3C Web Payment APIs, including potential attacks and verification methods. Learn about browser models and gain insights into API security.
Docker for Pentesting & Bug Bounty Hunting
Explore Docker's potential for pentesting and bug bounty hunting. Learn to set up Kali Linux, OWASP Juice Shop, and Bug Bounty Toolkit, enhancing your cybersecurity skills and workflow efficiency.
OPSEC and Personal Security Guide - Cybertalk Episode 7
Comprehensive guide on personal security and OPSEC, covering tools, techniques, and best practices to enhance digital safety and protect against cyber threats.
How to Win Over Security Teams and Gain Influence as a Hacker
Insights from experienced hackers on effective strategies, tools, and etiquette for successful bug bounty hunting and building positive relationships with security teams.
Advanced Hacking Workshop - Techniques and Personal Insights
Top hackers share advanced techniques, personal stories, and insights on bug bounty hunting. Learn from experts Frans Rosén and Peter Yaworski about URL validation, third-party scripts, and building a hacking career.
Unique Mindset - Hacking Techniques and Favorite Findings
Explore zseano's unique hacking mindset through real-world examples, favorite findings, and insights on identifying critical vulnerabilities in web applications.
API Security 101 by Sadako
Explore API security fundamentals, common vulnerabilities, and real-world examples. Learn testing methodologies, fuzzing techniques, and gain insights from notable bug discoveries in this beginner-friendly introduction.
How the Crowd Outperforms Traditional Security Testing
Explore how crowdsourced security testing outperforms traditional methods, with insights on implementation, benefits, and real-world examples from successful bug bounty programs.
Fuzzing XSS Sanitizers for Fun and Profit - Tom Anthony
Explore XSS sanitizer fuzzing techniques with Tom Anthony, from his hacking past to current cybersecurity insights. Learn about innovative approaches to discovering vulnerabilities in web applications.
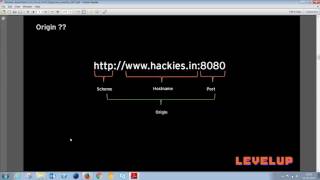
Browser Exploitation for Fun and Profit - Dhiraj Mishra, Bugcrowd's LevelUp 2017
Explore browser vulnerabilities, their root causes, and exploitation techniques. Learn about interesting security flaws discovered during research and gain insights into browser exploitation.
Do You Like Fuzzing? - Abhijeth, Bugcrowd's LevelUp
Explore REST API fuzzing with Fuzzapi, an automated tool for detecting vulnerabilities in web/mobile applications and improving API security.
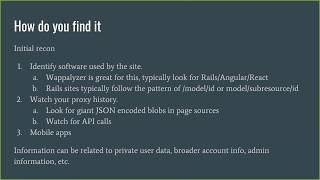
Hidden in Plain Site - Disclosing Information via Your APIs - Peter Yaworski, Bugcrowd's LevelUp 2017
Explore information disclosure vulnerabilities in APIs and HTML sources, focusing on Rails design patterns and front-end frameworks. Learn detection techniques and real-world examples.
A Starters Guide to Pentesting with OWASP
Learn essential web security concepts, OWASP Top 10 vulnerabilities, and practical pentesting techniques to enhance your cybersecurity skills and protect web applications effectively.
Security and Hacking - Lessons from the MySpace Worm
Explore hacking insights from Samy Kamkar, renowned for the MySpace worm, as he shares his expertise and experiences in cybersecurity at the Security@ Conference.
How I Hacked 55 Banks and Cryptocurrency Exchanges - LevelUpX Series 3
Alissa Knight reveals tactics used to breach 55 financial institutions, offering insights into vulnerabilities in FinTech apps and APIs. Learn from a veteran hacker's experience in cybersecurity.
Car Hacking Explained for Bug Hunters - Automotive Security Vulnerabilities and Methodologies
Explore automotive security vulnerabilities, from IoT to CAN bus hacking. Learn methodologies, attack surfaces, and bug prioritization for car hacking, covering infotainment systems, APIs, and mobile apps.
Code That Gets You Pwned - Common Vulnerabilities in Golang, Ruby, and Python
Explore non-obvious vulnerabilities in Golang, Ruby, and Python, covering topics like Tempfile, path.Clean, URL parsing, and Unicode security implications.
Crowdsourced Security: Insights from Industry Pioneers - Founder AMA
Explore crowdsourced security with industry pioneers, discussing its importance, future trends, and the motivations of bug bounty hunters in addressing sophisticated vulnerabilities.
Till REcollapse - Fuzzing the Web for Mysterious Bugs
Explore web fuzzing techniques for uncovering mysterious bugs with André Baptista. Learn strategies to identify impactful vulnerabilities and enhance your ethical hacking skills.
Hacking, Certificate Transparency, and TruffleHog - A Discussion with InsecureNature
Insightful discussion on hacking techniques, security tools, and bug bounty strategies, featuring expert insights on Certificate Transparency and TruffleHog for enhanced cybersecurity practices.