Exploring Web Applications Through Their JavaScript - Uncovering Hidden Information
Descubre cómo analizar el código JavaScript de sitios web para encontrar información valiosa como API Keys, endpoints internos y usuarios, mejorando tus habilidades en seguridad web.
Mi Camino a los 2500 Puntos de Reputación en HackerOne
Experiencia en bug bounty: desde los inicios hasta 2500 puntos en HackerOne. Consejos sobre reportes, cálculo de riesgos y colaboración en la comunidad de cazadores de vulnerabilidades.
Hosting Tutorial: Deploy NodeJS Apps in Production on Linux VPS - Tutorial 97
Learn to deploy NodeJs applications on a Linux VPS for production environments. Gain practical skills in server setup, configuration, and best practices for hosting web applications securely and efficiently.

Hosting Multiple Websites on One Single Hosting Server - Tutorial 96
Learn to host multiple websites on a single server efficiently. Discover techniques for optimizing server resources, managing domains, and configuring virtual hosts for improved web development workflow.
Implementing Google reCAPTCHA in Python Django
Learn to implement Google reCAPTCHA in Python Django to enhance website security and prevent automated bot submissions, with step-by-step guidance and practical demonstrations.

Saving PHP Website from a Potential XSS Attack - Tutorial 64
Learn to protect your PHP website from XSS attacks. Discover techniques to sanitize user input, validate data, and implement security measures to prevent cross-site scripting vulnerabilities.
Hunting Web Vulnerabilities - Introduction to Ethical Hacking - Workshop 3
Taller práctico sobre hacking ético de sitios web. Aprende técnicas legales para identificar vulnerabilidades, comprender el funcionamiento de la web y explorar oportunidades en seguridad informática.
Hunting and Scraping with Favicons - DefCamp 2023
Explore favicon hunting techniques for cybersecurity reconnaissance. Learn innovative methods to gather valuable information from website icons, enhancing your digital investigation skills.
Siber Güvenlik ve İnsan Hackleme Sanatı
Siber güvenlik uzmanı Okan Algün, sosyal mühendislik ve insan hackleme sanatı hakkında bilgi veriyor. Güvenli sandığımız dijital platformların riskleri ve siber suçlardan korunma yöntemleri ele alınıyor.
OWASP ModSecurity: Web Application Firewall Overview
Explore OWASP ModSecurity's features and implementation for enhancing web application security through this concise presentation by Ervin Hegedüs.
La lucha contra el auge de la inteligencia artificial - BOT-Apocalypse Now
Estrategias para combatir ataques BOT en la era de la IA, enfocándose en amenazas móviles, reducción de costos WAF y protección contra fraudes, DDoS y abusos de API.
Bumpy Roads - Exploring Security Vulnerabilities in Regional Carsharing Systems
Entdecke Schwachstellen und unsichere Software eines regionalen Carsharing-Anbieters. Tauche ein in ein Korallenriff voller Sicherheitslücken und lerne über Web-Applikationen, deren Schwachstellen und unsicheres Design.
How to Build a Large-Scale API Hub
Explore building a large-scale API hub, covering API management, automated delivery, and lifecycle. Learn to address challenges in distributed organizations and add business value.
Certificate Transparency: Detecting Malicious Certificates and Phishing Attacks
Explore Certificate Transparency to protect your website from impersonation attacks. Learn integration techniques for monitoring systems and detecting malicious TLS certificates.
Building Data Breach and Subpoena Resistant Applications - Philly ETE 2017
Explore cryptographic techniques and messaging systems to build applications resistant to data breaches and subpoenas, setting new standards for user data security.
Securing Software by Construction: From Research to Industry - Philly ETE 2016
Explore techniques for building secure software from the ground up, bridging the gap between academic research and industry practice in cybersecurity, and addressing challenges in commercializing long-term security solutions.
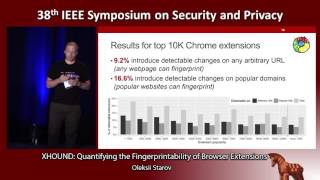
XHOUND - Quantifying the Fingerprintability of Browser Extensions
Quantifying browser extension fingerprintability and its impact on user privacy. Explores detection methods, analyzes popular extensions, and discusses implications for online tracking and user identification.
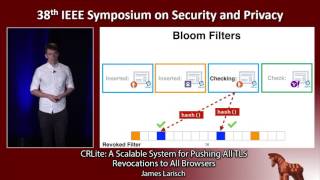
CRLite - A Scalable System for Pushing All TLS Revocations to All Browsers
Explore a scalable system for efficient TLS certificate revocation checking in browsers, reducing latency and enhancing privacy while maintaining low bandwidth costs.
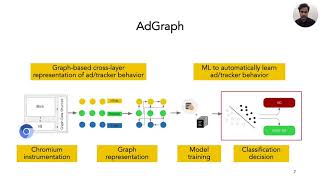
AdGraph: A Graph-Based Approach to Ad and Tracker Blocking
Innovative graph-based machine learning approach for detecting online ads and trackers, offering improved accuracy and performance compared to traditional filter list methods.

Tracking Browser Fingerprint Evolutions - Antoine Vastel
Explore browser fingerprint tracking techniques, including FP-STALKER's rule-based and hybrid approaches, to understand long-term user identification without cookies.
Detecting Filter List Evasion With Event-Loop-Turn Granularity JavaScript Signatures
Explore techniques for detecting filter list evasion using JavaScript signatures, focusing on event-loop-turn granularity and privacy-relevant aspects of web tracking.