
Cyber Security Fundamentals and Best Practices for Software Development
Master essential cybersecurity practices for modern software development, from threat assessment and incident response to secure system architecture, encryption protocols, and fostering a security-conscious development culture.
AWS Advanced Networking - Full Course - Part 1
Explore AWS advanced networking concepts, from VPC essentials to SSL/TLS with ACM. Master load balancers, security features, and efficient network architectures for cloud computing.
API Security in the Age of Microservices
Explore API security challenges in microservices architectures and learn strategies for distributed security, including gateways, service mesh, authentication, and network segmentation.
Response Smuggling - Pwning HTTP/1.1 Connections
Explore advanced HTTP response smuggling techniques, including protocol vulnerabilities, session hijacking, and response scripting, with real-world demonstrations on major ERP systems.
Browser Hacking With ANGLE
Explore browser hacking using ANGLE, covering WebGL basics, vulnerability analysis, and RCE exploitation in macOS. Learn about ANGLE architecture and specific CVEs in Chrome and Safari.
Deploying WebAuthn at Dropbox Scale - Second Factor and Beyond
Explore WebAuthn deployment at Dropbox, covering second factor authentication and advanced implementations for enhanced security at scale.
All That Glitters Isn't Chrome - Hunting for Suspicious Browser Extensions
Explore techniques for identifying and analyzing suspicious browser extensions, focusing on Chrome, to enhance cybersecurity awareness and protection strategies.
At Your Service - Abusing the Service Workers Web API
Explore potential security vulnerabilities in the Service Workers Web API and learn techniques for exploiting them to compromise web applications and user data.
The Power of Guardrails - How to Slash Your Risk of XSS in Half
Learn effective strategies to significantly reduce XSS vulnerabilities in web applications through powerful guardrails, enhancing overall security and protecting against common attack vectors.
Ghosts of XSS Past, Present & Future
Explore the evolution of Cross-Site Scripting (XSS) vulnerabilities, their impact on web security, and strategies for mitigation in this comprehensive presentation by a leading industry expert.
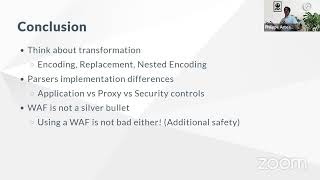
Web Application Firewall Workshop
Hands-on workshop exploring Web Application Firewall bypass techniques, including encoding, SQL injection, protocol switching, and syntax alternatives. Practical exercises with in-depth explanations for each method.
Request Smuggling 101
Explore HTTP Request Smuggling attacks, risks, and payloads. Learn to detect and mitigate vulnerabilities in load balancers and proxies. Includes live demonstration and practical mitigation strategies.
Your Chakra Is Not Aligned
Exploring Microsoft Chakra's JavaScript engine implementation, its vulnerabilities, and techniques for identifying bugs in new ECMAScript engines to enhance browser security.
Do We Get Stuff Done? We Don't Get Stuff Done? Or Do We? Or Will We?
Exploring web security's 20-year stagnation, this talk examines past mistakes and proposes future solutions, aiming to renovate mindsets and break the cycle of recurring vulnerabilities.
Breaking Formation - From an Error Message to Internal AWS Infrastructure
Explore a critical AWS CloudFormation vulnerability, its impact on cloud security, and the disclosure process. Gain insights into cloud infrastructure vulnerabilities and future research directions.
CSRF Finder as a Mozilla Addon
Discover how to create a Mozilla addon for detecting CSRF vulnerabilities in web applications, enhancing your security testing capabilities and web development skills.
Pentesting Without Pentesters
Innovative scanning technology enables functional test cases to produce security findings, bridging the gap between development and security testing without dedicated pentesters.
De Low a Medium - Como Elevar el Riesgo de tu Inyección de HTML
Técnicas avanzadas para elevar la severidad de inyecciones HTML en sistemas web, explorando métodos no convencionales más allá de las vulnerabilidades XSS tradicionales.
Ekoparty #UniTalks Colombia - HTTP Request Smuggling
Explicación detallada sobre la vulnerabilidad HTTP Request Smuggling, sus implicaciones en la seguridad web y cómo los atacantes pueden explotarla para ejecutar diversos ataques en aplicaciones con arquitecturas de múltiples servidores.
Response Smuggling - Exploiting HTTP/1.1 Connections
Explore response pipeline desynchronization in HTTP Smuggling, a novel attack vector for bypassing restrictions and breaching web application security in complex systems.
Servo - Designing and Implementing a Parallel Browser
Explore Servo, an experimental browser engine designed for multi-core hardware, focusing on parallelization and security through Rust. Learn about its goals, design, and potential impact on web browsing.