Kubernetes SIG Auth Deep Dive
Explore Kubernetes authentication, authorization, and security features with experts from Google, Microsoft, and Red Hat. Learn about ongoing projects and opportunities for involvement in SIG Auth.
DevOps, CI, APIs, and Security Gone Agile
Explore agile security practices for modern IT environments, covering infrastructure, apps, APIs, and source code. Learn to adapt security processes to rapid deployment cycles and DevOps methodologies.
DevOps for the Discouraged - Integrating Security into Continuous Delivery
Equipping security teams with tools and strategies to integrate into DevOps practices, focusing on continuous delivery pipelines and open-source security tools for web application stacks.
Production Workload Identity with SPIRE
Explore SPIRE for secure workload authentication in cloud-native architectures. Learn its core design, implementation in production environments, and upcoming features for enhanced identity management.
Scratch Containers and the Supply Chain Trouble
Explore scratch containers, their benefits in reducing vulnerabilities, and potential challenges in software composition analysis. Learn about security implications for containerized applications.
Using Workload Identity Federation to Increase Developer Productivity
Explore secure API token management using Kubernetes features like Service Account Token Volume projection and Workload Identity Federation for enhanced developer productivity.
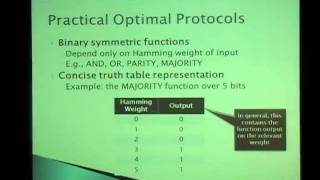
Secure Computation on the Web- Computing without Simultaneous Interaction
Explore secure computation in client-server models, addressing limitations and presenting practical protocols for web-based scenarios without simultaneous client interaction.
Exploiting PKI for Fun and Profit - The Next Yellow Padlock Icon
Explore PKI vulnerabilities and exploitation techniques for enhanced cybersecurity awareness. Learn about potential threats to secure communication systems and strategies for mitigation.
Transport Layer Security (TLS) - Session 11
Explore the intricacies of Transport Layer Security (TLS) protocols, enhancing your understanding of secure communication in modern networks.
Mesos Security Exposed - Recent Advancements and Features
Explore advanced security features in Apache Mesos, including API authentication, executor authentication, secrets management, cryptography support, and enhanced isolation techniques.
CSS for Evil, Not Good
Explore the potential misuse of CSS for deception and manipulation in web design, examining ethical implications and raising awareness about responsible development practices.
UCAN Community Call - User Controlled Authorization Networks Update
Explore User Controlled Authorization Networks (UCANs), an offline-first authorization method for distributed systems. Learn about its features, benefits, and progress towards v1.0 release.
Authorization in Software - How Box Does Authorization
Explore Box's multi-layered approach to authorization, covering security challenges, user permissions, and API access in file-sharing and collaboration platforms.
Authorization - Security Deep-Dive with Okta - Part 2
Explore authorization concepts like access control and delegated authorization. Learn practical security tips for React Native apps, balancing user experience with robust protection against malicious forces.
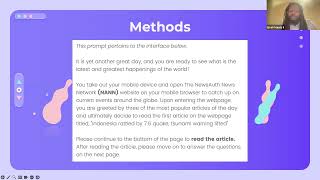
Usable News Authentication: Impact of Cryptographic Information Presentation and Location
Exploring how visual and textual presentation of cryptographic information affects user perception of news credibility and trustworthiness in online environments.
Securing LLMs in Kubernetes - Best Practices
Explore best practices for securing and operating Large Language Models in Kubernetes, including deployment, ingress control, and protection against data leakage in production environments.
Securing AI Apps with the OWASP Top Ten for Large Language Models
Explore strategies to mitigate risks in generative AI using OWASP Top 10 for LLMs. Learn best practices for building secure and responsible AI applications in your environment.
Securing Azure OpenAI Apps in the Enterprise
Explore core security controls for Azure OpenAI in enterprises. Learn available measures, identify gaps, assess effectiveness, and implement robust protection strategies.
Ingress-Nginx and 2024 Plans - Roadmap and Future Developments
Explore ingress-nginx's 2024 roadmap, including modsecurity, potential LUA replacements, and challenges in decoupling control and data planes. Gain insights into future developments and strategies.
Asymmetric Encryption - A Deep Dive
Explore the mathematical foundations, evolution, and future of asymmetric encryption algorithms like RSA and ECDSA, including their strengths, vulnerabilities, and post-quantum implications.
Asymmetric Cryptography - A Deep Dive
Explore asymmetric cryptography's foundations, evolution, and future. Uncover RSA and ECDSA algorithms, their limitations, and post-quantum implications in this mathematical journey through digital security.