Squeezing the Last Drop Out of OWASP Juice Shop
Explore advanced hacking techniques and security challenges in this hands-on session with OWASP Juice Shop, led by its creator Bjoern Kimminich.
Server-Side Prototype Pollution: Detection and Exploitation Techniques - OWASP AppSec Dublin
Explore server-side prototype pollution vulnerabilities, detection techniques, and prevention strategies in web applications with security expert Gareth Heyes.
Defending Against New Phishing Attacks that Abuse OAuth Authorization Flows
Explore advanced techniques to protect against sophisticated phishing attacks exploiting OAuth authorization flows, enhancing your cybersecurity defenses.
JavaScript Obfuscation: It's All About the Packers
Explore JavaScript obfuscation techniques, focusing on packers and their impact on code security and readability in this informative OWASP presentation.
Securing an API Ecosystem with OAuth 2.0
Explore OAuth 2.0 implementation for robust API security in this comprehensive talk by Philippe De Ryck, covering best practices and ecosystem protection strategies.
Package Transparency for WebAssembly Registries
Explore WebAssembly package distribution with warg, a new registry protocol offering enhanced supply chain security through Package Transparency, verifiable data structures, and easy detection of operator compromise.
Lessons from 7 Headline-Grabbing Cloud Security Breaches
Analyze 7 real cloud security breaches, exploring attack methods, defense strategies, and specific takeaways to enhance cloud infrastructure protection and avoid similar vulnerabilities.
Geeking Out with WebAssembly and Kubernetes Using ContainerD Shims
Explore WebAssembly integration with Kubernetes using ContainerD shims, covering features, risks, and practical demonstrations for cloud-native development.
ATOR - Authentication Token Obtain and Replace Burp Plugin V3
Streamline complex authentication testing with ATOR v3 Burp Plugin. Automate token handling, OTP validation for JavaScript frameworks. Simplifies configuration and debugging for efficient security assessments.
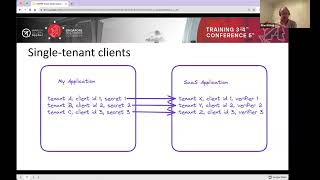
Cross-Tenant Request Forgery Attack in Multi-Tenancy Environments
Unveiling security vulnerabilities in multi-tenant SaaS platforms using OAuth, focusing on the "Cross-Tenant Request Forgery" attack and discussing potential remediations for developers.

HTTP Request Smuggling - Web Application Hacking Techniques
Explore HTTP Request Smuggling techniques for web application security, uncovering vulnerabilities and enhancing your hacking skills.
API Governance: Creating a Success Recipe
Learn to craft a robust API governance structure, bringing order to your API landscape through clear ownership, documentation, discovery, and inventorying for consistency, scalability, and security.
Securing Identity and Authorization in Microservices
Explore Transaction Tokens (TraTs) for securing microservices, enhancing user identity and context in call chains, and defending against various attacks in distributed architectures.
Security Safari: A Journey Through the Wilderness of Securing Budding Opensource Projects
Explore essential security guidelines for open-source projects, distilled from CNCF and OpenSSF resources. Learn actionable steps to implement fundamental security measures from day one.
Unveiling the Vulnerabilities: Hacking Cloud Native Apps and Discovering the Silver Lining
Explore cloud-native app vulnerabilities, including OAuth, storage services, and API-based microservices. Learn to identify, exploit, and mitigate risks through penetration testing and automated tools.
Complete MERN Stack Blog App Tutorial - React, Node.js, Express, MongoDB
Build a full-stack MERN blog app with user authentication, CRUD operations, and responsive design. Learn React, Node.js, Express, MongoDB, Context API, and JWT for a comprehensive web development experience.
Multi-Scheme Password Hashing Implementation in Rust - Episode 4
Implement multi-scheme password hashing in Rust with HMAC/SHA512 and Argon2, featuring auto-upgrade and static dispatch for enhanced web application security.
SBOM for Cloud Services - Challenges and Applications
Explore the concept of Software Bill of Materials for cloud services, its challenges, and potential applications in enhancing security and transparency in cloud computing.
OAuth Security - Best Practices and Implementation Guidelines
Explore OAuth security essentials with expert Jim Manico, covering key concepts, best practices, and potential vulnerabilities in this comprehensive presentation.
Web Security: Broken by Default?
Explore web security challenges, focusing on browser vulnerabilities and emerging standards to address these issues. Learn how developers can enhance application security beyond code fixes.
Don't Get Owned by Dependencies - How Firefox Uses WebAssembly for Protection
Explore Firefox's innovative use of WebAssembly to create lightweight sandboxes for third-party C libraries, enhancing security against memory vulnerabilities and zero-day attacks.