Web Application Honeypot Threat Intelligence - Techniques and Implementation
Explore web application honeypots for threat intelligence, using ModSecurity and OWASP Core Rule Set to capture attacker activity and protect software against emerging threats.
Purple Teaming with OWASP PurpleTeam - Security Regression Testing
Explore OWASP PurpleTeam, a security regression testing tool for web apps and APIs. Learn its components, setup, and workflows for early detection of application security defects in build pipelines.
Purple Teaming with OWASP PurpleTeam
Explore OWASP PurpleTeam: a security regression testing tool for web apps and APIs. Learn its journey, architecture, benefits, setup, and various workflows for effective implementation in build pipelines.
OWASP ZAP: Introduction to Web Application Security Testing
Explore OWASP ZAP's latest features, including automation, reporting, and out-of-band testing. Learn how this open-source tool enhances web application security through practical demonstrations and updates.
OWASP Top 10 - Introduction to Web Application Security Risks
Comprehensive overview of OWASP Top 10, exploring critical web application security risks and effective mitigation strategies for developers and security professionals.

OAuth 2.0 and OpenID Connect for Single Page Applications
Explore OAuth 2.0 and OpenID Connect implementation for single-page applications, enhancing security and user authentication in modern web development.
HTML5 Security Features - Advantages Over Traditional Web Technologies
Exploring HTML5's security features and comparing them to traditional techniques. Demonstrates how HTML5 APIs offer improved security for cross-domain communication, client-side persistence, and protection against common web vulnerabilities.
OWASP ZAP Advanced Features for Web Application Security Testing
Explore advanced features of OWASP ZAP for web application security testing, including handling non-standard apps, client-side testing, fuzzing, scripting, and more with expert Simon Bennetts.
Warning Ahead: Security Storms Brewing in JavaScript
Explore JavaScript vulnerabilities, including unique issues, third-party platform exploits, and HTML5 risks. Learn about emerging security threats and their impact on enterprise data and user safety.
Million Browser Botnet - Creating a JavaScript-Driven Browser Botnet for DDoS Attacks
Explore how online advertising networks can be exploited to create massive browser botnets for various malicious activities, including DDoS attacks and password cracking, without leaving traces.
Hack.me: A New Way to Learn Web Application Security
Explore a free, browser-based platform for practicing offensive techniques on vulnerable web applications. Learn about OWASP Top 10, CMS vulnerabilities, and latest exploits in a sandboxed environment.
HTTP Time Bandit - Identifying Web Application Performance Bottlenecks
Explore web application vulnerabilities and efficient DOS/DDOS attack techniques using HTTP Time Bandit tool. Learn to identify resource-consuming pages for improved security or targeted attacks.
RailsGoat: Vulnerable Ruby on Rails Framework for Security Education
Explore RailsGoat, a vulnerable Ruby on Rails app designed to educate developers and security professionals on OWASP Top 10 vulnerabilities and additional security issues.
The 2013 OWASP Top 10 - Understanding Web Application Security Risks
Comprehensive overview of OWASP Top 10 2013, covering changes, risks, and mitigation strategies for web application security. Essential for developers and security professionals.
HTML5 - Security Risks and Tools in Modern Web Applications
Explore HTML5's security implications, from potential risks to innovative tools for enhanced authentication and session tracking. Learn how new features impact web application security.
OWASP Zed Attack Proxy: Latest Features and Developments - Lecture
Explore web application security with OWASP's Zed Attack Proxy. Learn key features, including Plug-n-Hack and Zest scripting, suitable for both novice and experienced penetration testers.
Anatomy of a Cloud Security Breach - 7 Deadly Sins
Explore 7 real cloud security breaches, their attack patterns, and defense strategies. Learn key differences between cloud and on-premise threats, and gain actionable insights to protect your cloud infrastructure.
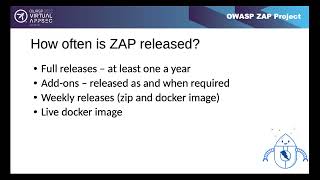
OWASP ZAP Project: Introduction to Web Application Security Testing
Learn to use OWASP ZAP, a powerful open-source web application security scanner. Discover its features, capabilities, and best practices for identifying vulnerabilities in web applications.
What's New in CRS4 - An Update from the OWASP CRS Project
Explore the latest updates and enhancements in CRS4, the OWASP Core Rule Set project, with insights on improved web application security and threat mitigation strategies.
15 Years of OWASP Top 10 - Has the Cloud Made a Difference?
Explore the evolution of web application security over 15 years, examining the impact of cloud computing on OWASP Top 10 vulnerabilities and current cybersecurity challenges.
Exploiting Web Messaging Implementations
Uncover vulnerabilities in cross-document messaging, learn common developer mistakes, and explore open-source tools for identifying post messaging security issues in web applications.