Benchmarking the Security of Your Software Supply Chain
Learn to assess and enhance the security of your software supply chain through benchmarking techniques, improving overall cybersecurity posture and reducing vulnerabilities.
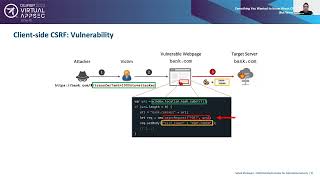
Everything You Wanted to Know About Client-Side CSRF But Were Afraid to Ask
Explore client-side CSRF vulnerabilities, detection challenges, and advanced analysis techniques using hybrid property graphs for improved web application security.
Shifting Security Everywhere
Explore strategies for integrating security throughout the software development lifecycle, emphasizing proactive measures and collaboration between development and security teams.
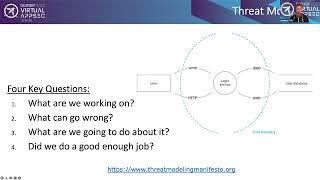
Shift Left Security with the Security Test Pyramid
Explore the concept of shifting security testing left in the development process using the Security Test Pyramid, enhancing software security from the early stages.
OWASP Application Security Verification Standard (ASVS) Project Overview
Explore the OWASP Application Security Verification Standard (ASVS) project, its importance in secure software development, and practical implementation strategies.
Telecom User Group and Cloud Native Network Functions Testbed - Introduction and Deep Dive
Explore the evolution of telecom network functions to cloud-native, discussing challenges, architecture, and performance testing in Kubernetes environments.
The Bug Hunter's Methodology 2.0 - Advanced Web Application Security Testing
Explore cutting-edge techniques and tools for discovering vulnerabilities in web applications, including XSS, SSTI, SSRF, code injection, and more. Learn from expert Jason Haddix's updated methodology for effective penetration testing.
Taking AppSec to 11: Pipelines, DevOps and Making Things Better
Scaling AppSec through DevOps: Learn strategies to enhance application security programs using pipelines, automation, and iterative improvements for large-scale organizations.
New Methods in Automated XSS Detection - Dynamic Testing Without Static Payloads
Explore innovative dynamic methods for automated XSS detection without static payloads, including techniques for Stored XSS and custom exploit generation. Learn to overcome limitations of traditional approaches.
Automating API Penetration Testing Using Fuzzapi
Explore automated API penetration testing with fuzzapi, addressing common vulnerabilities in REST APIs. Learn to integrate security testing into development pipelines for early detection and mitigation.
Attack Patterns for Black-Box Security Testing - AppSecEU 2016
Explore attack patterns for black-box security testing in web applications, focusing on methodologies and strategies to identify vulnerabilities effectively.
Bugs Ruin Everything - Keynote on Vulnerability Analysis and Exploitation
Explore vulnerability analysis techniques, their strengths and weaknesses, and real-world case studies with security expert Charlie Miller in this engaging keynote from AppSecEU 2016.
Bringing Security Testing to Development: Enabling Developers as Security Experts
Discover strategies for integrating security testing into development processes, empowering developers to become security experts and enhance application safety.
The API Assessment Primer
Learn essential API security assessment techniques, including key considerations, testing steps, and best practices for protecting APIs and mobile applications from common vulnerabilities and threats.
Running a Bug Bounty Program - What You Need to Know
Discover essential insights for running successful bug bounty programs, including strategies, resources, and best practices for effective vulnerability management and rewards.
Scanning with Swagger - Using the Open API Specification to Find Vulnerabilities
Explore leveraging Open API specification for enhanced security scanning, uncovering vulnerabilities and improving application protection strategies.
Skillful, Scalable Full-Stack Security in a State of Constant Flux
Approaches to maintaining secure full-stack posture at scale in changing environments. Discusses automation vs. human testing, analytics in continuous security, and scaling with human validation and intelligence.
Serverless Security for DevOps and Defenders
Explore serverless architecture's impact on DevOps and security with James Wickett. Learn how this emerging technology enhances defense strategies and streamlines development processes.
Building a Better Hacker to Improve Cybersecurity Defense
Explore how understanding hacker mentality bridges the gap between developers and security teams, leading to more effective cybersecurity strategies and proactive threat prevention.
Why Your AppSec Experts Are Killing You - Evolving to Continuous Application Security
Explore how to evolve into a "Continuous Application Security" organization using instrumentation-based testing, real-time feedback loops, and innovative tools for improved DevOps integration and portfolio-wide assurance.
Security Testing Windows Store Apps
Explore security testing for Windows Store Apps, focusing on HTML/JavaScript development, architecture, and potential vulnerabilities in this emerging application model.