Security Instrumentation - The Future of Software Security
Explore security instrumentation as a revolutionary approach to enhance software security, offering dynamic capabilities like intrusion detection, SBOM reporting, and runtime protection without code changes.
Dynamic Binary Instrumentation Techniques to Address Native Code Obfuscation
Explore dynamic binary instrumentation techniques for tackling obfuscated Android app code, aiding reverse engineers in overcoming anti-analysis protections.
Pwning Intel PIN
Exploring vulnerabilities in Intel PIN's dynamic binary instrumentation framework, challenging assumptions of isolation and stealthiness, and demonstrating potential security risks in instrumented programs.
Android Rootkits - Analysis from Userland and Kernelland
Explore Android rootkit analysis using memory forensics, dynamic binary instrumentation, and machine learning for actionable threat intelligence in userland and kernelland.
Finding 0days in Embedded Systems with Code Coverage Guided Fuzzing
Innovative fuzzing technique for embedded systems, overcoming challenges to discover critical vulnerabilities in network devices through emulation, dynamic binary instrumentation, and guided fuzzing.
Practical Uses of Program Analysis - Automatic Exploit Generation
Explore automatic exploit generation through program analysis techniques, including instrumentation and symbolic execution, with practical demonstrations and tool insights.
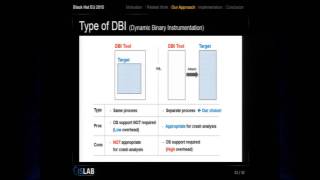
Triaging Crashed with Backward Taint Analysis for ARM Architecture
Explore tools for analyzing crashes on Linux and ARM, using dynamic binary instrumentation and backward taint analysis to determine exploitability. Learn about ARM-Tracer and ARM-Analyzer for efficient crash analysis.
Break Out of The Truman Show - Active Detection and Escape of Dynamic Binary Instrumentation
Explore active detection techniques for Dynamic Binary Instrumentation, focusing on exploiting weaknesses and escaping control. Learn to identify and overcome DBI environments in cybersecurity.
Pindemonium - A DBI-Based Generic Unpacker for Windows Executable
Explore a generic unpacking algorithm for Windows executables using Dynamic Binary Instrumentation. Learn to detect and defeat popular packing techniques, reconstruct working PEs, and handle IAT obfuscation.
Defeating the Transparency Feature of DBI
Techniques to break transparency in dynamic binary instrumentation tools, exposing limitations and enabling detection of analysis environments for malware and binary applications.
Reverse Engineering All the Malware and Why You Should Stop
Explore efficient malware analysis techniques, automation tools, and dynamic instrumentation methods to enhance reverse engineering skills and streamline the process.
Taking Testing to the Next Level
Dynamic binary instrumentation for advanced testing: Explore Frida toolkit to enhance code testing, retrofit interfaces, and solve production issues through innovative techniques and demonstrations.