Detecting CSRF Vulnerability Reliably - Programmatic Approach
Explore a programmatic approach to reliably detect CSRF vulnerabilities in web applications, overcoming common shortcomings of existing tools and improving automated security testing.
Creating Accessible Security Testing with ZAP - AppSecCali 2019 Lightning Talk
Introducing OWASP ZAP's Heads Up Display: A new UI that makes security testing more intuitive for developers and professionals, enabling efficient use of the attack proxy tool.
Open-Source OWASP Tools for Enhancing Penetration Testing Coverage
Explore open-source OWASP tools for efficient white box penetration testing. Learn about Code Pulse for real-time code coverage and Attack Surface Detector for comprehensive endpoint discovery to enhance security assessments.
A Seat at the Table: Effective Security Collaboration in DevOps - AppSecCali 2019
Discover effective collaboration strategies for security professionals in the DevOps era, focusing on new skills, approaches, and speed to engage early and add value in software development.
Monitoring Attack Surface and Integrating Security into DevOps Pipelines
Explore methods for calculating and tracking web application attack surface, and learn to integrate security testing into CI/CD pipelines for effective DevOps practices.
Security and the Self-Contained Unit of Software - AppSec EU 2017
Exploring security challenges in modern software development, focusing on self-contained components and shifting security features from infrastructure to application level.
SDLC for the DevSecOps Era - Adapting Application Security Techniques
Practical lessons on adapting application security techniques for agile development, covering lightweight controls, visibility, and measuring security maturity in modern DevOps environments.
Embedding GDPR Into the Secure Development Lifecycle
Practical guide to integrating GDPR requirements into software development lifecycle, covering privacy awareness, risk analysis, secure coding, and breach notification processes.
AppSec Pipelines and Event-based Security - Moving Beyond Traditional Security Testing
Explore event-based security and AppSec pipelines to enhance traditional security testing methods. Learn innovative approaches for improving application security from an experienced professional.
DASTProxy: Automated Security Testing Focused on Business Context
Explore DASTProxy: a tool for automated security testing that focuses on business context rather than crawling, enhancing efficiency and effectiveness in application security assessments.
InfoSec at Peak Prevention
Explore InfoSec at Peak Prevention with Daniel Miessler, an experienced security tester and consultant. Learn about cutting-edge strategies in application security and IoT security from an industry expert.
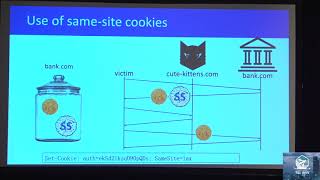
Bypassing Browser Policies and Privacy Extensions for Cookies
Explore bypasses to browser policies and extensions for cookie security. Learn about an automated framework for evaluating countermeasures against cross-site attacks and third-party tracking.
How to Break APIs - Security Testing Techniques
Comprehensive guide to identifying and exploiting vulnerabilities in APIs, focusing on practical techniques for security testing and penetration.
Do Certain Types of Developers or Teams Write More Secure Code?
Explore factors influencing secure code development, including team dynamics, developer experience, and human factors. Gain insights into improving software security practices.
Scaling Security in Leading Companies - DevOps and CI/CD Best Practices
Discover pro-tips and actionable lessons from mature security teams on scaling security in modern software development. Learn effective strategies for buy-in, engineering projects, analysis integration, and production monitoring.
Software Security 5D Framework - Evolution of Security Verification
Explore the OWASP Software Security 5D Framework and its impact on integrating security bugs into the software lifecycle, revolutionizing traditional assessment methods.
Threat Modeling the CI/CD Pipeline to Improve Software Supply Chain Security
Explore threat modeling for CI/CD pipelines to enhance software supply chain security, covering key vulnerabilities, data flow analysis, and mitigation strategies.
Security Chaos Engineering - Turning the Tide in the War on Uncertainty in Cyber Security
Explore security chaos engineering to proactively discover system weaknesses, increase confidence in security mechanisms, and move from subjective assessment to objective measurement through continuous experimentation.
Topics of Interest: Developers Struggle with Application Security and How to Make It Better
Explore challenges in application security for developers and learn strategies to improve DevSecOps practices, drawing from real-world experiences at major tech companies.
Securing the Build and Deployment Pipeline - Challenges and Best Practices
Explore challenges in securing build/deployment environments for agile development and DevOps. Learn about potential vulnerabilities in automated processes and strategies to maintain code integrity.
Automated Security Testing With OWASP Nettacker
Learn automated security testing techniques using OWASP Nettacker, a powerful open-source tool for vulnerability assessment and information gathering in web applications and networks.