Getting a Handle on Mobile Security
Comprehensive overview of mobile security challenges and best practices, covering encryption, data protection, and platform-specific concerns for developers building secure mobile applications.
OWASP Reverse Engineering and Code Modification Prevention Project
Explore reverse engineering risks and prevention techniques for application security experts. Learn about code integrity, data validation, and architectural principles to protect software in untrusted environments.
Building Secure Containers for Mobile Devices
Explore secure container solutions for BYOD environments, covering application wrapping, design challenges, iOS runtime analysis, and implementation best practices for mobile data protection.
Verifying Software for Security Bugs - Dynamic Analysis and Fuzzing Testing
Learn dynamic analysis and fuzzing techniques to verify software security, including mitigations and vulnerability checks. Explore BinSecSweeper, an open-source tool for binary analysis on Windows and Linux.
Dynamic Source-Sink Analysis for Java Applications - From the Ground Up
Dynamic source-sink analysis for Java applications to detect security vulnerabilities, aimed at developers for use during development, not production. Demonstrates live detection of issues like log manipulation.
AppSecUSA 2014 - Breakers Track Sessions
Explore cutting-edge web and mobile security topics, including mobile attacks, use-after-free exploitation, static analysis, runtime manipulation, and top hacking techniques from AppSecUSA 2014.
Continuous Security Testing in DevOps Environments
Explore continuous security testing in DevOps, addressing challenges and presenting an open-source framework using Behavior Driven Development for effective communication and automation.
Fix the Damned Software - Improving Application Security Design
Explore strategies for building security into software development, moving beyond vulnerability discovery to secure design and implementation. Learn from industry experience and BSIMM data.
Static Analysis for Dynamic Assessments - OWASP AppSecUSA 2014
Explore techniques for using static analysis tools in dynamic web vulnerability assessments without source code, enhancing detection of security weaknesses in complex applications.
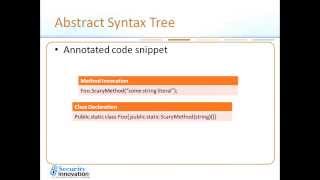
Adventures in Reviewing Mountains of Code
Explore strategies for efficiently reviewing large codebases, including experiments, tools, and unexpected challenges encountered during a 2.6 million line code assessment.
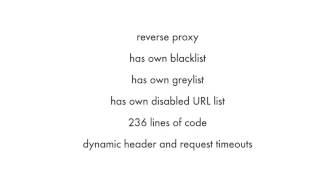
Surviving an Application DoS - Strategies and Open Source Defense Framework
Explore strategies to defend against Application-Level DoS attacks using a new open-source Node.js framework. Learn to identify threats, analyze traffic patterns, and implement active defense measures.
NIST Missions and Impacts on US Industry, Economy, and Citizens - Lecture
Explore NIST's mission, impact on US industry, and cybersecurity initiatives. Learn about current programs, projects, and R&D activities in this premier scientific institution.
Can I Build an Embedded Linux System with Clang - Lecture
Explore building embedded Linux systems using Clang, covering tools, dependencies, configurations, and challenges in this comprehensive technical overview.
Rust-VMM: A Security Journey
Explore rust-vmm's security journey, covering components, audits, development practices, and fuzzing techniques for virtualization and Virtio components.
Building Secure Terabit Network Services with FD.io Technologies
Explore FD.io's role in building secure Terabit NaaS cloud networking, focusing on VPP and CSIT projects for high-performance, scalable, and robust cloud VPNs with encrypted overlays.
Shift-Left DevOps for APIs with Okta and JFrog - Developer Day 2021
Strengthen your shift-left DevSecOps strategy by automating REST API security validation using Okta and JFrog. Learn to verify authentication and authorization policies before production release.
Making Fuzzing Part of Your Software Development Lifecycle
Learn to integrate fuzzing into software development, exploring tools like libFuzzer, ClusterFuzz, and OSS-Fuzz to enhance security and catch bugs early in open-source and proprietary projects.
Automated Testing and Board Farming for Embedded Linux
Explore practical aspects of running board farms for embedded Linux testing. Discuss control software, architectures, hardware tools, and collaboration opportunities in automated testing.
Shifting Application Security Left: Practical Steps to Get There
Explore practical steps to integrate automated security testing into software delivery pipelines, enabling efficient and secure development practices for modern engineering teams.
Automated Testing for Embedded Development - Next Generation Board Farming
Explore next-generation board farming techniques for automated testing in embedded development, enhancing efficiency and reliability in hardware-software integration.
Board Farm APIs for Automated Testing of Embedded Linux - An Update
Explore APIs for automated testing of embedded Linux, covering framework-lab interactions, resource models, and practical implementations for power measurement, camera, and serial operations.