Using the Snyk CLI for Static Code Analysis
Learn to use Snyk CLI for static code analysis in CI/CD pipelines. Covers installation, testing, result filtering, and practical scenarios for integrating security scans into your development workflow.
Rust: Why I Hate Garbage Collectors - Meetup 2016
Explore why garbage collectors can be problematic in programming, focusing on resource management, ownership, and static analysis. Learn about alternatives and Rust's approach.
Short Text, Large Effect - Measuring the Impact of User Reviews on Android App Security & Privacy
Exploring the impact of user reviews on Android app security and privacy, analyzing 4.5M reviews to identify concerns and measure developers' responses through code changes.
Talos - Neutralizing Vulnerabilities with Security Workarounds for Rapid Response
Neutralizing vulnerabilities using error-handling code for rapid response, minimizing patch delays while maintaining functionality. Explores automated security workarounds to mitigate risks in popular Linux server applications.
Hacker-Powered Security in Agile Software Development - Webinar
Explore hacker-powered security in agile software development, covering open source risks, bug bounty benefits, and integrating security into continuous delivery workflows.
What's in My Hacking Tool Box? by Richard Rushing
Explore a seasoned hacker's toolkit and methodology for penetration testing, covering various domains including malware analysis, mobile app exploitation, and API security.
Open-Source OWASP Tools for Enhanced Penetration Testing Coverage - 2018
Explore open-source OWASP tools for efficient white box testing. Learn about Code Pulse for real-time code coverage and Attack Surface Detector for comprehensive endpoint discovery, enhancing penetration testing effectiveness.
Open-Source OWASP Tools for Enhancing Penetration Testing Coverage
Explore open-source OWASP tools for efficient white box penetration testing. Learn about Code Pulse for real-time code coverage and Attack Surface Detector for comprehensive endpoint discovery to enhance security assessments.
Getting a Handle on Mobile Security
Comprehensive overview of mobile security challenges and best practices, covering encryption, data protection, and platform-specific concerns for developers building secure mobile applications.
OWASP Reverse Engineering and Code Modification Prevention Project
Explore reverse engineering risks and prevention techniques for application security experts. Learn about code integrity, data validation, and architectural principles to protect software in untrusted environments.
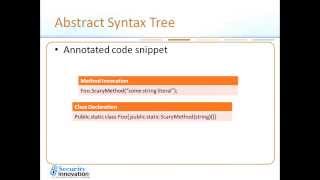
Adventures in Reviewing Mountains of Code
Explore strategies for efficiently reviewing large codebases, including experiments, tools, and unexpected challenges encountered during a 2.6 million line code assessment.
Security as Code - A DevSecOps Approach
Explore DevSecOps and Security as Code with CodeQL. Learn to implement security checks, detect vulnerabilities, and foster collaboration between development and security teams for a robust security culture.
NVMe: New Vulnerabilities Made Easy - Exploiting Cloud Storage Protocols
Exploring pre-auth remote vulnerabilities in NVMe implementation, emphasizing the importance of SCA tools in production pipelines and showcasing discoveries in Linux kernel and NVIDIA.
5 Open Source Security Tools All Developers Should Know About
Discover five essential open-source security tools for CI/CD pipelines. Learn to integrate SAST, secrets detection, SCA, IaC security, and DAST with practical code examples and demos.
Incident Response for Developers
Learn essential incident response strategies for developers, focusing on security incidents, your role during crises, and effective communication with AppSec teams.
Cracking the Code Review - From Guesswork to Automated Guidance
Discover effective code review strategies, communication techniques, and automated tools to streamline the review process, enhance code quality, and foster better team collaboration.

Java's Hidden Gems - Essential Tools and Libraries for Development
Discover lesser-known Java tools and libraries to enhance security, builds, architecture, and testing capabilities in this comprehensive overview of valuable development resources.
Choosing the Right Static Code Analyzers Based on Hard Data
Explore unbiased methods to assess static code analyzers' performance, learn about a new website presenting research results, and discover how to choose the right tools for your development pipeline.
Microservices Security Landscape - 2018
Comprehensive overview of microservices security, covering SDLC, DevOps, and application-level aspects. Addresses attack surface expansion, continuous delivery, deployment patterns, and inter-service communication security.
Improving Dynamic Vulnerability Scanners with Static Code Analysis
Combining static code analysis and dynamic scanning to enhance vulnerability detection in web applications, improving security by identifying hidden endpoints and reducing false positives.

Python Typing - Type Hints & Annotations
Learn Python type hints and annotations for clearer, more maintainable code. Covers various types, static analysis, and advanced concepts like generics to enhance your programming skills.