ChatGPT for Cybersecurity
Explore ChatGPT's applications in cybersecurity, from pentesting and shell generation to blue team strategies. Learn to leverage AI for enhanced security practices and automation.

Ethical Hacking in 15 Hours - 2023 Edition - Learn to Hack
Comprehensive ethical hacking training covering advanced techniques like subdomain hunting, vulnerability scanning, exploitation, and buffer overflows. Includes hands-on practice with multiple virtual machines.
Introduction to Burp Suite
Comprehensive guide to Burp Suite setup, methodology, and advanced features for effective white hat hacking and bug bounty hunting. Learn proxies, scanners, fuzzing, and targeting techniques.
Buffer Overflows Made Easy - 2022 Edition
Learn to exploit buffer overflows with hands-on techniques including spiking, fuzzing, finding offsets, and generating shellcode. Gain practical skills for ethical hacking and cybersecurity.
Burp Suite
Comprehensive introduction to Burp Suite for web application security testing, covering key features like proxy, repeater, and intruder. Includes hands-on demos for SQL injection and fuzzing.
Buffer Overflows Made Easy
Learn to exploit 32-bit Windows buffer overflows through step-by-step guidance, from introduction to gaining shells, with practical techniques for cybersecurity enthusiasts.
Eko2020 Workshops - Antonio Morales Maldonado: Advanced Fuzzing Workshop
Taller práctico de técnicas avanzadas de fuzzing y búsqueda de vulnerabilidades con formato CTF. Orientado a profesionales con conocimientos previos para mejorar habilidades en seguridad informática.
Security Threat Model Analysis and Protection Practice in Edge Computing Scenarios
Analyze security threats in edge computing, explore KubeEdge's audit process, and learn protection practices for cloud-native environments. Gain insights on improving security in multi-cloud and hybrid scenarios.
SocketCAN: The CAN Subsystem in the Linux Network Stack
Entdecke SocketCAN im Linux-Kernel: CAN-Bus-Grundlagen, Hardware-Unterstützung und Protokolle für Automotive und Industrieanwendungen. Lerne Tools zur Analyse und Manipulation von CAN-Datenverkehr kennen.
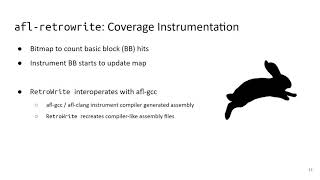
RetroWrite- Statically Instrumenting COTS Binaries for Fuzzing and Sanitization
Explore static instrumentation of COTS binaries for enhanced fuzzing and sanitization using RetroWrite, a framework for rewriting position-independent code.
iPhone Baseband Research and Reversing - Security Insights and Techniques
Explore iPhone baseband internals, research techniques, and tools for firmware analysis, reversing, and exploitation. Gain insights into Qualcomm baseband architecture and vulnerabilities.
API Security 101 by Sadako
Explore API security fundamentals, common vulnerabilities, and real-world examples. Learn testing methodologies, fuzzing techniques, and gain insights from notable bug discoveries in this beginner-friendly introduction.
Fuzzing XSS Sanitizers for Fun and Profit - Tom Anthony
Explore XSS sanitizer fuzzing techniques with Tom Anthony, from his hacking past to current cybersecurity insights. Learn about innovative approaches to discovering vulnerabilities in web applications.
Till REcollapse - Fuzzing the Web for Mysterious Bugs
Explore web fuzzing techniques for uncovering mysterious bugs with André Baptista. Learn strategies to identify impactful vulnerabilities and enhance your ethical hacking skills.
Advent of Cyber - Fuzzing with Burp Suite
Learn fuzzing techniques using Burp Suite in TryHackMe's Advent of Cyber challenge. Enhance your web application security testing skills and discover potential vulnerabilities through automated input manipulation.
Hacking APIs - Fuzzing 101
Learn API fuzzing techniques for penetration testing and security assessment, with hands-on lab demonstrating practical application and methodology.
Automating App Security Tests in Development with Docker
Learn to automate application security testing using Docker. Explore tools like ZAProxy, nikto, and SQLmap for continuous attack simulation in the software development lifecycle, with live demonstrations.
Hacking and Defending APIs - Red and Blue Make Purple
Comprehensive guide to API security: attack techniques, defense strategies, and best practices for both testers and defenders. Covers BOLA, authentication, data exposure, and more.
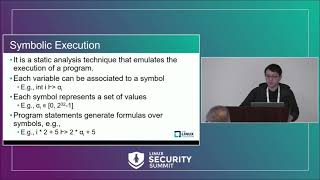
Triaging Kernel Out-of-Bounds Write Vulnerabilities
Explore techniques for triaging kernel out-of-bounds write vulnerabilities, including symbolic execution, capability summarization, and exploitability evaluation.
Pentesting Voice Biometrics Solutions - AppSec EU 2017
Explore pentesting techniques for voice biometrics, including tools for IVR automation, voice fuzzing, and bypassing algorithms. Learn security requirements and compare with traditional password methods.
Securing C Code That Seems to Work Fine
Explore strategies for securing C codebases in high-performance environments, balancing best practices with startup culture. Learn from real-world successes and failures in implementing application security controls.