Accelerating Innovation in Telecommunications - Keynote
Explore telco industry challenges, innovative solutions, and collaborative strategies to accelerate innovation in response to exponential internet traffic growth and evolving technological paradigms.
Trusted Firmware M: Secure Partitioning and Compartmentalization in IoT
Explore IoT device security through TrustZone and compartmentalization. Learn about isolation, interaction between components, and handling challenges in secure systems for robust IoT development.
Leaky Processors - Stealing Your Secrets With Foreshadow
Explore the Foreshadow vulnerability in modern processors and its implications for data security. Learn about potential exploits and mitigation strategies.
Realtime Systems, RISC-V Vector Processing, Open Source in Europe, and Software Transparency - Keynotes Day 3
Explore cutting-edge topics in open source technology with expert keynotes on realtime systems, RISC-V processors, strategic challenges, and software transparency.
TEEP Implementation on RISC-V Keystone and Arm TrustZone
Explore TEEP implementation on RISC-V Keystone and Arm TrustZone, covering use cases, prototypes, and CBOR expressions for secure execution environments.
TEEP Implementation on RISC-V Keystone and Arm TrustZone
Explore TEEP implementation on RISC-V Keystone and Arm TrustZone, focusing on secure provisioning techniques for trusted execution environments in embedded systems.
Implementing UEFI-based Secure Boot and OTA Updates for Embedded ARM Devices
Explore secure boot implementation and OTA updates for embedded ARM devices using UEFI, covering challenges, solutions, and practical integration techniques for robust system security.
Supporting TEE on x86 Client Platforms with pKVM
Explore x86 pKVM implementation for isolated TEE VMs, covering design, requirements, and integration with host OS. Learn about architecture, performance, and future developments.
Hardware Protections Against ROP Attacks
Explore hardware-based defenses against Return-Oriented Programming (ROP) attacks with IBM expert Mike Rapoport, focusing on cutting-edge security measures for system protection.
Recent Advances in U-Boot
Explore major U-Boot developments including Kconfig migration, UEFI support, and binman. Learn about minor enhancements in areas like IPv6, RISC-V, and device tree schema, concluding with a demonstration.
Meltdown and Spectre - Professor Mark Handley, UCL
Comprehensive explanation of Meltdown and Spectre vulnerabilities in modern CPUs, their impact on computer systems, and mitigation strategies. Explores CPU architecture, speculative execution, and side-channel attacks.
Emulation, PowerPC, and Personal Transition in Reverse Engineering - Breaking Ground
Explore baremetal emulation for PowerPC, its applications in reverse engineering, and the personal journey of creating a new framework while embracing self-discovery and transformation.
Booting Successfully for the First Time with Mainline Linux
Learn techniques for efficiently enabling new hardware to run Linux, from schematic review to successful upstreaming of bootloader and kernel patches, with real-world examples.
AMD x86 Memory Encryption Technologies - Secure Memory Encryption and Virtualization
Explore AMD's x86 memory encryption technologies: Secure Memory Encryption for physical access protection and Secure Encrypted Virtualization for isolated encrypted virtual machines. Learn about architecture, security benefits, and Linux implementation.
wolfBoot - Open Source Secure Boot and Remote Firmware Updates in Safety-critical Embedded Systems
Explore wolfBoot, an open-source secure bootloader for embedded systems. Learn about its portability, attack mitigation, and suitability for safety-critical applications across various architectures.
Finding the Best Block Filesystem for Your Embedded Linux System
Comparison of Linux block filesystems for embedded systems, covering design principles, features, performance metrics, and compression options on ARM boards with SD card storage.
DVFS Frequently Leaks Secrets - Hertzbleed Attacks Beyond SIKE, Cryptography, and CPU-Only Data
Explore Hertzbleed attacks beyond SIKE, revealing how DVFS can leak secrets in various scenarios, impacting cryptography and data security across CPU architectures.
CustomProcessingUnit: Reverse Engineering and Customization of Intel Microcode
Explore Intel microcode reverse engineering and customization techniques, uncovering CPU vulnerabilities and enhancing processor functionality.
Side-Channel Attacks on Microarchitecture - CHES 2024
Explore microarchitectural side-channel attacks and defenses in cryptographic systems at CHES 2024, featuring cutting-edge research and expert insights.
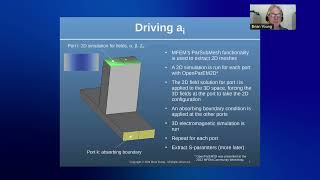
A Full-Wave Electromagnetic Simulator for Frequency-Domain S-Parameter Calculations
Explore an open-source electromagnetic simulator for S-parameter calculations, featuring adaptive mesh refinement, arbitrary order finite elements, and parallel processing using MFEM.
Software Supply Chain Security with Trusted Execution Environment Provisioning Protocol
Explore TEEP protocol for secure software supply chain management, covering its benefits, implementation, and application across various hardware platforms and industries.