Verified Software Security Down to Gates
Explore hardware-software contracts synthesis, security vulnerability detection, and microarchitecture updates for verified software security. Gain insights into cutting-edge approaches for high-assurance computer systems design.
KVM Address Space Isolation
Explore KVM Address Space Isolation: its intuition, applications, lifecycle, usage, and synchronization. Learn about page table filling, switching, and the ASI model for data privilege.
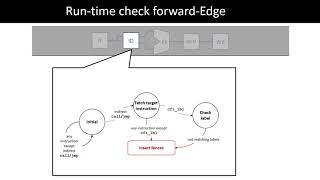
Mitigating Spectre Attacks Using CFI Informed Speculation
Mitigating Spectre attacks using Control-Flow Integrity to constrain speculative execution, combining forward and backward edge protection for comprehensive defense against non-vendor-specific vulnerabilities.
Meltdown and Spectre - Professor Mark Handley, UCL
Comprehensive explanation of Meltdown and Spectre vulnerabilities in modern CPUs, their impact on computer systems, and mitigation strategies. Explores CPU architecture, speculative execution, and side-channel attacks.
Side-Channel Attacks on Microarchitecture - CHES 2024
Explore microarchitectural side-channel attacks and defenses in cryptographic systems at CHES 2024, featuring cutting-edge research and expert insights.
Say Hello to Your New Cache Flow
Explore innovative cache flow techniques in IT security with experts Geoffrey Bertoli, Rémi Jullian, and Théo Gordyjan at TROOPERS24 conference in Heidelberg, Germany.
From Phantom to Inception: Leaking Data Using Branch-Free Predictor Training
Explore data leakage techniques using branch-free predictor training, from phantom to inception, in modern processors.
Reducing Client Latency and Timeouts When Running Cassandra on Public Cloud
Explore strategies to minimize latency and timeouts in Cassandra deployments on public clouds. Learn to detect incidents, implement automation, and optimize client configurations for improved performance and reliability.
Speculative Execution Vulnerabilities: From Spectre to Control Flow Hijack
Comprehensive exploration of speculative execution attacks, from original Spectre to new vulnerabilities. Clear explanations of exploitation challenges and processor vulnerabilities, with insights on high-resolution timers as potential weapons.
Ret2spec- Speculative Execution Using Return Stack Buffers
Explore speculative execution security risks, focusing on return stack buffer vulnerabilities and potential countermeasures in modern CPUs.
Spectre Attacks Exploiting Speculative Execution
Explore speculative execution vulnerabilities in modern processors, their impact on system security, and potential countermeasures to protect against Spectre attacks.
High-Assurance Cryptography in the Spectre Era
Explore cutting-edge cryptography techniques addressing Spectre vulnerabilities, focusing on constant-time implementations and speculative execution semantics for enhanced security.
Using Hardware Protected Keys with the Linux Crypto API
Learn to use hardware-protected keys with Linux Crypto API for enhanced security in embedded systems. Explore implementation, benefits, and potential challenges in this in-depth presentation.
Empower Programmable Pipeline for Advanced Stateful Packet Processing
Innovative architecture enhancing programmable pipelines for advanced stateful packet processing, enabling flexible dataplane functions through augmented hardware and speculative execution techniques.
Lifting Compiler Security Properties to Stronger Attackers: The Speculation Case
Explore compiler security properties against speculative execution attacks, focusing on lifting guarantees to stronger attacker models and developing a formal framework for well-formedness conditions.
Exec ASLR - Abusing Intel Branch Predictors to Bypass ASLR
Explore a new Spectre v2 technique to bypass ASLR on Intel CPUs by abusing branch predictors, with demos on x86 internals, side-channel attacks, and speculative execution.
MDS, Fallout, Zombieland & Linux
Explore CPU hardware vulnerabilities, their impact on system security, and Linux kernel mitigations with insights from a leading developer.
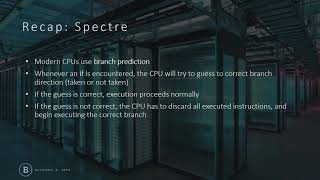
Bypassing KPTI Using the Speculative Behavior of the SWAPGS Instruction
Unveiling a new speculative execution attack exploiting SWAPGS instruction, bypassing existing CPU and kernel protections. Explores side-channel vulnerabilities and their implications for system security.
Mill vs. Spectre - Performance and Security
Explore CPU architecture vulnerabilities, focusing on Meltdown and Spectre attacks. Learn about the Mill architecture's unique approach to performance and security without hardware speculation.
Uncommon Sense - Detecting Exploits with Novel Hardware Performance Counters and ML Magic
Explore novel hardware performance counters and machine learning techniques to detect advanced exploits like speculative execution, Rowhammer, and ROP, enhancing cybersecurity defenses against evolving threats.
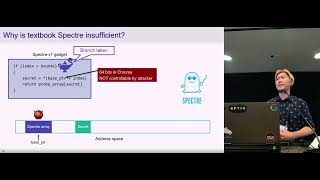
Spook.js - Attacking Chrome Strict Site Isolation via Speculative Execution
Explore a novel attack on Chrome's Strict Site Isolation, leveraging speculative execution to bypass security measures and potentially compromise user data.