Develop TrustZone Enabled Applications on STM32L5 ARM MCUs with STM32CubeIDE - Webinar Replay
Learn to develop and debug TrustZone-enabled applications on STM32L5 MCUs using STM32CubeIDE. Covers project setup, configuration, and practical demonstration with ARM Cortex-M33.
Trusted Firmware M: Secure Partitioning and Compartmentalization in IoT
Explore IoT device security through TrustZone and compartmentalization. Learn about isolation, interaction between components, and handling challenges in secure systems for robust IoT development.
CaSE- Cache-Assisted Secure Execution on ARM Processors
Secure execution framework for ARM processors using TrustZone and Cache-as-RAM to protect sensitive applications against software attacks and cold boot attacks, with minimal performance impact.
Blue Pill for Your Phone
Exploración de vulnerabilidades en hipervisores y TrustZone de teléfonos ARM modernos, analizando vectores de ataque y métodos para elevar privilegios. Incluye lanzamiento de soporte ARM para CHIPSEC.
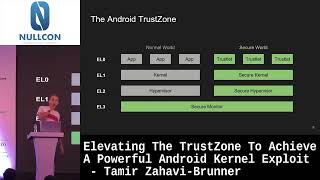
Elevating the TrustZone to Achieve a Powerful Android Kernel Exploit
Explore a novel Android kernel exploitation technique using TrustZone to bypass security mitigations, achieve 100% reliability, and create a versatile exploit applicable across devices and versions.
Reflections on Trusting TrustZone
Explore TrustZone security, vulnerabilities, and exploitation techniques in ARM devices. Gain insights into real-world implications and see a live demonstration of bootloader unlocking.
Next Generation Mobile Rootkits
Explore advanced mobile rootkit techniques using ARM TrustZone, including implementation, hiding methods, and lessons learned from creating an actual rootkit.
Mobile Malware - Why the Traditional AV Paradigm Is Doomed
Explore mobile malware threats, limitations of traditional antivirus methods, and innovative approaches like cloud-based screening and hardware-supported security solutions for protecting mobile devices.
KVM/arm64: The Blob Strikes Back - Episode V
Explore ARM Confidential Computing Architecture's impact on KVM, focusing on challenges posed by the Real Management Monitor as a firmware blob and potential improvements.
Secure Updates for Memory Constrained XIP Systems
Explore secure update methods for memory-constrained XIP systems, addressing challenges and providing real-world examples for IoT devices running Linux directly from flash memory.
A Dark Side of UEFI: Cross-Silicon Exploitation
Explore cross-silicon exploitation in UEFI, uncovering vulnerabilities and advanced attack techniques. Gain insights into Arm perspective, Windows Development Kit, and TrustZone weaknesses.
Secure and Encrypted Boot in Zephyr RTOS Using Hardware Keys and TrustZone
Explore secure booting implementation in Zephyr RTOS using MCUboot, hardware keys, and encryption features like HAB and TF-M for enhanced embedded system security and tamper protection.