
API Information Disclosure - Real-World Bug Hunting
Explore API information disclosure vulnerabilities and learn effective techniques for identifying and exploiting these security weaknesses in web applications.
Hacking and Defending APIs - Red and Blue Make Purple
Comprehensive guide to API security: attack techniques, defense strategies, and best practices for both testers and defenders. Covers BOLA, authentication, data exposure, and more.
Detecting and Controlling Rogue Third-Party Scripts in Web Applications
Explore web supply chain attacks, their impact on sensitive data, and strategies to detect and prevent rogue third-party scripts from compromising web application security.
API Security Through External Attack Surface Management
Integrating APIs into External Attack Surface Management to improve security posture of external-facing APIs. Discusses challenges in asset visibility and strategies for effective protection.
Making End User AppSec Training Engaging with Building Bricks
Innovative approach to AppSec training using LEGO minifigures and custom builds to enhance retention. Covers key security concepts with creative visual metaphors for better engagement and understanding.
JWTs - Patterns and Anti-patterns in Authentication
Explore JWT use cases, patterns, and anti-patterns for secure authentication. Learn best practices and alternatives for implementing stateless tokens in web applications.
SSL Hell: Automated Certificate Management for Microservices
Explore automated certificate management for microservices using cert-manager and ACME protocol. Learn to streamline SSL/TLS deployment in Kubernetes environments.
Core Rule Set for the Masses: Lessons from Taming ModSecurity Rules at Massive Scale - 2017
Insights on fine-tuning ModSecurity Core Rule Set at scale, reducing false positives, and optimizing web application firewall performance for large-scale deployments.
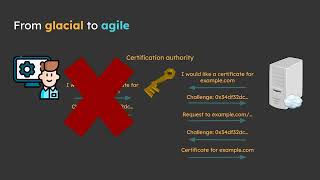
The Dirty Laundry of the Web PKI
Explores web PKI's flaws, revealing the fragile security infrastructure behind HTTPS connections. Discusses issues with certificate authorities and proposes improvements for future server authentication models.
Broken CAPTCHAs and Fractured Equity - Privacy and Security in hCaptcha's Accessibility Workflow
Exploring hCaptcha's accessibility workflow, its privacy implications, and security vulnerabilities. Discusses the future of CAPTCHAs and the challenge of balancing inclusivity with security in online verification systems.
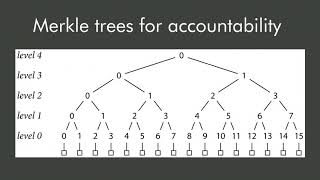
Securing the Software Supply Chain - Go Checksum Database
Exploring Go's checksum database design to secure software supply chains, addressing vulnerabilities in third-party dependencies and enhancing ecosystem integrity.
2019 OWASP Top 10 - Part 1
Comprehensive exploration of the first half of OWASP Top 10, covering critical web application security risks and effective mitigation strategies for developers and security professionals.
OWASP Top 10 Training - Part 3
Comprehensive exploration of OWASP Top 10 security vulnerabilities, focusing on prevention strategies and best practices for web application security.
OWASP Top 10 Training - Part 1
Comprehensive overview of OWASP Top 10 security vulnerabilities, focusing on identification, prevention, and mitigation strategies for web application developers and security professionals.
OWASP Top 10 Security Risks - Part 5
Explore the latest OWASP Top 10 security vulnerabilities, their impact, and effective mitigation strategies to enhance web application security and protect against common threats.
Mind the CSP Gap: Challenges Developing a Meaningful Content-Security-Policy
Strategies for implementing Content Security Policy (CSP) effectively, addressing challenges and phasing in a meaningful policy without disrupting engineering teams.
API Security Best Practices and Guidelines - 2016
Explore industry-leading best practices for designing secure APIs, navigating standards, and protecting both public and private APIs to maximize benefits while keeping threats at bay.
Easy Mobile Hacking: Native and Hybrid Pitfalls - 2016
Uncover common vulnerabilities in mobile apps, both native and hybrid, using free tools. Learn to identify and exploit configuration weaknesses across Android and iOS platforms.
OWASP Top 10 Security Risks for Low-Code/No-Code
Explore security vulnerabilities in low-code/no-code apps, learn about the OWASP Top 10 list, and gain insights from real-world examples to enhance application security in modern development environments.
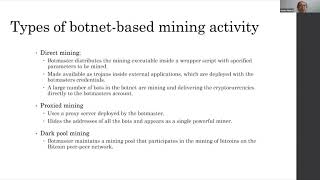
Botnets for Mining Cryptocurrencies - Renita Murimi
Explore botnet threats to cryptocurrency mining, including history, mechanisms, and countermeasures. Learn about consensus protocols, browser evolution, and emerging trends in this cybersecurity challenge.
Towards Usable Checksums- Automating the Integrity Verification of Web Downloads for the Masses
Explore automated integrity verification for web downloads, enhancing user security through improved checksum usability and implementation strategies.