Runtime Analysis of Vulnerabilities and Generation of Exploits
Runtime analysis tool for detecting vulnerabilities and generating exploits. Leverages program execution to identify dataflows, usable for both offensive and defensive purposes. Includes live demonstrations and open-source release.
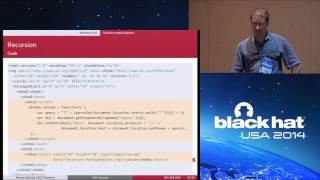
SVG - Exploiting Browsers without Image Parsing Bugs
Explore SVG's hidden potential for web exploitation, including JavaScript execution and external resource imports, challenging traditional browser security assumptions.
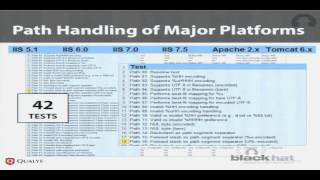
Confessions of a WAF Developer - Protocol-Level Evasion of Web App Firewalls
Explores protocol-level evasion techniques for bypassing web application firewalls, focusing on vulnerabilities in virtual patches and demonstrating real-world examples and countermeasures.

HTExploit - Bypassing Htaccess Restrictions
Explore HTExploit, an open-source Python tool that bypasses htaccess authentication, allowing unauthorized directory listing and exposing web security vulnerabilities.
Next Generation Clickjacking
Explore advanced clickjacking techniques, including data injection and extraction, cross-browser vulnerabilities, and a new tool for creating multi-step attacks on web applications.
The Deputies Are Still Confused
Exploring misunderstandings and vulnerabilities in same-origin policy, with practical examples of attacks bypassing common content-isolation mechanisms for CSRF, clickjacking, and NTLM protection.
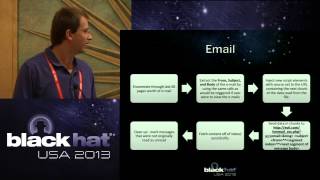
The Web Is Vulnerable - XSS Defense on the BattleFront
Comprehensive analysis of real-world XSS vulnerabilities and attacks, presenting advanced protection methods and introducing detectXSSlib, a new tool for real-time XSS detection.
ModSecurity as Universal Cross-Platform Web Protection Tool
Explore ModSecurity's evolution into a cross-platform WAF, its early attack detection capabilities, and its use of OWASP Core Rule Set for protecting Apache, IIS, and nginx servers.
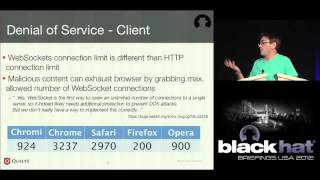
Hacking with WebSockets
Explore WebSocket vulnerabilities, privacy implications, and security risks. Learn to deploy WebSockets securely and use them in hacking frameworks. Gain insights into HTML5 security challenges.
When Security Gets in the Way - Pen Testing Apps That Use Certificate Pinning
Explore tools and techniques for defeating certificate pinning in mobile apps during black-box testing, enabling interception of SSL traffic on both iOS and Android platforms.
Diving Into IE 10’s Enhanced Protected Mode Sandbox
Explore IE 10's Enhanced Protected Mode Sandbox, its security features, and potential vulnerabilities in this in-depth technical analysis.
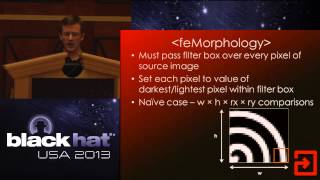
Pixel Perfect Timing Attacks with HTML5
Exploring JavaScript timing attacks to extract sensitive browser data, demonstrating cross-browser vulnerabilities and discussing challenges in fixing these security issues.
New Optimization and Obfuscation Techniques
Advanced SQL injection techniques for bypassing firewalls and intrusion detection systems, including optimization methods and the Leapfrog framework for testing security measures.
Dissecting CSRF Attacks & Countermeasures
Explore CSRF attacks, current countermeasures, and a proposed header-based policy for improved web security. Learn detection techniques and a new concept called Storage Origin Security for simplified protection.
AMF Testing Made Easy
Reshaping AMF fuzzing with automated gray-box testing. Learn to build custom AMF messages, dynamically generate objects, and improve fuzzing coverage for complex applications using the Blazer Burp Suite plugin.
Million Browser Botnet
Explore how online advertising networks can be exploited to create massive browser botnets, enabling DDoS attacks, spam campaigns, and password cracking without malware or zero-day vulnerabilities.
SSL, Gone in 30 Seconds - A BREACH Beyond CRIME
Unveiling new techniques to extract encrypted secrets from HTTPS channels, demonstrating a practical attack against enterprise products and discussing mitigation strategies.
Hard-core Web Defacement Statistics, Trends, and Analysis
Comprehensive analysis of web defacement trends, exploring statistics and patterns in cybersecurity attacks to enhance understanding and prevention strategies.
Defending Windows 2000 on the Internet
Explore strategies for securing Windows 2000 systems on the internet, covering architecture, configurations, and best practices to defend against common attacks and vulnerabilities.
Attacking and Defending DNS
Explore DNS vulnerabilities and defense strategies for Windows 2002, covering attack techniques and protective measures to enhance network security.
Attacking the WebAssembly Compiler of WebKit
Explore vulnerabilities in WebKit's WebAssembly compiler, focusing on recent updates and new features. Learn about potential security risks and attack surfaces in browser implementations.