Fuego Test Framework Status and Roadmap
Explore Fuego Test Framework's status, roadmap, and comparisons with existing open-source testing tech. Learn about recent developments and contribute to shaping its future direction.
How Scripting in ZAP Can Bridge the Gap Between Dev Teams and Security
Learn to bridge dev and security teams using ZAP scripting. Explore opportunities, overcome obstacles, and implement effective testing strategies for enhanced application security.
Testing iOS Apps without Jailbreak - Penetration Testing Techniques
Learn techniques for penetration testing iOS apps without jailbreaking, including live demos on accessing protected resources on the latest iOS version. Ideal for pentesters facing jailbreak limitations.
Turning Engineers into Extended Blue Team Members - Security Strategies
Strategies for empowering engineers to become part of the security team, including threat modeling, incident-driven learning, and security testing integration into development processes.
SUSTO: Systematic Universal Security Testing Orchestration
Explore systematic universal security testing orchestration for efficient vulnerability detection and management in software development lifecycles.
Real World Static Analysis for Real Humans
Explore practical static analysis techniques for software security, focusing on real-world applications and human-centric approaches to code analysis.
OWASP ZAP: Introduction to Web Application Security Testing
Explore OWASP ZAP's latest features, including automation, reporting, and out-of-band testing. Learn how this open-source tool enhances web application security through practical demonstrations and updates.
OWASP Web Security Testing Guide
Comprehensive guide for web security testing, covering methodologies and best practices to identify vulnerabilities and enhance application security.
Attacking Microservice Systems: Methods and Practical Tips
Discover methods and practical tips for attacking microservice systems, exploring new security architecture patterns and vulnerabilities specific to this increasingly popular design approach.
Using Coccinelle to Detect and Fix Nested Execution Context Violations
Explore techniques for detecting and fixing nested execution context violations using Coccinelle, enhancing code quality and reliability in Linux kernel development.
Automatic Detection of Inadequate Authorization Checks in Web Applications
Automatic detection of missing authorization checks in web apps using static analysis. Explores techniques, real-world applications, and provides remediation suggestions for developers.
CopperDroid: Reconstructing Android Malware Behaviors
Explore CopperDroid, an innovative system for analyzing Android malware behaviors through VMI-based dynamic analysis, capturing both OS-specific and Android-specific actions to enhance mobile security.
OWASP ZAP Advanced Features for Web Application Security Testing
Explore advanced features of OWASP ZAP for web application security testing, including handling non-standard apps, client-side testing, fuzzing, scripting, and more with expert Simon Bennetts.
HTTP Time Bandit - Identifying Web Application Performance Bottlenecks
Explore web application vulnerabilities and efficient DOS/DDOS attack techniques using HTTP Time Bandit tool. Learn to identify resource-consuming pages for improved security or targeted attacks.
RailsGoat: Vulnerable Ruby on Rails Framework for Security Education
Explore RailsGoat, a vulnerable Ruby on Rails app designed to educate developers and security professionals on OWASP Top 10 vulnerabilities and additional security issues.
Introduction to OWASP's Zed Attack Proxy - Web Application Penetration Testing
Explore OWASP's free, open-source penetration testing tool for web applications. Learn its features, installation, and usage through hands-on demonstrations and testing of insecure web apps.
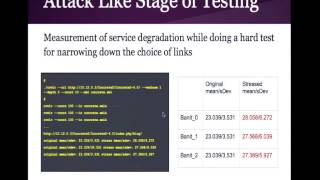
HTTP Time Bandit: Identifying and Exploiting Web Application Performance Bottlenecks
Explore a tool for identifying web application performance bottlenecks and vulnerabilities, enabling efficient DOS/DDOS attacks. Learn about data normalization, testing methods, and attack strategies.
Building Embedded Drivers for Industrial Communication Using Code Generation
Learn to build embedded drivers for industrial communication using code generation techniques, focusing on challenges, MSpec examples, and integration testing.
Dealing with Verification Data Overload in OpenJDK Projects
Explore data visualization and deep learning techniques to efficiently process and analyze massive test logs, enabling quick problem identification and improved monitoring of complex CI/CD pipelines.
Clang as a Viable Static Compiler for Embedded Linux
Explore Clang as a viable static compiler for Embedded Linux, its modern design, sophisticated tools, and integration with Yocto Project. Learn about its advantages and use cases in embedded development.
Extending Mesos for Large Scale Clusters at Uber
Learn how Uber extended Mesos for large-scale cluster management, including reactive integration with service discovery and custom modules for resource oversubscription. Gain insights on monitoring, building, and testing.