Unleashing Mayhem on Binary Code
Explore automated exploit generation for binary programs using hybrid symbolic execution and index-based memory modeling. Learn techniques to find and demonstrate exploitable vulnerabilities efficiently.
Heapster- Analyzing the Security of Dynamic Allocators for Monolithic Firmware Images
Explore Heapster's innovative approach to analyzing dynamic allocators in monolithic firmware, enhancing security through advanced identification and evaluation techniques.
DP-Sniper - Black-Box Discovery of Differential Privacy Violations Using Classifiers
Explore a novel approach to detect differential privacy violations using classifiers, enhancing data protection and privacy in machine learning systems.
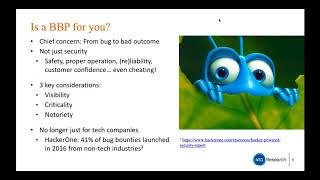
Bug Bounties and the Path to Secure Software Development
Explore bug bounties and vulnerability disclosure policies for secure software development, including implementation strategies, benefits, and best practices.
Hacker-Powered Security in Agile Software Development - Webinar
Explore hacker-powered security in agile software development, covering open source risks, bug bounty benefits, and integrating security into continuous delivery workflows.
Bug Bounty Field Manual - Cliff Notes for Planning and Operating Successful Programs
Comprehensive guide on planning, launching, and operating successful bug bounty programs, covering team formation, scope setting, bounty structures, and program management strategies.
Bug Hunting as a Team: Challenges and Insights - LevelUp 0x04
Insights on collaborative bug hunting: organizing teams, sharing information, splitting bounties, and overcoming challenges in the evolving field of cybersecurity.
iPhone Baseband Research and Reversing - Security Insights and Techniques
Explore iPhone baseband internals, research techniques, and tools for firmware analysis, reversing, and exploitation. Gain insights into Qualcomm baseband architecture and vulnerabilities.
What's in My Hacking Tool Box? by Richard Rushing
Explore a seasoned hacker's toolkit and methodology for penetration testing, covering various domains including malware analysis, mobile app exploitation, and API security.
API Security 101 by Sadako
Explore API security fundamentals, common vulnerabilities, and real-world examples. Learn testing methodologies, fuzzing techniques, and gain insights from notable bug discoveries in this beginner-friendly introduction.
Social Engineering 101 by Matteo Cagnazzo
Discover techniques for gathering company information through OSINT and social engineering. Learn how non-technical methods can complement technical security assessments in bug hunting.
Revitalizing Product Security Through Bug Bounty Programs - Zephyr Health Case Study
Discover how implementing a private bug bounty program transformed Zephyr Health's development culture, motivating teams to prioritize security and leverage crowdsourced expertise.
Critical Vulnerabilities and Bug Bounty Programs
Explore critical vulnerabilities uncovered through bug bounty programs, their impact, and strategies for effective vulnerability management and disclosure in cybersecurity.
Finding Bugs with Burp Plugins and Bug Bounty 101
Learn to create automated testing plugins for Burp and explore bug bounty programs. Gain insights on finding vulnerabilities, tips for success, and valuable resources for cybersecurity enthusiasts.
Fuzzing XSS Sanitizers for Fun and Profit - Tom Anthony
Explore XSS sanitizer fuzzing techniques with Tom Anthony, from his hacking past to current cybersecurity insights. Learn about innovative approaches to discovering vulnerabilities in web applications.
Practical Recon Techniques for Bug Hunters & Pen Testers
Discover effective reconnaissance strategies for identifying vulnerabilities and enhancing security assessments in this informative session led by expert Bharath.
The State of Bug Bounties and Future Trends - Casey Ellis AMA
Insights on bug bounty industry trends, future prospects, and expert Q&A with Bugcrowd's CEO Casey Ellis, covering various aspects of cybersecurity and ethical hacking.
Overcoming Executive Biases in Cybersecurity Investment
Strategies to overcome executive biases and secure more investment in cybersecurity, including new success metrics and industry comparisons.
Demystifying Program Management in Crowdsourced Security
Explore expert program management in crowdsourced security testing, focusing on bug bounties and vulnerability disclosure. Learn key strategies for successful implementation and management.
Till REcollapse - Fuzzing the Web for Mysterious Bugs
Explore web fuzzing techniques for uncovering mysterious bugs with André Baptista. Learn strategies to identify impactful vulnerabilities and enhance your ethical hacking skills.
Advent of Cyber - Fuzzing with Burp Suite
Learn fuzzing techniques using Burp Suite in TryHackMe's Advent of Cyber challenge. Enhance your web application security testing skills and discover potential vulnerabilities through automated input manipulation.