Especificaciones de Tipos Automágicamente - Code BEAM Lite Mexico 2023
Aprende a mejorar código heredado con TypEr, agregando especificaciones de tipos automáticamente. Descubre herramientas y mejoras para facilitar el mantenimiento de software.
Escribiendo Mejores Pruebas en Elixir - Charla en Español
Aprende a escribir pruebas más efectivas en Elixir. Descubre características de buenos tests, escenarios más allá del camino feliz y razones para implementarlos. Mejora la calidad y confiabilidad de tu código.
Exploring Elixir Codebases with Archeometer - Talk in Spanish
Explora y analiza eficientemente grandes bases de código Elixir utilizando Archeometer para obtener metadatos, identificar módulos clave y evaluar la calidad del diseño del sistema.
Dynamic Analysis of Complex Mobile Applications
Aprenda a realizar análisis de seguridad en aplicaciones móviles complejas, superando protecciones criptográficas y encontrando vulnerabilidades mediante herramientas como Frida, Burp Suite y Brida.
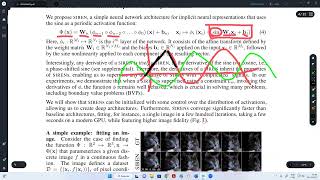
Processamento de Imagens - Laboratório - Aula 07
Aprenda técnicas avançadas de processamento de imagens, incluindo inicialização de redes, camadas intermediárias e soluções para equações de posição.
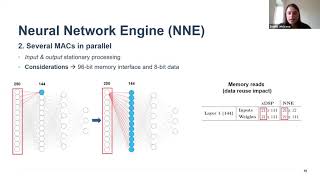
Benchmarking and Improving NN Execution on Digital Signal Processors for Hearing Instruments
Benchmarking and optimizing neural network execution on DSPs for hearing aids, introducing a custom NN processing engine to improve performance and energy efficiency.
Documentation Changes to Help Your Practice - Innovations in ED Management Course
Practical guidance on documentation changes in emergency medicine, focusing on best practices, coding updates, and critical care benchmarking to improve efficiency and compliance.
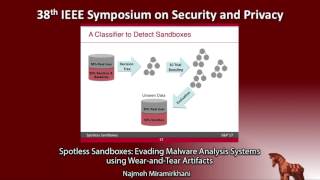
Spotless Sandboxes: Evading Malware Analysis Systems Using Wear-and-Tear Artifacts
Explore techniques for evading malware analysis systems by exploiting wear-and-tear artifacts on real devices, with insights on detection accuracy and potential defensive strategies.
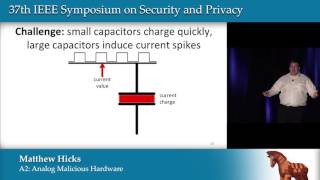
Analog Malicious Hardware
Explore stealthy hardware attacks using analog circuits to bypass security measures. Learn techniques for creating small, undetectable malicious modifications during chip fabrication.
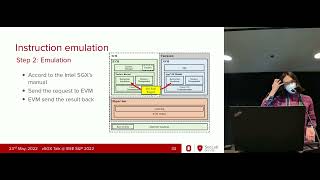
vSGX: Virtualizing SGX Enclaves on AMD SEV
Explore virtualizing Intel SGX enclaves on AMD SEV, addressing vendor lock-in and enabling software-defined trusted execution environments. Learn design goals, challenges, and performance implications.
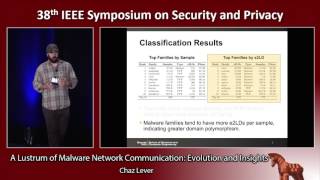
A Lustrum of Malware Network Communication: Evolution and Insights
Explore the evolution of malware network communication over five years, examining trends, insights, and implications for cybersecurity through analysis of 26.8 million samples.
RetroWrite- Statically Instrumenting COTS Binaries for Fuzzing and Sanitization
Explore static instrumentation of COTS binaries for enhanced fuzzing and sanitization using RetroWrite, a framework for rewriting position-independent code.
Short Text, Large Effect - Measuring the Impact of User Reviews on Android App Security & Privacy
Exploring the impact of user reviews on Android app security and privacy, analyzing 4.5M reviews to identify concerns and measure developers' responses through code changes.
CaSym: Cache Aware Symbolic Execution for Side Channel Detection and Mitigation
Explores cache-aware symbolic execution for detecting and mitigating side-channel vulnerabilities, offering novel abstract cache models and guidance for effective countermeasures.
Iodine - Fast Dynamic Taint Tracking Using Rollback Free Optimistic Hybrid Analysis
Explores fast dynamic taint tracking using optimistic hybrid analysis, reducing overhead while maintaining soundness. Introduces Iodine tool for efficient security policy enforcement without rollbacks.
Understanding Linux Malware
Explore Linux malware analysis challenges, infrastructure design, and insights from a large-scale study of 10,548 samples, addressing the growing threat in embedded devices and IoT.
Revealer- Detecting and Exploiting Regular Expression Denial-of-Service Vulnerabilities
Explore techniques for detecting and exploiting ReDoS vulnerabilities, including static analysis, pattern identification, and automated exploit generation.
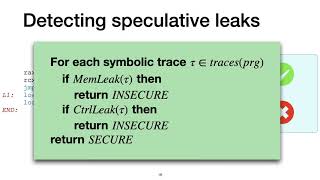
SPECTECTOR - Principled Detection of Speculative Information Flows
Principled detection of speculative information flows in computer systems, focusing on security against Spectre-like attacks through speculative non-interference and symbolic execution techniques.
Talos - Neutralizing Vulnerabilities with Security Workarounds for Rapid Response
Neutralizing vulnerabilities using error-handling code for rapid response, minimizing patch delays while maintaining functionality. Explores automated security workarounds to mitigate risks in popular Linux server applications.
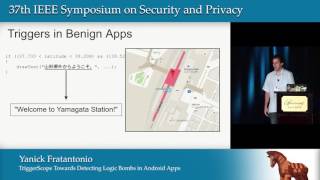
TriggerScope - Towards Detecting Logic Bombs in Android Applications
Explore techniques for detecting logic bombs in Android apps using symbolic execution and path predicate analysis. Learn about TriggerScope, a tool for identifying time-, location-, and SMS-related triggers in mobile applications.
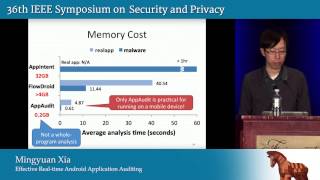
Effective Real-Time Android Application Auditing
Innovative approach combining static and dynamic analysis for efficient, real-time Android app auditing to detect data leaks, offering improved speed and accuracy over existing methods.