Optimizing a Real-Time Audio Processing Library
Optimize real-time audio processing libraries with practical strategies, measurement techniques, and performance-enhancing tricks. Gain tools for confident code optimization across platforms.

DevSecOps: Dynamic Application Security Testing for Identifying Vulnerabilities
Explore security practices in DevSecOps and learn DAST testing to identify vulnerabilities in deployed applications.

Horusec - Security and Vulnerability Integration with CI/CD Pipelines and SonarQube
Explore Horusec integration with CICD pipelines and Sonarqube for enhanced security and vulnerability checks in software development.
A11y Broke My Build - Shifting Accessibility Left in Development
Discover how to integrate accessibility testing into your development pipeline, shifting it left for early error detection and faster feedback loops.
Blasting Past WebP - Exploring Image Format Vulnerabilities
Explore advanced techniques for bypassing WebP image format security measures, uncovering vulnerabilities and potential exploits in web applications.
Removing AWS Policy Review Fatigue with Automated Terraform Resource Analysis
Automate AWS policy control with Terraform resource analysis, reducing security review fatigue and improving developer productivity through early-stage static analysis in IaC pipelines.
7 Must-Know Steps to Making Modern Web Apps Ultra-Secure
Learn 7 essential steps to enhance web app security. Master prevention of vulnerabilities, implement secure authorization, add security layers, logging, and testing for robust protection.
API Security Best Practices - Preventing Vulnerabilities and Hacks
Learn API security best practices, including BOLA vulnerability prevention, testing techniques, and strategies to protect against hacking through a demo-oriented session.
AI for DevSecOps Engineers - Enhancing Security Culture and Education
Explore AI technologies to enhance security testing, analysis, and education for DevSecOps engineers. Learn to automate processes, identify threats, and improve software quality in CI/CD environments.
DevSecOps Unveiled: Integrating Security in the Development Lifecycle
Explore DevSecOps principles and practices for seamlessly integrating security into the development lifecycle. Learn to foster collaboration, automation, and shared responsibility for proactive vulnerability management.
Building Your First DevSecOps Pipeline
Demystify DevSecOps and build a functional pipeline with cutting-edge security testing, including SCA, SAST, and DAST tooling. Supercharge software security and achieve true "Shift Left" success.
5 Open Source Security Tools All Developers Should Know About
Discover five essential open-source security tools for CI/CD pipelines. Learn to integrate SAST, secrets detection, SCA, IaC security, and DAST with practical code examples and demos.
Securing Applications in the Software Development Life Cycle (SDLC) - Beginner
Aprenda prácticas de codificación segura para mitigar riesgos de seguridad y proteger datos en el desarrollo de software moderno.
Defense in Depth: Refocusing on Defensive Security Techniques
Explore defensive product security techniques, emphasizing defense-in-depth and supply chain security. Learn key aspects to consider in your application security strategy.
Automated Testing of Stateful Network Protocol Implementations in the IoT
Explore automated testing techniques for stateful network protocols in IoT, enhancing reliability and efficiency in embedded systems development.
The Peripheral Selftesting Shield - RIOT System
Explore innovative peripheral self-testing techniques for embedded systems in this RIOT Summit presentation on "The Peripheral Selftesting Shield".
Quick Development Cycles with NFS-Root: A Prototype Tool for Embedded Systems - YPDD 2023
Explore efficient embedded system development using NFS-Root booting for quick test cycles and live package updates, enhancing workflow and reducing rebuild times.
Maintenance and Security of a Yocto Project-based Distribution
Explore best practices for maintaining and securing Yocto Project-based distributions. Learn from real-world experiences with CVE checks, SPDX generation, and handling regressions in large-scale projects.
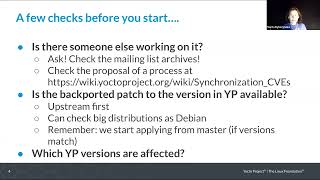
How to Submit a CVE Fix to the Yocto Project - YPS 2023.11
Learn the step-by-step process of submitting security fixes to the Yocto Project, from identifying issues to getting patches accepted.
Exploring a Risk Approach to Software Supply Chain Security
Explore software supply chain security through a risk-based approach, focusing on open source vulnerabilities and process improvements to mitigate supplier risks.
Mastering Data Fabrication: Enhance Testing and Protect User Privacy with Python
Generate realistic, fictitious data for enhanced application testing while adhering to privacy standards. Master tools like Faker to create diverse data types and ensure compliance.