Empowering the Guardians of Your Code Kingdom
Explore strategies for empowering developers to become guardians of code security, enhancing application protection and fostering a security-first mindset in software development.
AI Powered Wordlist - How to Bug Bounty
Learn to create custom wordlists using AI for effective bug bounty hunting. Enhance your cybersecurity skills with this innovative approach to ethical hacking and web application testing.
Bypassing UAC with UACMe - HEK.SI 2022 Conference Presentation
Comprehensive guide to bypassing User Account Control on Windows 10 for privilege escalation, presented at HEK.SI 2022. Covers techniques using UACMe tool to elevate privileges and enhance system access.
Black Belt Bug Hunting - Token Hijacking via PDF File
Learn advanced token hijacking techniques using PDF files in this expert-level web security tutorial, enhancing your penetration testing and bug hunting skills.
Threat Modeling for AI Apps with Attacks as Code
Explore automated threat modeling for AI apps using Secops-Chaos framework. Learn to encode TTPs as security experiments and map MITRE ATLAS TTPs to AI apps in Kubernetes environments.
Inside Apple's Lightning: JTAGging the iPhone for Fuzzing and Profit
Explore Apple's Lightning protocol, learn iPhone JTAGging techniques, and discover fuzzing methods for potential vulnerabilities and profit.
Exploit Engineering: Attacking the Linux Kernel
Explore Linux kernel exploitation techniques, from attack surface mapping to vulnerability discovery and exploit development. Gain insights into advanced kernel exploitation methods and tools.
Changing and Unchanged Things in Vulnerability Research
Explore vulnerability research evolution, from buffer overflows to advanced fuzzing and exploit mitigations. Analyze case studies and future trends in offensive and defensive security strategies.
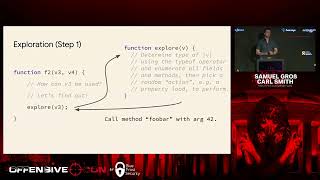
Advancements in JavaScript Engine Fuzzing - OffensiveCon 2023
Explore advancements in JavaScript engine fuzzing, covering techniques like splicing, code coverage, and hybrid engines to enhance bug discovery and security testing.
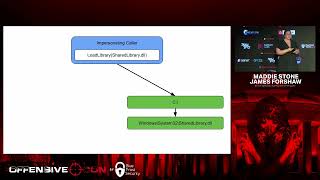
The Print Spooler Bug that Wasn't in the Print Spooler
Explore a unique Windows vulnerability discovery, from initial bug report to full exploit chain, with insights on Microsoft's patch process and security implications.

Securing Web Applications: Integrating OWASP with Burp Suite
Integrate OWASP tools with Burp Suite to identify vulnerabilities, conduct security assessments, and implement effective mitigation strategies for web applications.
OWASP IoT Security Testing Guide (ISTG)
Comprehensive guide for IoT security testing, covering methodologies and best practices to identify vulnerabilities and enhance device protection in the interconnected world.
Jumpstarter: Enabling Open Hardware-in-the-Loop Testing
Automate embedded software testing with Jumpstarter, integrating hardware-in-the-loop into CI/CD pipelines for faster, more consistent results. Explore the dutlink-board and its expandable functionality.
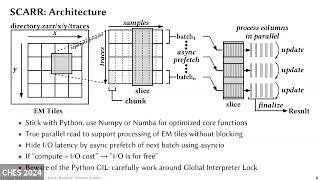
Hardware Security I - CHES 2024
Explore hardware security topics presented at CHES 2024, chaired by Jan Richter-Brockmann. Gain insights into cutting-edge research and developments in the field of cryptographic hardware and embedded systems.
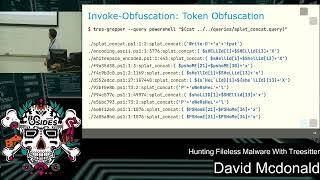
Hunting Fileless Malware with Treesitter
Explore advanced techniques for detecting obfuscated, fileless malware using Treesitter parser generator library. Learn to create scalable and accurate detections for malicious PowerShell and Bash payloads.
Fully Automated Power Measurement Solution with IC Temperature Control
Explore automated power measurement and temperature control for embedded Linux platforms, featuring innovative solutions for characterization and Operating Performance Points optimization.
Finding Vulnerabilities in Your Codebase Using Open Source Tools
Explore open-source tools for identifying vulnerabilities in your codebase. Learn effective techniques to enhance software security and protect against potential threats.
Radxa X2L - Low-Cost x86 SBC with RP2040 Review and Demo
Comprehensive review of Radxa X2L, an x86 single board computer with RP2040 microcontroller. Covers unboxing, specs, performance tests, and unique features like onboard Raspberry Pi Pico functionality.
Board Farm APIs for Automated Testing of Embedded Linux
Explore APIs for automated testing of embedded Linux systems, covering multi-device orchestration, hardware integration, and practical use cases with a live demonstration.
Nintendo DSi Hacking: Extracting Boot ROMs and New Jailbreak Methods - 37C3 2023
Exploración profunda del hackeo de Nintendo DSi: extracción de boot ROMs, nuevos jailbreaks y revivir consolas con chips NAND desgastados. Análisis técnico de explotación, inyección de fallos y criptografía.
A Beginner's Guide to Code Review
Learn essential code review techniques to identify vulnerabilities, practice with labs, and discover resources for finding code to review. Improve your skills in detecting and fixing security issues.