
Automating Testing with Intelligence - DIY Strategies for Success
Master intelligent test automation techniques using machine learning and AI to implement smart processes and enhance data-driven testing strategies.
Network Protocols and Their Impact on Application Performance
Explore how network protocol choices in microservices architecture impact system performance, reliability, and troubleshooting across application, transport, and system layers, with practical insights for optimization.
Securing AI-Generated Code: Challenges and Solutions for the Future
Explore the critical challenges and solutions for securing AI-generated code, featuring practical tools and research for building AI security engineering capabilities.
Hackers in Jurassic Park: When Attackers Find a Way
Explore real-world cybersecurity breaches through engaging hacking stories, drawing parallels with Jurassic Park to understand how attackers penetrate seemingly secure digital systems.
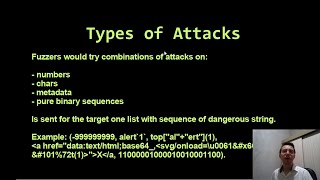
Fuzzing - Finding Your Own Bugs and Zero-Days
Master the art of fuzzer creation and vulnerability discovery, exploring buffer overflow exploitation techniques with hands-on demonstrations and practical exploit development strategies.
Security Tooling Space - Latest Developments and Innovations
Explore the latest developments and innovations in blockchain security tooling, focusing on emerging threats, defensive strategies, and cutting-edge solutions for smart contract protection.
New Isn't Always Novel - Finding Basic Vulnerabilities in Enterprise Software
Discover how basic vulnerabilities in enterprise software led to a successful Pwn2Own contest entry, featuring a command injection exploit in Lexmark printers and practical security insights.
Hacking War Stories: From Prison Systems to Tech Companies - A Series of Unfortunate Events
Dive into real-world hacking adventures, from prison systems to major tech companies, exploring identification, exploitation techniques, and potential impact across different organizational contexts.
Smashing the State Machine: Advanced Web Race Condition Attacks
Discover advanced web race-condition attack techniques, from limit-overrun exploits to state machine manipulation, with practical methodologies and tools for identifying and exploiting vulnerabilities.
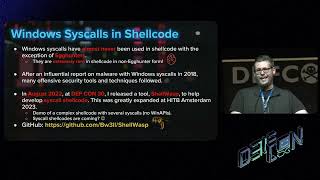
Game Changing Advances in Windows Shellcode Analysis Using SHAREM Framework
Discover groundbreaking advances in Windows shellcode analysis through SHAREM framework, offering enhanced emulation, complete code coverage, and superior disassembly capabilities for security professionals.
Malware Design: Abusing Legacy Microsoft Transports and Session Architecture
Explore advanced malware design techniques and covert communication frameworks, focusing on Windows architecture exploitation and maintaining persistent access while evading detection systems.
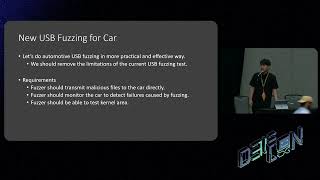
Automotive USB Fuzzing: Efficient Methods and Real-World Vulnerabilities
Dive into automotive USB fuzzing techniques and discover efficient methods for testing vehicle vulnerabilities through direct USB connections, featuring real-world case studies and practical demonstrations.
Taking Down Applications with Logic - DEF CON 31
Dive into advanced application security techniques and learn how logical vulnerabilities can be exploited to compromise web applications, demonstrated through real-world examples.
Hacking Apple's USB-C Controller: From JTAG Access to Code Execution on iPhone 15
Dive into advanced hardware hacking techniques to exploit Apple's ACE3 USB-C controller, using reverse engineering, side-channel analysis, and fault injection to gain code execution access on iPhone 15.
Inside Llama 3 Red Team Process - AI Safety and Security Assessment
Delve into Meta's AI Red Team's comprehensive approach to testing Llama 3's safety, exploring methodologies, automated attacks, and emerging security challenges in AI systems.
Reflections on a Decade in Bug Bounties - From Novice to Seasoned Hunter
Gain insights into the evolution of bug bounty hunting through a decade-long journey, from basic vulnerability reporting to crafting critical impact chains, with perspectives from both hunter and triage sides.
QuickShell: Remote Code Execution Attack Chain Analysis in Quick Share
Uncover critical security vulnerabilities in Google's Quick Share protocol, including an RCE attack chain, HTTPS MITM techniques, and protocol analysis for both Windows and Android platforms.
Xiaomi Mobile Security Vulnerabilities - Regional Exploit Analysis and Pwn2Own Competition
Delve into the behind-the-scenes journey of exploiting Xiaomi 13 Pro at Pwn2Own Toronto 2023, exploring regional security variations and the challenges of mobile device exploitation.
WHAD: A Framework for Wireless Protocol Hacking and Analysis
Discover WHAD, a versatile framework for wireless protocol hacking that enables hardware interoperability and simplified tool development for security researchers exploring wireless vulnerabilities.
Using Testcontainers for Better Integration Tests in Java Microservices
Discover how to create robust integration tests using Testcontainers framework, enabling independent testing of Java microservices with Docker-based infrastructure services like databases and message brokers.
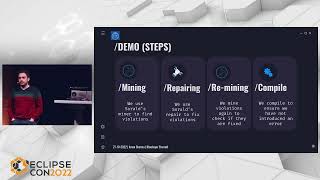
Automated Static Analysis Warning Resolution Using Software Bots - A Sorald Demo
Discover how to automate fixing SonarQube violations using Sorald, a software bot that monitors GitHub repositories and submits patches through pull requests, streamlining code maintenance.