Hack In The Studio - Fireside Chat
Fireside chat with security experts Cristofaro Mune and Adam Laurie, discussing their extensive experience in hardware hacking, embedded systems security, and reverse engineering techniques.
Reversing GO Binaries With Ghidra
Exploring techniques for reverse engineering Golang binaries using Ghidra, focusing on IoT malware analysis, overcoming Go-specific challenges, and addressing recent obfuscation trends.
Exploiting UAF by Ret2bpf in Android Kernel
Exploiting a 10-year-old Use-After-Free vulnerability in Android's xt_qtaguid kernel module, demonstrating local privilege escalation on Mi9 device using ret2bpf technique to bypass protections.
Rogue7 - Rogue Engineering-Station Attacks on S7 Simatic PLCs
Uncovers vulnerabilities in Siemens S7 PLC systems, demonstrating potential attacks on industrial control architectures despite claimed security measures and advanced cryptographic protocols.
Reverse Engineering the M1
Explore Apple's M1 chip architecture, including ARM variant quirks, memory access issues, and the AMX vector instruction set. Gain insights into reverse engineering proprietary hardware.
Apple Neural Engine Internal - From ML Algorithm to HW Registers
Explore the inner workings of Apple's Neural Engine, from machine learning algorithms to hardware registers, with insights into FaceID's neural network and SEP firmware security.
Anti-Forensics - Reverse Engineering a Leading Phone Forensic Tool
Explore vulnerabilities in Cellebrite UFED through reverse engineering, uncovering potential impacts on court cases and discussing the ethical implications of forensic software flaws.

Reverse Engineering WhatsApp Encryption for Chat Manipulation and More
Decrypting WhatsApp traffic and creating tools for vulnerability research, including a Burp Suite extension for investigating encrypted communications.
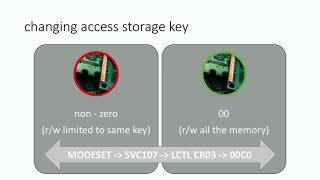
Mainframe Z-OS Reverse Engineering and Exploit Development
Explore mainframe security vulnerabilities, reverse engineering techniques, and exploit development for z/OS systems, challenging common assumptions about mainframe invulnerability.
Breaking Bootloaders on the Cheap
Reverse-engineering bootloaders of popular microcontrollers to assess vulnerabilities in readout protection, focusing on software-based attacks and critical flaws in specific chip families.
Trust in Apple's Secret Garden - Exploring and Reversing Apple's Continuity Protocol
Explore Apple's Continuity protocol, examining privacy and security implications of seamless device communication. Uncover potential vulnerabilities in AirDrop, iMessage, and other features within Apple's ecosystem.
Automation Techniques in C++ Reverse Engineering
Explore dynamic analysis techniques for C++ reverse engineering, focusing on structure usage and function argument types through DLL injection-based automation.
Beyond Root - Custom Firmware for Embedded Mobile Chipsets
Explore reverse engineering techniques to bypass protections and expand functionality of embedded mobile chipsets, going beyond traditional rooting methods for complete device control.
Reverse Engineering and Exploiting Font Rasterizers - The OpenType Saga
Explore critical vulnerabilities in OpenType font handling across popular software, revealing potential for arbitrary code execution and bypassing exploit mitigations. Learn about reverse-engineering techniques and in-depth vulnerability analysis.
Introduction to Reverse Engineering C++
Learn techniques for reverse engineering C++ programs, including analyzing compiled code, understanding memory layouts, and identifying key structures. Gain practical skills for software analysis and security research.
Pwning the Nerf Gun
Reversing and hijacking a remote-controlled Nerf tank gun through hardware, firmware, and RF analysis. Includes live demonstration of taking control and potentially shooting the conference organizer.
Reverse Engineering and Bug Hunting on KMDF Drivers
Explore reverse engineering and bug hunting techniques for KMDF drivers, focusing on entry points, IO queues, and implementation vulnerabilities. Gain practical skills for analyzing driver security.
Reverse Engineering Windows Malware 101 Workshop
Hands-on workshop introducing reverse engineering fundamentals for Windows malware analysis. Learn to set analysis goals, use tools, and apply computer science concepts through practical exercises.

So You Want to Hack Radios
Explore Software Defined Radio for hacking IoT devices. Learn digital signal processing basics and a reverse engineering workflow to recover and inject packets in proprietary wireless systems.
Hypervisor-Assisted Ring0 Debugging with Radare2
Explore hypervisor-assisted Ring0 debugging using radare2 for reverse engineering protected kernel-mode code, connecting to a virtual machine for direct memory access and analysis.
Lessons Learned Hunting IoT Malware
Explore IoT malware hunting techniques, honeypot designs, and real-world case studies. Learn reverse-engineering strategies for embedded systems and gain insights into next-generation threat detection.