Reverse Engineering Tutorials
Explore Android app reverse engineering techniques, from decompilation to vulnerability detection, using tools like GHIDRA for software analysis and security testing.
Current Malware Analysis
Comprehensive malware analysis techniques covering tools, unpacking methods, and real-world examples for cybersecurity professionals and enthusiasts.
Reverse Engineering and Malware Analysis
Learn essential reverse engineering and malware analysis skills using Ghidra, including crackme challenges, WannaCry analysis, and malware detection with Sysinternals Process Explorer.
Malware Analysis With Ghidra - Stuxnet Analysis
Explore Ghidra's features for malware analysis through a hands-on examination of Stuxnet, demonstrating reverse engineering techniques and tool capabilities.
Hacking Hardware - Samy Kamkar
Explore hardware hacking techniques, from credit card manipulation to wireless keyboard emulation, with insights on cryptography, fault injection, and firmware reverse engineering tools.
Ghidra Setup and Intro
Learn to set up and use Ghidra, a powerful reverse engineering tool. Explore file import, code browsing, decompilation, and memory mapping through hands-on examples.
Reverse Engineering with Ghidra
Explore software reverse engineering fundamentals, x86_64 architecture, and Ghidra basics in this comprehensive introduction to analyzing and understanding compiled code.
Reverse Engineering with Ghidra - Class 4
Explore advanced Ghidra features: external libraries, patch diffing, checksums, memory management, PCODE, SLEIGH, extensions, and scripting for enhanced reverse engineering capabilities.
Reverse Engineering with Ghidra - Class 3
Explore advanced reverse engineering techniques using Ghidra, covering structs, pointers, enums, system calls, and file operations. Gain practical tips for efficient analysis and code manipulation.
Reverse Engineering with Ghidra
Dive deep into assembly language concepts for reverse engineering, covering control flow, loops, variables, functions, and memory management using the Ghidra software suite.

Software Reverse Engineering with Ghidra - NSA Codebreaker Challenge Demo
Explore NSA's Ghidra platform for software reverse engineering through a hands-on demonstration solving real-world challenges and learning basic features.
Leveling Up Ghidra - Learn Ghidra Plugins with Game Boy Game Reverse Engineering
Explore Ghidra plugin development for efficient reverse engineering, using Game Boy games as an engaging example to showcase automation possibilities and enhance RE skills.
Taking Ghidra to the Next Level
Enhancing Ghidra: BinCraft's modernization efforts, improved decompilation, and integration of advanced techniques like GraalVM for a more powerful reverse engineering tool.
A Look at Jython-Enhanced Reverse Engineering with Ghidra
Explore Jython scripting in Ghidra for efficient malware analysis, using real-world examples to enhance reverse engineering techniques and streamline the process of analyzing obfuscated binaries.
Automating Binary Analysis with Ghidra's P-Code
Explore automated binary analysis using Ghidra's P-Code, an intermediate language that enables architecture-independent scripting for reverse engineering and vulnerability research.
Static Binary Analysis - The Essentials
Dive into reverse engineering and static malware analysis essentials with Igor Kuznetsov. Learn visual inspection, disassembly techniques, and structure analysis using IDA Pro and Ghidra.
Feeding Gophers to Ghidra
Improve Golang binary analysis in Ghidra with Java-based scripts. Recover strings, functions, and types for efficient malware research and vulnerability detection.
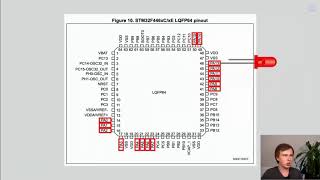
Firmware Hacking With Ghidra
Hands-on firmware hacking workshop using Ghidra for reverse engineering ARM Cortex-M architecture, followed by live demonstration of hardware glitching attacks on microcontrollers.
Reversing GO Binaries With Ghidra
Exploring techniques for reverse engineering Golang binaries using Ghidra, focusing on IoT malware analysis, overcoming Go-specific challenges, and addressing recent obfuscation trends.
Ghidriff
Explore ghidriff, an open-source Python package for efficient binary diffing using Ghidra. Learn about its command-line interface, function matching heuristics, and markdown output for simplified patch analysis and vulnerability research.
No Symbols When Reversing? No Problem - Bring Your Own Symbols for Binary Analysis
Discover efficient techniques for analyzing unknown functions in binaries, focusing on portable symbol creation and management using Ghidra, with practical examples from Golang-based malware analysis.