Control Flow Graph Reconstruction from EVM Bytecode
Dive into advanced techniques for reconstructing control flow graphs from Ethereum Virtual Machine bytecode, exploring core concepts and practical applications.
Reverse Engineering Demystified - OISF 2013
Explore reverse engineering techniques, from source code analysis to binary disassembly. Learn about vulnerability discovery, static and dynamic approaches, and overcoming obstacles in software analysis.
Writing a New Decompiler for JRuby Security Audits
Explore JRuby vulnerabilities and learn about YBurj, a new open-source decompiler for JRuby IR, enabling recovery of compiled source code for enhanced security audits.

Software Reverse Engineering with Ghidra - NSA Codebreaker Challenge Demo
Explore NSA's Ghidra platform for software reverse engineering through a hands-on demonstration solving real-world challenges and learning basic features.

Securing Mobile App Secrets: Preventing Credential Leaks in Android Applications
Explore how mobile apps leak sensitive credentials, analyze real-life breaches, and learn actionable steps to prevent secrets from being exposed in source code and compiled applications.
Locating Vulnerabilities in Ethereum Smart Contracts - Hybrid Analysis Method
Explore a hybrid analysis method combining smart contract decompilation and EVM simulation to identify vulnerabilities in Ethereum projects, with practical demonstrations and insights.
Taking Ghidra to the Next Level
Enhancing Ghidra: BinCraft's modernization efforts, improved decompilation, and integration of advanced techniques like GraalVM for a more powerful reverse engineering tool.
Decompiler Internals - Microcode
Explore the intermediate language used in Hex-Rays Decompiler, its simplicity and power in representing programs, and plans for publication and programmatic access.
Kotlin - Uncovered
Explore Kotlin's inner workings by decompiling to Java, examining data classes, lambdas, and delegation to gain deeper understanding and tools for further investigation.
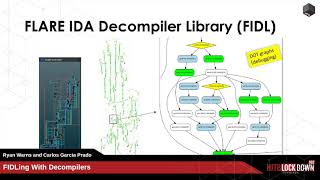
FIDLing with Decompilers
Explore decompilation basics, popular tools, and the Hex-Rays Decompiler. Learn about FIDL, a new library simplifying decompiler API usage, with practical examples and demos.
Decompiler Internals - Microcode
Explore the intermediate language used in Hex-Rays Decompiler, understanding its simplicity and power in representing complex programs.
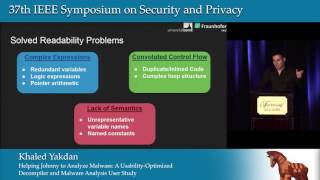
Helping Johnny to Analyze Malware - A Usability-Optimized Decompiler and Malware Analysis User Study
Explore a usability-optimized decompiler for malware analysis, featuring readability improvements that significantly enhance analysts' ability to understand and combat complex malicious software.
Detecting Bugs Using Decompilation and Data Flow Analysis
Explore Bugwise, a free online service for detecting software bugs through decompilation and data flow analysis, showcasing its success in finding vulnerabilities in Debian Linux.
Unleashing the Power of Decompilation for x86 Deep Neural Network Executables
Explore BTD, a decompiler for deep neural network executables, enabling reverse engineering of compiled DL models on various hardware platforms to enhance security and transparency.

Reverse Engineering Python Binaries - There and Back Again
Uncover Python bytecode secrets: Learn to interpret and decompile .pyc files, explore challenges in automated decompilation, and gain insights into recovering source code from bytecode.
Lost and Found in Translation - An Intro to ML Assisted Decompilation and Deobfuscation
Explore ML-assisted decompilation and deobfuscation, covering large language models, neural machine translation, and their applications in reverse engineering and security auditing.
Reverse Engineering Python Binaries - There and Back Again
Uncover Python bytecode secrets: Learn to interpret and decompile .pyc files, explore challenges in automated decompilation, and gain insights into recovering source code from bytecode.

Black Hat Asia 2025
Black Hat Asia 2025

Black Hat Europe 2022
Black Hat Europe 2022